2016
#
AWS re:Invent 2016: Lessons Learned from a Year of Using Spot Fleet (CMP205) - YouTube
Yelp talk about their Spot Fleet price optimization autoscaler app, FleetMiser
#
4 Wi-Fi Tips from Former Apple Wi-Fi Engineer
Good tips: use the same SSID for all radios; deal with congestion with more APs using less power; don't use "Wide" channels on 2.4Ghz; and place antennae perpendicular to each other.
#
The hidden cost of QUIC and TOU
The recent movement to get all traffic encrypted has of course been great for the Internet. But the use of encryption in these protocols is different than in TLS. In TLS, the goal was to ensure the privacy and integrity of the payload. It's almost axiomatic that third parties should not be able to read or modify the web page you're loading over HTTPS. QUIC and TOU go further. They encrypt the control information, not just the payload. This provides no meaningful privacy or security benefits. Instead the apparent goal is to break the back of middleboxes [0]. The idea is that TCP can't evolve due to middleboxes and is pretty much fully ossified. They interfere with connections in all kinds of ways, like stripping away unknown TCP options or dropping packets with unknown TCP options or with specific rare TCP flags set. The possibilities for breakage are endless, and any protocol extensions have to jump through a lot of hoops to try to minimize the damage.
quic tou protocols http tls security internet crypto privacy firewalls debugging operability
#
Slicer: Auto-sharding for datacenter applications
Paper from Google describing one of their internal building block services:
A general purpose sharding service. I normally think of sharding as something that happens within a (typically data) service, not as a general purpose infrastructure service. What exactly is Slicer then? It has two key components: a data plane that acts as an affinity-aware load balancer, with affinity managed based on application-specified keys; and a control plane that monitors load and instructs applications processes as to which keys they should be serving at any one point in time. In this way, the decisions regarding how to balance keys across application instances can be outsourced to the Slicer service rather than building this logic over and over again for each individual back-end service. Slicer is focused exclusively on the problem of balancing load across a given set of backend tasks, other systems are responsible for adding and removing tasks.
interesting.Cherami: Uber Engineering's Durable and Scalable Task Queue in Go - Uber Engineering Blog
a competing-consumer messaging queue that is durable, fault-tolerant, highly available and scalable. We achieve durability and fault-tolerance by replicating messages across storage hosts, and high availability by leveraging the append-only property of messaging queues and choosing eventual consistency as our basic model. Cherami is also scalable, as the design does not have single bottleneck. [...] Cherami is completely written in Go, a language that makes building highly performant and concurrent system software a lot of fun. Additionally, Cherami uses several libraries that Uber has already open sourced: TChannel for RPC and Ringpop for health checking and group membership. Cherami depends on several third-party open source technologies: Cassandra for metadata storage, RocksDB for message storage, and many other third-party Go packages that are available on GitHub. We plan to open source Cherami in the near future.
cherami uber queueing tasks queues architecture scalability go cassandra rocksdb
The Perfect Weapon: How Russian Cyberpower Invaded the U.S. - The New York Times
This is scary shit. It's amazing how Russia has weaponised transparency, but I guess it's not new to observers of "kompromat": https://en.wikipedia.org/wiki/Kompromat
kompromat russia cyberpower cyberwar security trump us-politics dnc
#
Did the Russians "hack" the election? A look at the established facts | Ars Technica
solid roundup. There's a whole lot of evidence pointing Russia's way, basically
#
-
good preso from Percona Live 2015 on the messiness of MySQL vs UTF-8 and utf8mb4
utf-8 utf8mb4 mysql storage databases slides booking.com character-sets
-
A new data structure for accurate on-line accumulation of rank-based statistics such as quantiles and trimmed means. The t-digest algorithm is also very parallel friendly making it useful in map-reduce and parallel streaming applications. The t-digest construction algorithm uses a variant of 1-dimensional k-means clustering to product a data structure that is related to the Q-digest. This t-digest data structure can be used to estimate quantiles or compute other rank statistics. The advantage of the t-digest over the Q-digest is that the t-digest can handle floating point values while the Q-digest is limited to integers. With small changes, the t-digest can handle any values from any ordered set that has something akin to a mean. The accuracy of quantile estimates produced by t-digests can be orders of magnitude more accurate than those produced by Q-digests in spite of the fact that t-digests are more compact when stored on disk.
Super-nice feature is that it's mergeable, so amenable to parallel usage across multiple hosts if required. Java implementation, ASL licensing.data-structures algorithms java t-digest statistics quantiles percentiles aggregation digests estimation ranking
#
A Yale history professor's 20-point guide to defending democracy under a Trump presidency — Quartz
Good advice -- let's hope it doesn't come to this. Example: '17. Watch out for the paramilitaries: When the men with guns who have always claimed to be against the system start wearing uniforms and marching around with torches and pictures of a Leader, the end is nigh. When the pro-Leader paramilitary and the official police and military intermingle, the game is over.'
trump activism government politics us-politics right-wing history hitler nazis fascism
Commentary: The 'Irish' Startup Attribution Problem
Why don't Irish tech startup activity show up on a EU-wide comparisons? Turns out we tend to transition to a US-based model, with US-based management and EU-based operations and engineering, like $work does:
Successful Irish tech companies have a skewed geographic profile. This presents a data gathering problem for the data companies but its also a strong indicator of the market reality for Irish startups. The size of the local market and a focus on software business in particular means many Irish startups are transitioning to the US (some earlier and with more commitment than others), and getting backed by a spectrum of local and international VCs.
Correcting for this put Ireland's tech venture investment in the second half of 2014 at $125m, midway between Sweden and Finland, 8th in Europe overall.
#
Hi-tech caves bring prehistoric Sistine chapel back to life
ooh, Lascaux 4 is finally opening:
St-Cyr added: "It's impossible for anyone to see the original now, but this is the next best thing. What is lost in not having the real thing is balanced by the fact people can see so much more of the detail of the wonderful paintings and engravings."
#
Contactless credit cards vulnerable to a range of scams
Johanson said it's possible to use an RFID "gate antenna" — two electronic readers spanning a doorway, similar to the anti-theft gates in retail stores — to scan the credit cards of people passing through. With enough high-powered gates installed at key doorways in a city or across the country, someone could collect comprehensive information on people's movements, buying habits and social patterns. "These days you can buy a $500 antenna to mount in doorways that can read every card that goes through it," Johanson said.
Amazingly, these seem to be rife with holes -- they still use the legacy EMV protocol, do not require online verification with backend systems, and allow replay attacks. A Journal.ie article today claims that attackers are sniffing EMV data, then replaying it against card readers in shops in Dublin, which while it may not be true, the attack certainly seems viable...rfid security scams emv wireless contactless credit-cards replay-attacks
Counterfeit Macbook charger teardown: convincing outside but dangerous inside
rather dramatic differences
apple macbook chargers components hardware clones counterfeit
#
Trump's lies have a purpose. They are an assault on democracy
Donald Trump's media strategy as a form of Surkovian control via post-truth 'destabilised perception', through deliberate flooding with fake news:
By attacking the very notion of shared reality, the president-elect is making normal democratic politics impossible. When the truth is little more than an arbitrary personal decision, there is no common ground to be reached and no incentive to look for it. To men like Surkov, that is exactly as it should be. Government policy should not be set through democratic oversight; instead, the government should "manage" democracy, ensuring that people can express themselves without having any influence over the machinations of the state. According to a 2011 openDemocracy article by Richard Sakwa, a professor of Russian and European politics at the University of Kent, Surkov is "considered the main architect of what is colloquially known as 'managed democracy,' the administrative management of party and electoral politics." "Surkov's philosophy is that there is no real freedom in the world, and that all democracies are managed democracies, so the key to success is to influence people, to give them the illusion that they are free, whereas in fact they are managed," writes Sakwa. "In his view, the only freedom is 'artistic freedom.'"
post-truth lies donald-trump surkov breitbart pr media news propaganda fake-news
#
PayWave & PayPass deletion via RFID antenna kill
remove RFID from a payment card with a single drilled hole
Fast Forward Labs: Probabilistic Data Structure Showdown: Cuckoo Filters vs. Bloom Filters
Nice comparison of a counting Bloom filter and a Cuckoo Filter, implemented in Python:
This post provides an update by exploring Cuckoo filters, a new probabilistic data structure that improves upon the standard Bloom filter. The Cuckoo filter provides a few advantages: 1) it enables dynamic deletion and addition of items 2) it can be easily implemented compared to Bloom filter variants with similar capabilities, and 3) for similar space constraints, the Cuckoo filter provides lower false positives, particularly at lower capacities. We provide a python implementation of the Cuckoo filter here, and compare it to a counting Bloom filter (a Bloom filter variant).
algorithms probabilistic approximation bloom-filters cuckoo-filters sets estimation python
#
-
Football Manager includes what is effectively a parallel universe, so they modelled the effects of Brexit on the UK Premier League: 'In my own current "save", Brexit kicked in at the end of season three. Unfortunately I got one of the hard options, where all non-homegrown players are now going through a work permit system, albeit one that's slightly relaxed. It means I can no longer bring in that 19-year-old Italian keeper I'd been eyeing up as one for the future. Instead I have to wait for him to break into the Italian squad, and play 30% of their fixtures over the next two years. Then he'll be mine. Meanwhile, my TV revenue has just dropped by a few million. Let's hope that doesn't continue, or I won't even be able to afford him.'
brexit uk games gaming football-manager forecasts simulation
Accidentally Quadratic — Rust hash iteration+reinsertion
It was recently discovered that some surprising operations on Rust's standard hash table types could go quadratic.
Quite a nice unexpected accidental detour into O(n^2)big-o hashing robin-hood-hashing siphash algorithms hashtables rust
Reproducible research: Stripe's approach to data science
This is intriguing -- using Jupyter notebooks to embody data analysis work, and ensure it's reproducible, which brings better rigour similarly to how unit tests improve coding. I must try this.
Reproducibility makes data science at Stripe feel like working on GitHub, where anyone can obtain and extend others' work. Instead of islands of analysis, we share our research in a central repository of knowledge. This makes it dramatically easier for anyone on our team to work with our data science research, encouraging independent exploration. We approach our analyses with the same rigor we apply to production code: our reports feel more like finished products, research is fleshed out and easy to understand, and there are clear programmatic steps from start to finish for every analysis.
stripe coding data-science reproducability science jupyter notebooks analysis data experiments
Introducing Veneur: high performance and global aggregation for Datadog
neat -- aggregation of histograms for Datadog statsd
#
-
auditd -> go-audit -> elasticsearch at Slack
Irish eyes are crying: Tens of thousands of broadband modems wide open to hijacking
Eir ship vulnerable firmware images AGAIN. ffs
"Solving Imaginary Scaling Issues" ... "At Scale"
Amazing virtuoso performance -- be sure to scroll up all the way to Chapter 1
Webhooks do's and dont's: what we learned after integrating +100 APIs
interesting tips
#
Dynamically Scale Applications on Amazon EMR with Auto Scaling
good call -- new EMR feature
Testing@LMAX – Time Travel and the TARDIS
LMAX' approach to acceptance/system-testing time-dependent code. We are doing something similar in Swrve too, so finding that LMAX have taken a similar approach is a great indicator
Heineken refreshed by 'craft beer' ruling
scumbags. Attempting to pass off their pissy beer under alternative names to con consumers into buying it! 'There will be no sanctions against Heineken for passing off non-craft beer as "locally produced", the Food Safety Authority of Ireland (FSAI) has said. The FSAI and HSE launched a joint investigation last month after it emerged that Heineken Ireland had sold some of its products, including Foster's lager, under craft-type names such as Blasket Blonde and Beanntrai Bru. Two well-known stouts, Beamish and Murphy's, were also sold under craft-type names by the international brewing giant. C&C, a Tipperary-based drinks company, was also investigated after it admitted selling its Clonmel 1650 lager under a different name, Pana Cork, in Cork.'
#
Simple Queue Service FIFO Queues with Exactly-Once Processing & Deduplication
great, I've looked for this so many times. Only tricky limit I can spot is the 300 tps limit, and it's US-East/US-West only for now
"Get In Control Of Your Workflows With Airflow"
good intro to Airflow usage preso
Etsy Debriefing Facilitation Guide
by John Allspaw, Morgan Evans and Daniel Schauenberg; the Etsy blameless postmortem style crystallized into a detailed 27-page PDF ebook
-
'bike-shedding', or needless arguing about trivial issues, actually dates back to 1957 as C. Northcote Parkinson's 'law of triviality'
triviality bikeshed bikeshedding management arguments decisions history
#
Julia Evans reverse engineers Skyliner.io
simple usage of Docker, blue/green deploys, and AWS ALBs
docker alb aws ec2 blue-green-deploys deployment ops tools skyliner via:jgilbert
IPBill ICRs are the perfect material for 21st-century blackmail
ICRs are the perfect material for blackmail, which makes them valuable in a way that traditional telephone records are not. And where potentially large sums of money are involved, corruption is sure to follow. Even if ICR databases are secured with the best available technology, they are still vulnerable to subversion by individuals whose jobs give them ready access. This is no theoretical risk. Just one day ago, it emerged that corrupt insiders at offshore call centres used by Australian telecoms were offering to sell phone records, home addresses, and other private details of customers. Significantly, the price requested was more if the target was an Australian "VIP, politician, police [or] celebrity."
blackmail privacy uk-politics uk snooping surveillance icrs australia phone-records
#
Docklands Print Commission 2016: Colin Martin
I love Colin's work. just may spring for this one
#
-
a low-cost online vendor in Ireland, recommended by @irldexter on ITS (along with webdoctor.ie): 'For basic consultations I halved the cost €55 to engage a GP with https://www.webdoctor.ie/ down to €25 (for limited domains) and after paying €8.48 and €9.48 respectively for a Ventolin inhaler, I now get them for €3.50 at http://www.purepharmacy.ie/ (closer to mainland EU costs). I also benchmarked my parents medicine costs which worked out 40% cheaper too.'
#
Rents dwarf Celtic Tiger era with 'disastrous effect' on society
"The scale of the challenge here remains depressing," says the report. "It has never been viable to build apartment blocks in the vast majority of this country." [...] The report notes that the rise in living costs of almost three quarters in less than five years is "a symptom of strong demand for housing" as economic recovery continues and the population grows. "But there is nothing inevitable about housing costs rising with demand," it says. "That only happens when supply fails to respond, and the complete absence of any meaningful level of construction over the past five years is a systemic failure in desperate need of policy solutions. "There is no more urgent task facing the Minister for Housing, his department and advisers, and the Housing Agency, than understanding why the costs of building, and building apartments in particular, is so dramatically out of line with our own incomes and indeed with the cost in other countries."
-
I'm not remotely interested in shockingly good graphics, in murder simulators, in guns and knives and swords. I'm not that interested in adrenaline. My own life is thrilling enough. There is enough fear and hatred in the world to get my heart pounding. My Facebook feed and Twitter feed are enough for that. Walking outside in summer clothing is enough for that. I'm interested in care, in characters, in creation, in finding a path forward inside games that helps me find my path forward in life. I am interested in compassion and understanding. I'm interested in connecting. As Miranda July said, "all I ever wanted to know is how other people are making it through life." I want to make games that help other people understand life. We are all overwhelmed with shock, with information, with change. The degree of interactivity in our lives is amazing and wonderful and I wouldn't exchange it for anything, but it is also shocking and overwhelming and it's causing us to dig in and try to find some peace by shutting each other out. On all sides of the political spectrum we've stopped listening to each other and I fear we are all leaning toward fascist thinking. We should be using this medium to help us adapt to our new, interactive lives. This is how we become relevant.
#
Tesco Bank: 20,000 customers lose money - BBC News
"Any financial loss that results from this fraudulent activity will be borne by the bank," Mr Higgins said. "Customers are not at financial risk."
Well, that would be surprising....-
Hooray for nuclear power. (via Ossian Smyth)
-
Ivan's Childhood, Andrei Rublev, Solaris, The Mirror, and Stalker -- all viewable for free on YouTube thanks to Mosfilm. quality not great though....
#
Jeff Erickson's Algorithms, Etc.
This page contains lecture notes and other course materials for various algorithms classes I have taught at the University of Illinois, Urbana-Champaign. The notes are numbered in the order I cover the material in a typical undergraduate class, wtih notes on more advanced material (indicated by the symbol ?) interspersed appropriately. [...] In addition to the algorithms notes I have been maintaining since 1999, this page also contains new notes on "Models of Computation", which cover a small subset of the material normally taught in undergraduate courses in formal languages and automata. I wrote these notes for a new junior-level course on "Algorithms and Models of Computation" that Lenny Pitt and I developed, which is now required for all undergraduate computer science and computer engineering majors at UIUC.
Via Tony Finch
#
How Macedonia Became A Global Hub For Pro-Trump Misinformation - BuzzFeed News
"I started the site for a easy way to make money," said a 17-year-old who runs a site [from Veles] with four other people. "In Macedonia the economy is very weak and teenagers are not allowed to work, so we need to find creative ways to make some money. I'm a musician but I can't afford music gear. Here in Macedonia the revenue from a small site is enough to afford many things."
macedonia veles scams facebook misinformation donald-trump us-politics
#
-
'an antagonistic GSM base station [disguised] in the form of an innocuous office printer. It brings the covert design practice of disguising cellular infrastructure as other things - like trees and lamp-posts - indoors, while mimicking technology used by police and intelligence agencies to surveil mobile phone users.'
gsm hardware art privacy surveillance hacks printers mobile-phones
Testing Docker multi-host network performance - Percona Database Performance Blog
wow, Docker Swarm looks like a turkey right now if performance is important. Only "host" gives reasonably perf numbers
docker networking performance ops benchmarks testing swarm overlay calico weave bridge
-
Subreddit devoted to becoming a software developer in Ireland, with a decent wiki
Great comment on the "realism" of space photos
In short, the answer to the question "is this what it would look like if I was there?" is almost always no, but that is true of every photograph. The photos taken from space cameras are no more fake or false than the photos taken from any camera. Like all photos they are a visual interpretation using color to display data. Most space photos have information online about how they were created, what filters were used, and all kinds of interesting details about processing. The discussion about whether a space photo is real or fake is meaningless. There's no distinction between photoshopped and not. It's a nuanced view but the nature of the situation demands it.
photography photos space cassini probes cameras light wavelengths science vision realism real
#
-
LOL as DST bug uncovers spurious automated noise complaints:
In January last year the airport unearthed a scheme whereby campaigners were using automated software to generate complaints against the airport. Officials caught out the set-up when the two anti-Heathrow enthusiasts forgot to take into account the hour going back in October, and began complaining about flights that had not yet taken off or arrived.
bugs dst daylight-savings-time funny heathrow complaints automation noise
Facebook scuppers Admiral Insurance plan to base premiums on your posts
Well, this is amazingly awful:
The Guardian claims to have further details of the kind of tell-tale signs that Admiral's algorithmic analysis would have looked out for in Facebook posts. Good traits include "writing in short concrete sentences, using lists, and arranging to meet friends at a set time and place, rather than just 'tonight'." On the other hand, "evidence that the Facebook user might be overconfident—such as the use of exclamation marks and the frequent use of 'always' or 'never' rather than 'maybe'—will count against them."
The future is shitty.insurance facebook scoring computer-says-no algorithms text-analysis awful future
MemC3: Compact and concurrent Memcache with dumber caching and smarter hashing
An improved hashing algorithm called optimistic cuckoo hashing, and a CLOCK-based eviction algorithm that works in tandem with it. They are evaluated in the context of Memcached, where combined they give up to a 30% memory usage reduction and up to a 3x improvement in queries per second as compared to the default Memcached implementation on read-heavy workloads with small objects (as is typified by Facebook workloads).
memcached performance key-value-stores storage databases cuckoo-hashing algorithms concurrency caching cache-eviction memory throughput
#
Total Nightmare: USB-C and Thunderbolt 3
the coming incompatibility nightmare of USB-C cabling
Amazon ElastiCache for Redis Update – Sharded Clusters, Engine Improvements, and More | AWS Blog
Elasticache now supports sharding
-
The square root staffing law is a rule of thumb derived from queueing theory, useful for getting an estimate of the capacity you might need to serve an increased amount of traffic.
ops capacity planning rules-of-thumb qed-regime efficiency architecture
Measuring Docker IO overhead - Percona Database Performance Blog
See also https://www.percona.com/blog/2016/02/05/measuring-docker-cpu-network-overhead/ for the CPU/Network equivalent. The good news is that nowadays it's virtually 0 when the correct settings are used
docker percona overhead mysql deployment performance ops containers
React's license: necessary and open?
Luis Villa: 'Is the React license elegant? No. Should you be worried about using it? Probably not. If anything, Facebook's attempt to give users an explicit patent license should probably be seen as a good faith gesture that builds some confidence in their ecosystem. But yeah, don't use it if your company intends to invest heavily in React and also sue Facebook over unrelated patents. That… would be dumb. :)'
luis-villa open-source react facebook patents swpats licensing licenses bsd
-
Writeup of their Consul-based service discovery system, a bit similar to smartstack. Good description of the production problems that they saw with Consul too, and also they figured out that strong consistency isn't actually what you want in a service discovery system ;) HN comments are good too: https://news.ycombinator.com/item?id=12840803
consul api microservices service-discovery dns load-balancing l7 tcp distcomp smartstack stripe cap-theorem scalability
#
Here's Why Facebook's Trending Algorithm Keeps Promoting Fake News - BuzzFeed News
Kalina Bontcheva leads the EU-funded PHEME project working to compute the veracity of social media content. She said reducing the amount of human oversight for Trending heightens the likelihood of failures, and of the algorithm being fooled by people trying to game it. "I think people are always going to try and outsmart these algorithms — we've seen this with search engine optimization," she said. "I'm sure that once in a while there is going to be a very high-profile failure." Less human oversight means more reliance on the algorithm, which creates a new set of concerns, according to Kate Starbird, an assistant professor at the University of Washington who has been using machine learning and other technology to evaluate the accuracy of rumors and information during events such as the Boston bombings. "[Facebook is] making an assumption that we're more comfortable with a machine being biased than with a human being biased, because people don't understand machines as well," she said.
facebook news gaming adversarial-classification pheme truth social-media algorithms ml machine-learning media
#
seriot.ch - Parsing JSON is a Minefield ????
Crockford chose not to version [the] JSON definition: 'Probably the boldest design decision I made was to not put a version number on JSON so there is no mechanism for revising it. We are stuck with JSON: whatever it is in its current form, that's it.' Yet JSON is defined in at least six different documents.
"Boldest". ffs. :facepalm:bold courage json parsing coding data formats interchange fail standards confusion
mjg59 | Fixing the IoT isn't going to be easy
We can't easily fix the already broken devices, we can't easily stop more broken devices from being shipped and we can't easily guarantee that we can fix future devices that end up broken. The only solution I see working at all is to require ISPs to cut people off, and that's going to involve a great deal of pain. The harsh reality is that this is almost certainly just the tip of the iceberg, and things are going to get much worse before they get any better.
#
-
This is shocking:
At the end of the panel on artificial intelligence, a young black woman asked [Sebastian Thrun, CEO of the education startup Udacity, who is best known for founding Google X] whether bias in machine learning "could perpetuate structural inequality at a velocity much greater than perhaps humans can." She offered the example of criminal justice, where "you have a machine learning tool that can identify criminals, and criminals may disproportionately be black because of other issues that have nothing to do with the intrinsic nature of these people, so the machine learns that black people are criminals, and that's not necessarily the outcome that I think we want." In his reply, Thrun made it sound like her concern was one about political correctness, not unconscious bias. "Statistically what the machines do pick up are patterns and sometimes we don't like these patterns. Sometimes they're not politically correct," Thrun said. "When we apply machine learning methods sometimes the truth we learn really surprises us, to be honest, and I think it's good to have a dialogue about this."
"the truth"! Jesus. We are fuckedgoogle googlex bias racism implicit-bias machine-learning ml sebastian-thrun udacity inequality policing crime
#
-
Holy shit.
Using a proxy, remove "securityQuestion0" and "securityQuestion1" from the post data.
Massive facepalm. -
amazing architectural-oddities Tumblr (via Present and Correct)
-
I've had the privilege of experiencing a few different management levels (responsibilities? jobs?) at Etsy since I've joined. At each stage, I felt like the job of being a manager totally changed. What I did day-to-day changed, what was hard about it changed, how I measured my own success changed, and though I feel like the experiences built on one another, it continues to be an enormous shift in brainpower each time the gig changes a bit. Given how intangible (and often hidden) management work can be, I've outlined some highlights of what my work has been like as a manager over the last four years. (Obvious, major caveat: this is just my experience, and there's lots in here that is unique to this particular work environment, hierarchy, requirements, and challenges!)
JG Ballard, on the "pram in the hall"
Cyril Connolly, the 50s critic and writer, said that the greatest enemy of creativity is the pram in the hall, but I think that was completely wrong. It was the enemy of a certain kind of dilettante life that he aspired to, the man of letters, but for the real novelist the pram in the hall is the greatest ally - it brings you up sharp and you realise what reality is all about. My children were a huge inspiration for me. Watching three young minds creating their separate worlds was a very enriching experience.
writing creativity jg-ballard quotes pram-in-the-hall children kids parenting biography
#
50% of American Adults Are in Police Facial-Recognition Databases
holy crap this is going to be a serious problem
facial-recognition ml algorithms policing us-politics future dystopia
Danger is Everwhere Docter Noel Zone Halloween costume
may need this, depending on kiddie preferences this year ;)
A Guide to Communication, Shotcalling, and Etiquette in Competitive Overwatch
Excellent post on team voice comms tactics. Many tips here
-
Love the 'decade of' dig at FB and Amazon -- 'we were doing it first' ;) Great details on how Google have built out and improved their DC networking. Includes a hint that they now use DCTCP (datacenter-optimized TCP congestion control) on their internal hosts....
datacenter google presentation networks networking via:irldexter ops sre clos-networks fabrics switching history datacenters
#
Cloudy Gamer: Playing Overwatch on Azure's new monster GPU instances
pretty amazing. full 60FPS, 2560x1600, everything on Epic quality, streaming from Azure, for $2 per hour
Anti-Brexit traitors outed on twitter
oh god this is funny. Louise Mensch and various UKIPpers fall for transparent pisstake involving "taking Article 50 out of the ring binder and shredding it. It now goes straight from 49 to 51" etc.
Image Synthesis from Yahoo's open_nsfw
What makes an image NSFW, according to Yahoo? I explore this question with a clever new visualization technique
Deep Dream applied to an NSFW classifier. This is a bit NSFW, as it happens
#
Sean O'Dowd on Twitter: "damn someone at apple needs a hug"
stack trace leads with a symbol called "_thereIsNoSadnessLikeTheDeathOfOptimism"
-
interesting presentation describing how to architect Airflow ETL setups; see also https://gtoonstra.github.io/etl-with-airflow/principles.html
#
_Airport Noise NIMBYism: An Empirical Investigation_
'Generally, a very small number of people account for a disproportionately high share of the total number of noise complaints. In 2015, for example, 6,852 of the 8,760 complaints submitted to Ronald Reagan Washington National Airport originated from one residence in the affluent Foxhall neighborhood of northwest Washington, DC. The residents of that particular house called Reagan National to express irritation about aircraft noise an average of almost 19 times per day during 2015.' Somebody needs help.
#
ETL best practices with Airflow
good advice on how to ETL
New Scientist: Home abortions are safe – we should let women do it themselves
the Women on Web approach is backed by a column in New Scientist: 'It's also safer than many other medicines that we are allowed to buy from pharmacies without a prescription, such as Viagra in the UK. So why can't women get abortion pills from pharmacies and manage the process themselves at home if they choose? It might sound radical but it's already widespread in countries where abortion is illegal, with women buying the pills from online pharmacies. While some countries, such as Poland, are trying to tighten their already strict abortion laws, the advent of mail-order abortion pills means the law is becoming almost irrelevant.'
new-scientist safety abortion pro-choice medicine mifepristone pills poland ireland repealthe8th
#
What $50 buys you at Huaqiangbei, the world's most fascinating electronics market
This is amazing -- what a wonderland! For instance:
Six dollars for: a GSM chipset, a CPU, an LCD screen, a battery, a PCB, a metal housing, a molded silicone watch band, a MicroUSB cable, and a box. And the labor to assemble and test all of that.
#
-
The UK's version of the POD database project was used by the Home Office to track immigrants for various reasons -- in other words, exactly the reasons why parents will choose not to provide that data
How One 19-Year-Old Illinois Man Is Distorting National Polling Averages - The New York Times
One "outlier" voter—a 19-year old black Trump supporter—was weighted so heavily that it shifted the whole poll significantly. Stats fail
statistics nytimes politics via:reddit donald-trump hilary-clinton polling panels polls
Kafka Streams - Scaling up or down
this is a nice zero-config scaling story -- good work Kafka Streams
Medium's DynamoDB Data Source for Apache Spark
nice approach
-
'a Mexican cerveza preparada made with beer, lime juice, and assorted sauces, spices, and peppers. It is served in a chilled, salt-rimmed glass. There are numerous variations of this beverage throughout Mexico and Latin America.'
-
a variation on the mimosa, with an IPA and grapefruit juice -- sounds like Brewdog's Elvis Juice
-
'This crisp, refreshing beer and ginger beer cocktail is a Cuban favorite, and it's super-simple to make.'
#
The "Alpha Wolf" notion is outmoded and incorrect
via Saladin Ahmed -- the scientist who coined the term abandoned it as useless years ago:
The concept of the alpha wolf is well ingrained in the popular wolf literature at least partly because of my book "The Wolf: Ecology and Behavior of an Endangered Species," written in 1968, published in 1970, republished in paperback in 1981, and currently still in print, despite my numerous pleas to the publisher to stop publishing it. Although most of the book's info is still accurate, much is outdated. We have learned more about wolves in the last 40 years then in all of previous history. One of the outdated pieces of information is the concept of the alpha wolf. "Alpha" implies competing with others and becoming top dog by winning a contest or battle. However, most wolves who lead packs achieved their position simply by mating and producing pups, which then became their pack. In other words they are merely breeders, or parents, and that's all we call them today, the "breeding male," "breeding female," or "male parent," "female parent," or the "adult male" or "adult female." In the rare packs that include more than one breeding animal, the "dominant breeder" can be called that, and any breeding daughter can be called a "subordinate breeder."
biology animals wolves alpha alpha-males mra science wolf-packs society competition parenting
The private monorail tunnel under North London
20km of private monorail owned and operated by the electricity grid, used to monitor and inspect one of the longest 400kV circuits in Europe
power monorail transport london underground tunnelling electricity cool
AWS latency comparison: API Gateway vs Lambda vs Bare EC2
ugh, 213ms mean response overhead
Airfixers - Hosting without the hassle
Full AirBnB property management service in Dublin
Mt. Gox had a chair worth $28,000
According to the bankruptcy documents, one of the assets listed is 'a chair worth 2,902,119JPY, or roughly $28,000USD.'
chairs funny mtgox scams bitcoin furniture assets bankruptcy
#
Ludicrous Patent of the Week: Rectangles on a computer screen
"Chinese internet giant Tencent" have been granted a USPTO patent for drawing a box on a screen.
boxes screen tencent patents uspto funny absurd swpats via:markdennehy
-
This is the new fear -- that FF/FG will accidentally and stupidly disengage Ireland from the EU as a side effect of trying to keep the UK happy and cross-border trade intact
#
How Fucked Up is Your Management?
Oh dear.
Score 1 "My management culture is fucked up" point for each of the following: We have an unlimited vacation policy; We don't do regular 1:1s, but we have open office hours/are super available if anyone wants to chat; We don't have a process for interviewing, we just hire awesome people when we meet them; We super care about diversity, but we don't want to lower the bar so we just hire the best person for the job even if it means diversity suffers; We don't have defined levels and career paths for our employees, we're a really flat org; We don't have formal managers for every staff member, everyone just gets their work done; We don't have, like, HR HR, but our recruiter/office manager/only female employee is super good if you want someone to talk to; We don't do performance improvement plans for employees that are struggling. We just have a super honest conversation about how they aren't a good fit and fire them; We would have some hard explaining to do if our salary list accidentally became public.
startups management culture work vacation hiring office-hours managers diversity careers hr
Google and Monotype launch Noto, an open-source typeface family for all the world's languages
Great font factoid: 'The name "Noto" comes from the little squares that show when a font is not supported by a computer. This are often referred to as "tofu", because of their shape, therefore the font is short for No Tofu.'
#
Simple testing can prevent most critical failures
Specifically, the following 3 classes of errors were implicated in 92% of the major production outages in this study and could have been caught with simple code review:
Error handlers that ignore errors (or just contain a log statement); error handlers with "TODO" or "FIXME" in the comment; and error handlers that catch an abstract exception type (e.g. Exception or Throwable in Java) and then take drastic action such as aborting the system.
(Interestingly, the latter was a particular favourite approach of some misplaced "fail fast"/"crash-only software design" dogma in Amazon. I wasn't a fan)fail-fast crash-only-software coding design bugs code-review review outages papers logging errors exceptions
#
We are witnessing nothing less than a Tory reformation | Rafael Behr | Opinion | The Guardian
An excellent explanation of what is going on in the UK right now. What a nightmare:
Finally there are the self-styled buccaneers of the free-trade seas. Boris Johnson would probably cast himself as Sir Walter Raleigh – polymath, wordsmith, adventurer. That leaves Liam Fox to play Sir Francis Drake, looking for domestic glory in global circumnavigation but seen from abroad as a pirate. This is all myth and fantasy, of course. But parties have always been sustained by internal mythologies, and the task of exiting the EU is so complicated and fraught with danger that fantasy becomes a necessary comfort. As one former minister says of the puritan choristers: "They have spent their lives working towards this dream. Of course they don't want to accept that it's a nightmare." Tory pro-Europeans are in the impossible position of using rational argument against faith. If they counsel compromise on migration or the single market, they are accused of talking Britain down or trying to refight the referendum. They have few reinforcements across the political water. Labour is a shambles. The Lib Dems are puny in parliament. Scotland has its own distinct politics, and in Nicola Sturgeon its own remainian queen with her own independence agenda. The Tories do not speak for all of England, but in the absence of credible opposition they feel as if they do, and will act accordingly. To those millions who did not vote to leave the EU, the message is clear: you are free to pray for whatever you like. Your antique rites will be tolerated. But do not expect your concerns to be represented in the court of Queen Theresa. Be humble instead. Swallow your doubts and take a pew in the reformed national church of Brexit.
-
Martin Fowler's take on the 4 kinds of tech debt
programming design tech-debt technical-debt deadlines product ship
#
Charity Majors responds to the CleverTap Mongo outage war story
This is a great blog post, spot on:
You can't just go "dudes it's faster" and jump off a cliff. This shit is basic. Test real production workloads. Have a rollback plan. (Not for *10 days* … try a month or two.)
The only thing I'd nitpick on is that it's all very well to say "buy my book" or "come see me talk at Blahcon", but a good blog post or webpage would be thousands of times more useful.databases stateful-services services ops mongodb charity-majors rollback state storage testing dba
Remarks at the SASE Panel On The Moral Economy of Tech
Excellent talk. I love this analogy for ML applied to real-world data which affects people:
Treating the world as software promotes fantasies of control. And the best kind of control is control without responsibility. Our unique position as authors of software used by millions gives us power, but we don't accept that this should make us accountable. We're programmers—who else is going to write the software that runs the world? To put it plainly, we are surprised that people seem to get mad at us for trying to help. Fortunately we are smart people and have found a way out of this predicament. Instead of relying on algorithms, which we can be accused of manipulating for our benefit, we have turned to machine learning, an ingenious way of disclaiming responsibility for anything. Machine learning is like money laundering for bias. It's a clean, mathematical apparatus that gives the status quo the aura of logical inevitability. The numbers don't lie.
Particularly apposite today given Y Combinator's revelation that they use an AI bot to help 'sift admission applications', and don't know what criteria it's using: https://twitter.com/aprjoy/status/783032128653107200culture ethics privacy technology surveillance ml machine-learning bias algorithms software control
#
-
So assuming the mission continues well, in 2014 the Rosetta Probe will land on Comet 67P/Churyumov-Gerasimenko, where it will measure the comet's molecular composition. Then it will remain at rest as the comet orbits the sun for hundreds of millions of years. So somewhere in the solar system, where it is safe but hard to reach, a backup sample of human languages is stored, in case we need one.
As jwz says: 'The Rosetta Disc is now safely installed on 67P/Churyumov-Gerasimenko.'
#
Airflow/AMI/ASG nightly-packaging workflow
Some tantalising discussion on twitter of an Airflow + AMI + ASG workflow for ML packaging: 'We build models using Airflow. We deploy new models as AMIs where each AMI is model + scoring code. The AMI is hence a version of code + model at a point in time : #immutable_infrastructure. It's natural for Airflow to build & deploy the model+code with each Airflow DAG Run corresponding to a versioned AMI. if there's a problem, we can simply roll back to the previous AMI & identify the problematic model building Dag run. Since we use ASGs, Airflow can execute a rolling deploy of new AMIs. We could also have it do a validation & ASG rollback of the AMI if validation fails. Airflow is being used for reliable Model build+validation+deployment.'
ml packaging airflow asg ami deployment ops infrastructure rollback
#
Commodore 64C going strong after over 25 years in production
C64C used in Polish auto repair shop to balance driveshafts, working non-stop for over a quarter of a century. I'd like to see a Spectrum do _this_ ;)
-
'Build Negroni over ice, top with sparkling wine, stir briefly. They'll get you messed up quick, but it's a great way to go.' aka. the Double Sbagliato. yum
negroni cocktails recipes campari prosecco sparkling-wine red-vermouth gin
#
Snooping powers saw 13 people wrongly held on child sex charges in the UK
Sorry, Daily Mail article --
Blunders in the use of controversial snooping powers meant 13 people were wrongly arrested last year on suspicion of being paedophiles. Another four individuals had their homes searched by detectives following errors in attempts to access communications data, a watchdog revealed yesterday. Other mistakes also included people unconnected to an investigation being visited by police and delayed welfare checks on vulnerable people including children whose lives were at risk, said the Interception of Communications Commissioner. [....] A large proportion of the errors involved an internet address which was wrongly linked to an individual. Of the 23 serious mistakes, 14 were human errors and the other nine 'technical system errors'.
surveillance ip-addresses privacy uk daily-mail snooping interception errors
#
The best thing to mark National Stalking Awareness Week would be to scrap the law on stalking
"The Secret Barrister" explains a classic case of empty-gesture lawmaking in the UK:
in 2012, the coalition government, in a fit of virtue signalling, announced a bold plan to offer extra protection to victims of stalking, following a rash of reported cases where obsessive nutjobs had slipped through the net. Hence, via the 2012 Act, section 2A was shoved into the Protection from Harassment Act, creating a shiny new offence of stalking. What is stalking, you ask? Well here's the clever bit. Stalking is…"a course of conduct which amounts to harassment…and [where] the acts or omissions involved are ones associated with stalking". To inject some colour into the dull circularity of the definition, section 2A(3) provides "examples of acts or omissions associated with stalking". In other words, you need to prove that the defendant is guilty of both harassment and stalking, in order to convict them of stalking. Therefore, proving stalking is by definition harder for the prosecution than simply proving harassment. And what do you get if you opt for the harder road? What prize awaits the victorious prosecutor who has slogged her way through the additional evidential burden thrust upon her by section 2A? The answer is….nothing. Or at least, nothing more than if you successfully prosecuted for harassment. The maximum sentence in each case is 6 months' imprisonment. It is the very definition of empty gesture legislating. Section 2A is so very pointlessly pointless that I want urgently to go back in time to the day when then-crime prevention minister Jeremy Browne was hubristically prattling on about what a difference this law is going to make and shove a whoopee pie right up his schnoz. Section 2A does nothing other than create a new offence that is harder to prove than an existing offence that prohibits the same conduct, solely, it seems, to allow for the drawing of an entirely semantic distinction between "harassment" and "stalking".
harrassment stalking law legislation uk police crime prosecution
#
"Better truck design could save hundreds of pedestrian and cyclist lives"
European transport group, Transport and Environment, said that the Loughborough study shows that better design "could save hundreds of pedestrian and cyclists' lives". It added that the study "finds huge differences in the direct vision – what drivers can see with their own eyes – of best and worst-in-class trucks in all categories, and that 'low-entry cabs' like the Mercedes Econic out perform all of today's best performing vehicles." A P-Series truck, from truck maker Scania, was rated at the best of its class with zero blind spots — this could go a long way to explaining why the makers of a Road Safety Authority video using another P-Series truck reportedly had to fake blind spots last year. Mandatory extra mirrors has been EU policy to try to reduce collisions with people cycling and walking but researchers point out that blind spots remain on many trucks and improving direct vision may be a better policy than improving indirect vision using mirrors. [...] The EU currently has a deadline of 2028 for improved vision in trucks but Transport and Environment said: "Given that better vision cabs are already available on the market and in all market segments (best in class, smarter configurations, low entry vehicles) a 2028 deadline is not justifiable."
-
good page on the Universal Scalability Law and how to apply it
usl performance scalability concurrency capacity measurement excel equations metrics
Artist Tricks Tourists With Elaborate Monument To Staten Island Ferry Octopus Attack
'You probably don't know much about the Staten Island Ferry Disaster Memorial Museum, which honors the 400 victims who died when a giant octopus attacked the Cornelius G. Kolff, a Staten Island Ferry boat, on Nov. 22, 1963. That isn't because the event was overshadowed by the assassination of JFK that same day—it's because, as you may have guessed based on the word "tricks" in the headline, there was no such octopus-induced tragedy.'
#
-
great idea -- donate old, obsolete iPhone 4/4s phones to a charity which repurposes them for autistic/non-verbal kids
autism communication health phones recycling charity iphones
Brian Krebs - The Democratization of Censorship
Events of the past week have convinced me that one of the fastest-growing censorship threats on the Internet today comes not from nation-states, but from super-empowered individuals who have been quietly building extremely potent cyber weapons with transnational reach. More than 20 years after Gilmore first coined [his] turn of phrase, his most notable quotable has effectively been inverted — "Censorship can in fact route around the Internet." The Internet can't route around censorship when the censorship is all-pervasive and armed with, for all practical purposes, near-infinite reach and capacity.
brian-krebs censorship ddos internet web politics crime security iot
#
SMC Education Blog — Girls and Their Frenemies
on "relational aggression" among schoolkids
#
"The couple, who had no experience of wine-making but much faith in professorial expertise…"
I love this story -- a wealthy couple buy a vineyard in the Languedoc for its theoretically-optimal microclimate for wine-making. Defying what one's preconceptions would expect (mine included!), the results were fantastic.
In the Languedoc there is a vineyard that teaches us an important lesson about textbook learning and its application to the world. In the early Seventies it was bought by a wealthy couple, who consulted professors Emile Peynaud and Henri Enjalbert, the world's leading academic oenologist and oenological geologist respectively. Between them these men convinced the couple that their new vineyard had a theoretically ideal microclimate for wine-making. When planted with theoretically ideal vines whose fruits would be processed in the optimal way according to the up-to-date science of oenology, this vineyard had the potential to produce wine to match the great first growths of Bordeaux. The received wisdom that great wine was the product of an inscrutable (and untransferable) tradition was quite mistaken, the professors said: it could be done with hard work and a fanatical attention to detail. The couple, who had no experience of wine-making but much faith in professorial expertise, took a deep breath and went ahead. If life were reliably like novels, their experiment would have been a disaster. In fact Aimé and Véronique Guibert have met with a success so unsullied that it would make a stupefying novel (it has already been the subject of a comatogenic work of non-fiction). The first vintage they declared (in 1978) was described by Gault Millau as 'Château Lafite du Languedoc'; others have been praised to the heights by the likes of Hugh Johnson and Robert Parker. The wine is now on the list at the Tour d'Argent and the 1986 vintage retails at the vineyard for £65 a bottle. The sole shadow on the lives of these millionaires is cast by the odd hailstorm. No one to whom I have begun recounting the story believes it will end well. Most people are extremely unwilling to grant that faith in textbook knowledge should ever be crowned with success. We have a very strong narrative bias against such stories. It is a bias we forget once our children fall sick or we have to travel in an aeroplane, but so long as we are in storytelling mode we simply deny that systematic textbook reasoning can make headway against whimsy and serendipity. Apart from anything else, it is deeply unfair that it should.
books science languedoc wine academia microclimates preconceptions
The Problem With Cul-de-Sac Design - CityLab
"A lot of people feel that they want to live in a cul-de-sac, they feel like it's a safer place to be," Marshall says. "The reality is yes, you're safer – if you never leave your cul-de-sac. But if you actually move around town like a normal person, your town as a whole is much more dangerous." This is the opposite of what traffic engineers (and home buyers) have thought for decades. And it's just the beginning of what we're now starting to understand about the relative advantages of going back to the way we designed communities a century ago. Marshall and Garrick took the same group of California cities and also examined all their minutely classified street networks for the amount of driving associated with them. On average, they found, people who live in more sparse, tree-like communities drive about 18 percent more than people who live in dense grids. And that's a conservative calculation.
(via Tony Finch)
#
-
"A modern standard for event-oriented data". Avro schema, events have time and type, schema is external and not part of the Avro stream. 'a modern standard for representing event-oriented data in high-throughput operational systems. It uses existing open standards for schema definition and serialization, but adds semantic meaning and definition to make integration between systems easy, while still being size- and processing-efficient. An Osso event is largely use case agnostic, and can represent a log message, stack trace, metric sample, user action taken, ad display or click, generic HTTP event, or otherwise. Every event has a set of common fields as well as optional key/value attributes that are typically event type-specific.'
osso events schema data interchange formats cep event-processing architecture
#
Highly Available Counters Using Cassandra
solid discussion of building HA counters using CRDTs and similar eventually-consistent data structures
#
J1 2015 "Debugging Java Apps in Containers: No Heavy Welding Gear Required"
Some good slides with tips on running java apps in production in Docker
Algorithmic management as the new Taylorism
'its legacy can be seen in factories, call centres and warehouses today, although new technology has taken the place of Taylor's instruction cards and stopwatches. Many warehouse workers for companies such as Amazon use handheld devices that give them step-by-step instructions on where to walk and what to pick from the shelves when they get there, all the while measuring their "pick rate" in real time. For Jeremias Prassl, a law professor at Oxford university, the algorithmic management techniques of Uber and Deliveroo are Taylorism 2.0. "Algorithms are providing a degree of control and oversight that even the most hardened Taylorists could never have dreamt of," he says.'
algorithms labour work labor taylorism management silicon-valley tech deliveroo uber piece-work
[Cryptography] Bridge hand record generator cracked
'How to cheat at Bridge by breaking the tournament card-dealing random number generator', via Tony Finch
#
A Loud Sound Just Shut Down a Bank's Data Center for 10 Hours | Motherboard
The purpose of the drill was to see how the data center's fire suppression system worked. Data centers typically rely on inert gas to protect the equipment in the event of a fire, as the substance does not chemically damage electronics, and the gas only slightly decreases the temperature within the data center. The gas is stored in cylinders, and is released at high velocity out of nozzles uniformly spread across the data center. According to people familiar with the system, the pressure at ING Bank's data center was higher than expected, and produced a loud sound when rapidly expelled through tiny holes (think about the noise a steam engine releases). The bank monitored the sound and it was very loud, a source familiar with the system told us. "It was as high as their equipment could monitor, over 130dB". Sound means vibration, and this is what damaged the hard drives. The HDD cases started to vibrate, and the vibration was transmitted to the read/write heads, causing them to go off the data tracks. "The inert gas deployment procedure has severely and surprisingly affected several servers and our storage equipment," ING said in a press release.
ing hardware outages hard-drives fire fire-suppression vibration data-centers storage
#
Fuck Your Noguchi Coffee Table
"fuck your bookshelf with all of the spines facing in"
#
-
'All the information you need while traveling including visa requirements, currency, electricity, communication info and more.'
The Internet Thinks I'm Still Pregnant - The New York Times
This is pretty awful -- an accidental, careless and brutal side effect of marketers passing on sensitive info to one another, without respect for their users' privacy: 'I hadn't realized, however, that when I had entered my information into the pregnancy app, the company would then share it with marketing groups targeting new mothers. Although I logged my miscarriage into the app and stopped using it, that change in status apparently wasn't passed along. Seven months after my miscarriage, mere weeks before my due date, I came home from work to find a package on my welcome mat. It was a box of baby formula bearing the note: "We may all do it differently, but the joy of parenthood is something we all share."'
privacy pregnancy miscarriage data-protection apps babies parenthood
#
Peco Beermakers Professional Boiler 32lt (Includes Hop Strainer) - The Homebrew Company
on the list
Tekkonkinkreet Art Book Shinji Kimura - White Side: Shinji Kimura: 9784870317659: Amazon.com: Books
Beautiful background art from a 2006 anime by Shinji Kimura, as a 10" x 7" full-colour hardback art book.
did Google blacklist their own site?
The leading theory that I've seen going around is that Google is actually blocking all links in any FeedBurner feed, because it's a violation of its own terms of service. Seriously. The link-shortener "goo.gl", run by Google, is blocking all URLs generated by Feedburner, run by Google. pic.twitter.com/IR7wrlv6xj — Great Again Also (@agentdero) September 6, 2016 That's because Google's URL shortener's terms of service bans "URL re-directors" and it appears that the genius engineers at Google have decided that Google-run FeedBurner is nothing more than a URL re-director and killed off everyone's links without notice or explanation. This despite the fact that they're the same damn company and that FeedBurner unilaterally moved everyone's RSS feed to use Goo.gl links in the first place.
urls url-shorteners history goo.gl google feedburner redirectors rss links
#
-
Coda Hale's new gig on how they're using Docker, AWS, etc. I like this: "Use containers. Not too much. Mostly for packaging."
Lessons Learned from Using Regexes At Scale
great post from Loggly on production usage of regular expressions on shared, multitenant architecture, where a /.*/ can really screw things up. "NFA isn't a golden ticket" paragraph included
#
Auto Scaling for EC2 Spot Fleets
'we are enhancing the Spot Fleet model with the addition of Auto Scaling. You can now arrange to scale your fleet up and down based on a Amazon CloudWatch metric. The metric can originate from an AWS service such as EC2, Amazon EC2 Container Service, or Amazon Simple Queue Service (SQS). Alternatively, your application can publish a custom metric and you can use it to drive the automated scaling.'
How a Japanese cucumber farmer is using deep learning and TensorFlow
Unfortunately the usual ML problem arises at the end:
One of the current challenges with deep learning is that you need to have a large number of training datasets. To train the model, Makoto spent about three months taking 7,000 pictures of cucumbers sorted by his mother, but it's probably not enough. "When I did a validation with the test images, the recognition accuracy exceeded 95%. But if you apply the system with real use cases, the accuracy drops down to about 70%. I suspect the neural network model has the issue of "overfitting" (the phenomenon in neural network where the model is trained to fit only to the small training dataset) because of the insufficient number of training images."
In other words, as with ML since we were using it in SpamAssassin, maintaining the training corpus becomes a really big problem. :(google machine-learning tensorflow cucumbers deep-learning ml
Northland man denies burning down house but insurer refuses to pay out
This is a mad story. The insurance company is accusing a guy in NZ of using remote-login software from 400km away to trigger a "print" command to a complicated Heath Robinson setup in order to light a fire to burn down his house
#
Google Intrusion Detection Problems
'We have lost access to multiple critical data stores because Google has an automated threat detection system that is incapable of handling false positives.'
google security cloud false-positives intrusion-detection automation fail
#
Engineering Intelligence Through Data Visualization at Uber
bloody hell, Uber have a 15-person dataviz team. More money than sense! The resulting output is pretty though
#
How the NSA snooped on encrypted Internet traffic for a decade | Ars Technica
In a revelation that shows how the National Security Agency was able to systematically spy on many Cisco Systems customers for the better part of a decade, researchers have uncovered an attack that remotely extracts decryption keys from the company's now-decommissioned line of PIX firewalls. The discovery is significant because the attack code, dubbed BenignCertain, worked on PIX versions Cisco released in 2002 and supported through 2009. Even after Cisco stopped providing PIX bug fixes in July 2009, the company continued offering limited service and support for the product for an additional four years. Unless PIX customers took special precautions, virtually all of them were vulnerable to attacks that surreptitiously eavesdropped on their VPN traffic.
#
NPR Website To Get Rid Of Comments
Sadly, this makes sense and I'd have to agree.
Mike Durio, of Phoenix, seemed to sum it up in an email to my office back in April. "Have you considered doing away with the comments sections, or tighter moderation?" he wrote. "The comments have devolved into the Punch-and-Judy-Fest of moronic, un-illuminating observations and petty insults I've seen on other pretty much every other Internet site that allows comments." He added, "This is not in keeping with NPR's take-a-step-back, take-a-deep-breath reporting," and noted, "Now, thread hijacking and personal insults are becoming the stock in trade. Frequent posters use the forums to duke it out with one another." A user named Mary, from Raleigh, N.C., wrote to implore: "Remove the comments section from your articles. The rude, hateful, racist, judgmental comments far outweigh those who may want to engage in some intelligent sideline conversation about the actual subject of the article. I am appalled at the amount of 'free hate' that is found on a website that represents honest and unbiased reporting such as NPR. What are you really gaining from all of these rabid comments other than proof that a sad slice of humanity that preys on the weak while spreading their hate?"
Meeting the Free Speech Crusaders Who Want to End Political Correctness | VICE | United Kingdom
The 'Young British Heritage Society', aka gam*rgate as a college society
#
The Mattress Industry is One Big Scam
yes, yes it is
Unchecked exceptions for IO considered harmful - Google Groups
Insightful thread from the mechanical sympathy group, regarding the checked-vs-unchecked style question:
Peter Lawrey: Our view is that Checked Exception makes more sense for library writers as they can explicitly pass off errors to the caller. As a caller, especially if you are new to a product, you don't understand the exceptions or what you can do about them. They add confusion. For this reason we use checked exceptions internally in the lower layers and try to avoid passing them in our higher level interfaces. Note: A high percentage of our fall backs are handling iOExceptons and recovering from them. [....] My experience is that the more complex and layered your libraries the more essential checked exceptions become. I see them as essential for scalability of your software.
exceptions java style coding checked-exceptions ioexceptions io error-handling
#
TV detector vans may have been a con all along
This is shaking my world view -- although I find it more plausible that (as responses to https://www.theguardian.com/notesandqueries/query/0,5753,-22440,00.html claim) they _did_ work until about 10-20 years ago, by detecting RF emissions from the local oscillator inside the TV. Ross Anderson, at https://www.cl.cam.ac.uk/~rja14/Papers/SE-15.pdf , notes:
During [..] World War II, radio engineering saw advances in radar, passive direction finding, and low-probability-of-intercept techniques, which I'll discuss in the next chapter. By the 1960s, the stray RF leaking from the local oscillator signals in domestic television sets was being targeted by direction-finding equipment in "TV detector vans," in Britain, where TV owners must pay an annual license fee that is supposed to support public broadcast services. Its use has since expanded to satellite and cable TV operators, who use detector vans to find pirate decoders. Some people in the computer security community were also aware that information could leak from cross-coupling and stray RF (see, for example, [259, 791]).
rf radio tv bbc tv-licenses tv-license-detector-vans security emissions tempest
"I Want to Know What Code Is Running Inside My Body" — Backchannel
Sandler wants to be able to explore the code running her device for programming flaws and vulnerability to hacking, but she can't. "Because I don't have access to the source code, I have no power to do anything about it," she says. In her eyes, it's a particularly obvious example of a problem that now cuts across much of modern life: proprietary software has become crucial to daily survival, and yet is often locked away from public exploration and discussion by copyright.
copyright safety health pacemakers law proprietary-software life medicine implants
#
-
'Researchers learn about wire-fraud scam after Nigerian scammers infect themselves with their own malware.'
The researchers observed Wire-Wire scores of $5,000 to $250,000 with the average between $30,000-$50,000 from small- and medium-sized businesses. The scammers themselves were "well-respected and admired" in their communities.
I've heard about this scam -- it's nasty, and worst of all, banks won't reimburse the losses. Showing bottle: one man's vision crafted a revolution
A eulogy for Oliver Hughes, founder of the Porterhouse and Dingle Distillery, and arguably the progenitor of Ireland's craft beer scene. I had the pleasure of sharing a table with him at a beer tasting in Sweeney's off license a while back, and it was both educational and a good fun night. RIP
oliver-hughes porterhouse beer ireland dublin dingle-distillery rip deaths
#
-
'FakeTime is simulated time."
When testing RealTime software a simulator is often employed, which injects events into the program which do not occur in RealTime. If you are writing software that controls or monitors some process that exists in the real world, it takes a long time to test it. But if you simulate it, there is no reason in the simulated software (if it is disconnected from the real world completely) not to make the apparent system time inside your software appear to move at a much faster rate. For example, I have written simulators that can verify the operational steps taken by industrial controllers over a 12 hour FakeTime period, which executes in 60 seconds. This allows me to run '12 hours' of fake time through my test cases and test scenarios, without waiting 12 hours for the testing to complete. Of course, after a successful fakeTime test, an industrial RealTime system still needs to be tested in non-simulated fashion.
-
'Event driven Diagnostic and Remediation Platform' -- aka 'runbooks as code'
runbooks winston netflix remediation outages mttr ops devops
#
International Olympic Committee bans GIFs
hahaha. gtfo, IOC
Ratas - A hierarchical timer wheel
excellent explanation and benchmarks of a timer wheel implementation
timer-wheels timing-wheels algorithms c linux timers data-structures
-
ECS, Docker, ELB, SQS, SNS, RDS, VPC, and spot instances. Pretty canonical setup these days...
The mytaxi app is also now able to predict daily and weekly spikes. In addition, it has gained the elasticity required to meet demand during special events. Herzberg describes a typical situation on New Year's Eve: "Shortly before midnight everyone needs a taxi to get to parties, and after midnight people want to go home. In past years we couldn't keep up with the demand this generated, which was around three and a half times as high as normal. In November 2015 we moved our Docker container architecture to Amazon ECS, and for the first time ever in December we were able to celebrate a new year in which our system could handle the huge number of requests without any crashes or interruptions—an accomplishment that we were extremely proud of. We had faced the biggest night on the calendar without any downtime."
mytaxi aws ecs docker elb sqs sns rds vpc spot-instances ops architecture
#
Exit Scam Survival Guide : Buttcoin
Bitcoin lols:
Honesty is most important. Be sure to carefully explain that (excluding the mountain of evidence to the contrary) there was no way to foresee the [Bitcoin] exchange hacking. Practice phrases like, "this operation was the most trustworthy exchange running out of a vacant building in Singapore" and "no we can't just call the exchange, they don't have a phone number". If your significant other criticizes your decision to buy cryptocurrencies, be sure to fall back on technical merits of cryptocurrencies. Mention, "it's backed by math" and "[insert cryptocurrency here] didn't fail, people failed".
bitcoin buttcoin lol funny cryptocurrency security exchanges
-
awesome resource.
This WIKI collects information about prepaid (or PAYG) mobile phone plans from all over the world. Not just any plans though, they must include good data rates, perfect for smartphone travellers, as well as tablet or mobile modem users.
-
'aw yiss comic generator'. AW YISS
#
Photographer Files $1 Billion Suit Against Getty for Licensing Her Public Domain Images
Massive, massive copyright fail by Alamy and Getty Images.
Since each violation of copyright in this case allows the plaintiff to seek damages up to $25,000, the statutory damages for Getty's 18,755 violations amount to $468,875,000. But because the company was found to have violated the same copyright law within the past three years — in 2013, Daniel Morel was awarded $1.2 million in a suit against Getty, after the agency pulled his photos from Twitter and distributed them without permission to several major publications — Highsmith can elect to seek three times that amount: hence the $1 billion suit. "The economic damage that Ms. Highsmith has suffered includes, without limitation, any and all revenue received by the Defendants based on purported licenses sold for the Highsmith Photos. These funds represent money that Ms. Highsmith could have received had she attempted to monetize her photos through the Defendants," the complaint states. "The injury to Ms. Highsmith's reputation has been … severe," it continues. "There is at least one example of a recipient of a threatening letter for use of a Highsmith Photo researching the issue and determining that Ms. Highsmith had made her photos freely available and free to use through the Library website. … Therefore, anyone who sees the Highsmith Photos and knows or learns of her gift to the Library could easily believe her to be a hypocrite."
getty alamy images copyright licensing relicensing public-domain carol-highsmith
#
Why Uber Engineering Switched from Postgres to MySQL
Uber bringing the smackdown for the HN postgres fanclub, with some juicy technical details of issues that caused them pain. FWIW, I was bitten by crappy postgres behaviour in the past (specifically around vacuuming and pgbouncer), so I've long been a MySQL fan ;)
database mysql postgres postgresql uber architecture storage sql
#
Noirmoutier Indigo Campsite, France
As recommended by J & F: 'Most of the campsites we've stayed in have had great facilities for kids - pools, activities, entertainment etc - but the problem with that is you spend your day being dragged from one to the other. There's none of that at Camping Indigo in Noirmoutier apart from a playground, some kayaks and some music in the bar at night but it is on the beach so the kids either run wild around the campsite or play on the beach - it was the best and most relaxing holiday we ever had and we definitely met the coolest people there. There's a really nice town in the centre of the island and great beaches all around it so hire bikes and roam free.' Bookmarking for next year's holiday planning!
holidays fun france camping noirmoutier chaize-wood loire nantes recommendations
#
-
his Monitorama 2016 talk, talking about the "deep health checks" concept (which I implemented at Swrve earlier this year ;)
monitorama health deep-health-checks healthz testing availability reliability
-
I never knew we had a native take on the sauna, the "teach alluis":
Sweathouses were used for the treatment for a wide range of ailments up to the late 19th and early 20th centuries, primarily rheumatism but also including sciatica, lameness, sore eyes, gout, skin disorders, psychiatric disorders, impotence and infertility. Surviving records indicate that treatment was often a group activity for 4-8 persons. The sweathouse was heated by filling the interior with fuel (turf, heather, wood etc. as available), and firing the structure for a period of up to two days to heat the stone structure, the hot ashes were then raked out and the interior floor lined with bracken, grass or straw. The bathers entered and blocked the entrance with turves, clothes or some other means. The sweating period could last a number of hours while the structure retained heat. Some authors note that water was thrown on hot stones to create steam. Afterwards, the "patients" would either take a cold plunge in the nearby water source, or go home and rest for a few hours, or simply return to their normal daily activities.
(via Aileen)
#
-
excellent recipe for this classic cocktail
-
meditations on this classic cocktail (with solid recipes)
#
-
Course notes from Gerald Jay Sussman's "Adventures in Advanced Symbolic Programming" class at MIT. Hard to argue with this:
The syntax of the regular-expression language is awful. There are various incompatable forms of the language and the quotation conventions are baroquen [sic]. Nevertheless, there is a great deal of useful software, for example grep, that uses regular expressions to specify the desired behavior. Although regular-expression systems are derived from a perfectly good mathematical formalism, the particular choices made by implementers to expand the formalism into useful software systems are often disastrous: the quotation conventions adopted are highly irregular; the egregious misuse of parentheses, both for grouping and for backward reference, is a miracle to behold. In addition, attempts to increase the expressive power and address shortcomings of earlier designs have led to a proliferation of incompatible derivative languages.
(via Rob Pike's twitter: https://twitter.com/rob_pike/status/755856685923639296)regex regexps regular-expressions functional combinators gjs rob-pike coding languages
A Cute Internet Star Flirts. All He Wants Is Your Password. - The New York Times
whoa.
Mr. Johnson's fans are not naïve. Handing over their passwords to some strange, cute boy actually constitutes a minor act of youthful rebellion. The whole encounter delivers a heady mix of intimacy and transgression — the closest digital simulation yet to a teenage crush.
(via Adam Shostack)via:adam-shostack passwords authentication security teens rebellion
Just As We Warned: A Chinese Tech Giant Goes On The Patent Attack -- In East Texas | Techdirt
Techdirt has been warning for years that the West's repeated demands for China to "respect" patents could backfire badly. [...] And guess what? That is exactly what has just happened, as The Wall Street Journal reports: 'Huawei Technologies Co. said it has filed a lawsuit against T-Mobile US Inc., alleging the U.S. telecommunications carrier violated the Chinese company's patents related to wireless networks. In its complaint filed this week in the U.S. District Court for the Eastern District of Texas, Huawei said T-Mobile is using its patented technology without signing a licensing agreement.'
At least this is the most likely scenario to result in patent reform, finally.A New Wrinkle in the Gig Economy: Workers Get Most of the Money - The New York Times
So using money from the sale of iStock to Getty, she and Mr. Livingstone set out to create Stocksy, paying photographers 50 to 75 percent of sales. That is well above the going rate of 15 to 45 percent that is typical in the stock photography field. The company also distributes 90 percent of its profit at the end of each year among its photographers. Stocksy is part of a new wave of start-ups that are borrowing the tools of Silicon Valley to create a more genuine "sharing" economy that rewards the individuals generating the value.
#
-
(a) 83.5% uptime over 24 hours. GOOD JOB (b) excellent marketing by Datadog!
#
-
eye-poppingly bizarre half-assed safety features of the 1950s -- a megaton nuclear weapon rendered safe from accidental criticality accidents only by a plastic bag full of ball bearings
nuclear-weapons nukes safety 1950s uk funny bizarre violet-club ball-bearings via:cstross
Frankly Useless Crank "Knowledge," Only For Fools
A wonderfully-sweary post on the etymology of swear words, and how they're not derived from acronyms, really.
shit? Also from an old Germanic root, descended equally to modern German Scheiss (which sounds closer to Scots shite). It shows up in Old English, fully inflected: "Wiþ þon þe men mete untela melte & gecirre on yfele wætan & scittan" (that scittan is an infinitive form of 'shit' and was said like "shit-tan"). I can assure you that an acronym Ship High In Transit – supposedly meaning that manure was to be loaded in the upper parts of ships – was not possible in the language in the Old English period, not just because transit was not borrowed from Latin until half a millennium later, or because they didn't use acronyms like that then, but because what the fuck are you even thinking. They didn't need to ship manure. Animals produce it on the spot everywhere. Holy shit, fucking seriously.
#
QA Instability Implies Production Instability
Invariably, when I see a lot of developer effort in production support I also find an unreliable QA environment. It is both unreliable in that it is frequently not available for testing, and unreliable in the sense that the system's behavior in QA is not a good predictor of its behavior in production.
#
-
Doorman is a solution for Global Distributed Client Side Rate Limiting. Clients that talk to a shared resource (such as a database, a gRPC service, a RESTful API, or whatever) can use Doorman to voluntarily limit their use (usually in requests per second) of the resource. Doorman is written in Go and uses gRPC as its communication protocol. For some high-availability features it needs a distributed lock manager. We currently support etcd, but it should be relatively simple to make it use Zookeeper instead.
From google -- very interesting to see they're releasing this as open source, and it doesn't rely on G-internal servicesdistributed distcomp locking youtube golang doorman rate-limiting rate-limits limits grpc etcd
-
'based my observations while I was a Site Reliability Engineer at Google', courtesy of Rob Ewaschuk <rob@infinitepigeons.org>. Seem pretty reasonable
monitoring sysadmin alerting alerts nagios pager ops sre rob-ewaschuk
-
'Best Plex Media Server' -- this looks pretty superb for EUR240 or thereabouts
media-servers plex video home tv toget nvidia shield android
#
-
'a small library to manage encrypted secrets using asymmetric encryption.'
The main benefits provided by ejson are: Secrets can be safely stored in a git repo. Changes to secrets are auditable on a line-by-line basis with git blame. Anyone with git commit access has access to write new secrets. Decryption access can easily be locked down to production servers only. Secrets change synchronously with application source (as opposed to secrets provisioned by Configuration Management). Simple, well-tested, easily-auditable source.
crypto security credentials encryption ejson json configuration config
#
The mysterious syndrome impairing astronauts' sight - The Washington Post
Visual impairment intracranial pressure syndrome (VIIP) is named for the leading theory to explain it. On Earth, gravity pulls bodily fluids down toward the feet. That doesn't happen in space, and it is thought that extra fluid in the skull increases pressure on the brain and the back of the eye.
Designing the Perfect Anti-Object
This pale, amorphous lump of sculpted concrete is designed to resist almost everything in a city that it might come into contact with. Named for the London authority that commissioned it, the Camden Bench has a special coating which makes it impervious to graffiti and vandalism. The squat, featureless surface gives drug dealers nowhere to hide their secret caches. The angled sides repel skateboarders and flyposters, litter and rain. The cambered top throws off rough sleepers. In fact, it is specially crafted to make sure that it is not used as anything except a bench. This makes it a strange artifact, defined far more by what it is not than what it is. The Camden Bench is a concerted effort to create a non-object.
non-objects objects city camden benches vandalism skating london
#
The Apollo 11 AGC source code was uploaded to Github, and someone opened an issue
For the famous Apollo 13 near-fatal failure scenario:
'A customer has had a fairly serious problem with stirring the cryogenic tanks with a circuit fault present. To reproduce: Build CSM; Perform mission up to translunar coast; During translunar coast, attempt to stir cryo tanks If a wiring fault exists, the issue may be replicated. Be aware that this may be hazardous to the tester attempting it.' Sample response: 'Does it happens only with translunar coast (sol-3-a), or any moon coasting? It may be a problem with the moon. Just trying to narrow down the issue.'
lol funny apollo apollo-11 apollo-13 agc history space github
Law to allow snooping on social media defies European court ruling
Karlin on fire:
But there's lots in this legislation that should scare the public far more. For example, the proposal that the legislation should allow the retention of "superfluous data" gathered in the course of an investigation, which is a direct contravention of the ECJ's demand that surveillance must be targeted and data held must be specifically relevant, not a trawl to be stored for later perusal "just in case". Or the claim that interception and retention of data, and access to it, will only be in cases of the most serious crime or terrorism threats. Oh, please. This was, and remains, the supposed basis for our existing, ECJ-invalidated legislation. Yet, as last year's Gsoc investigation into Garda leaks revealed, it turns out a number of interconnected pieces of national legislation allow at least 10 different agencies access to retained data, including Gsoc, the Competition Authority, local authorities and the Irish Medicines Board.
surveillance ireland whatsapp viber snowden snooping karlin-lillington facebook internet data-retention
#
Raintank investing in Graphite
paying Jason Dixon to work on it, improving the backend, possibly replacing the creaky Whisper format. great news!
graphite metrics monitoring ops open-source grafana raintank
conventional-changelog-atom 502 Bad Gateway · Issue #13284 · npm/npm
npm down for most of the (EU) day. What a shitshow
Camille Fournier's excellent rant on microservices
I haven't even gotten into the fact that your microservices are an inter-dependent environment, as much as you may wish otherwise, and one service acting up can cause operational problems for the whole team. Maybe if you have Netflix-scale operational hardening that's not a problem. Do you? Really? Is that the best place to spend your focus and money right now, all so teams can throw shit against the wall to see if it sticks? Don't sell people fantasies. This is not the reality for a mid-sized tech team working in microservices. There are enough valuable components to building out such a system without the fantastical claims of self-organizing teams who build cool hack projects in 2 week sprints that change the business. Microservices don't make organizational problems disappear due to self-organization. They allow for some additional degrees of team and process independence and force very explicit decoupling, in exchange, there is overall system complexity and overall system coordination overhead. I personally think that's enough value, especially when you are coming from a monolith that is failing to scale, but this model is not a panacea.
microservices rants camille-fournier architecture decoupling dependencies
#
-
quotable: "I spend a lot of time on this task. I should write a program automating it!"
-
Quotable: "how long can work on making a routine task more efficient before you're spending more time than you save?"
quotes time automation hacks life imdb productivity efficiency
Why Did Yankee Doodle Call a Feather 'Macaroni'? | Mental Floss
history!
usa history macaroni yankee-doodle language dandies 18th-century
-
John Rauser on this oft-cited dictum of percentile usage in monitoring, and when it's wrong and it's actually possible to reason with averaged percentiles, and when it breaks down.
statistics percentiles quantiles john-rauser histograms averaging mean p99
MRI software bugs could upend years of research - The Register
In their paper at PNAS, they write: "the most common software packages for fMRI analysis (SPM, FSL, AFNI) can result in false-positive rates of up to 70%. These results question the validity of some 40,000 fMRI studies and may have a large impact on the interpretation of neuroimaging results." For example, a bug that's been sitting in a package called 3dClustSim for 15 years, fixed in May 2015, produced bad results (3dClustSim is part of the AFNI suite; the others are SPM and FSL). That's not a gentle nudge that some results might be overstated: it's more like making a bonfire of thousands of scientific papers. Further: "Our results suggest that the principal cause of the invalid cluster inferences is spatial autocorrelation functions that do not follow the assumed Gaussian shape". The researchers used published fMRI results, and along the way they swipe the fMRI community for their "lamentable archiving and data-sharing practices" that prevent most of the discipline's body of work being re-analysed. ®
fmri science mri statistics cluster-inference autocorrelation data papers medicine false-positives fps neuroimaging
-
'a Ruby regular expression editor and tester'. Great for prototyping regexps with a little set of test data, providing a neat permalink for the results

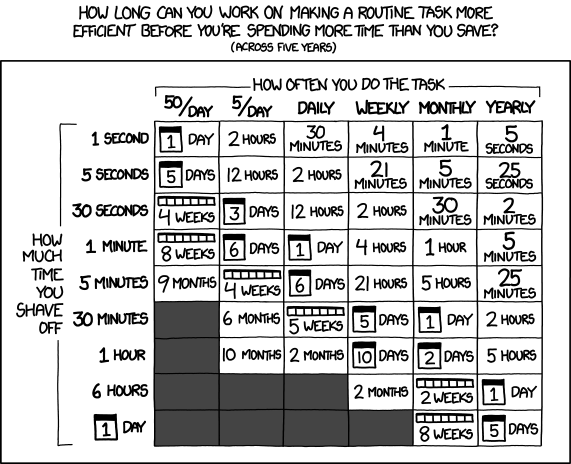
#
Stick Insect Eggs - Live Bug Kits
going to do this with the kids next!
#
-
by avoiding division
coding algorithms performance optimization shuffle shuffling
Self-driving cars: overlooking data privacy is a car crash waiting to happen
Interesting point -- self-driving cars are likely to be awash in telemetry data, "phoned home"
self-driving cars vehicles law data privacy data-privacy surveillance
#
Push notifications delayed, Hearbeat Interval not reliable - Google Product Forums
Good thread on GCM notifications and their interactions with NAT -- they are delivered over a single TCP connection to port 5228 to the google servers, kept alive, and NAT timeouts can hang the conn resulting in delayed notifications. Particularly useful is the *#*#426#*#* dial code, which displays a log screen on Android devices with GCM debugging info.
USE Method: Linux Performance Checklist
Really late in bookmarking this, but has some up-to-date sample commandlines for sar, mpstat and iostat on linux
linux sar iostat mpstat cli ops sysadmin performance tuning use metrics
#
My kids don't have a YouTube channel — but they pretend they do
"Dad is making a right turn now," my 5-year-old son Jack will say as he newscasts the ride to school to a fictional audience. "Don't forget to subscribe," his sister Ella, 6, will often interject -- again, to no one in particular. When I was their age, I'd pretend to be a soldier or a baseball player. Today, kids apparently aspire to be vloggers. It's not enough for them to watch their favorite shows. They want to broadcast their lives, banter with commenters and keep their make-believe view counts high.
#
Cops Use Stingray To Almost Track Down Suspected Fast Food Thief
Law enforcement spokespeople will often point to the handful of homicide or kidnapping investigations successfully closed with the assistance of cell site simulators, but they'll gloss over the hundreds of mundane deployments performed by officers who will use anything that makes their job easier -- even if it's a tool that's Constitutionally dubious. Don't forget, when a cell site simulator is deployed, it gathers cell phone info from everyone in the surrounding area, including those whose chicken wings have been lawfully purchased. And all of this data goes... somewhere and is held onto for as long as the agency feels like it, because most agencies don't seem to have Stingray data retention policies in place until after they've been FOIA'ed/questioned by curious legislators. Regular policework -- which seemed to function just fine without cell tracking devices -- now apparently can't be done without thousands of dollars of military equipment. And it's not just about the chicken wing thieves law enforcement can't locate. It's about the murder suspects who are caught but who walk away when the surveillance device wipes its feet on the Fourth Amendment as it serves up questionable, post-facto search warrants and pen register orders.
stingrays mobile surveillance imsi-catchers data-retention privacy chicken-wings fast-food
A fast alternative to the modulo reduction
(x * N) div 2^32 is an equally fair map reduction, but faster on modern 64-bit CPUs
fairness modulo arithmetic algorithms fair-mapping reduce daniel-lemire
#
There are liars and then there's Boris Johnson and Michael Gove
Post-brexit post-mortem from Nicholas Cohen in the grauniad:
The Vote Leave campaign followed the tactics of the sleazy columnist to the letter. First, it came out with the big, bold solution: leave. Then it dismissed all who raised well-founded worries with "the country is sick of experts". Then, like Johnson the journalist, it lied.
-
The prime minister evidently thought that the whole debate could be cleanly started and finished in a matter of months. His Eton contemporary Boris Johnson – and, really, can you believe that the political story of the last four months has effectively been a catastrophic contest between two people who went to the same exclusive school? – opportunistically embraced the cause of Brexit in much the same spirit. What they had not figured out was that a diffuse, scattershot popular anger had not yet decisively found a powerful enough outlet, but that the staging of a referendum and the cohering of the leave cause would deliver exactly that. Ukip were held back by both the first-past-the-post electoral system, and the polarising qualities of Farage, but the coalition for Brexit effectively neutralised both. And so it came to pass: the cause of leaving the EU, for so long the preserve of cranks and chancers, attracted a share of the popular vote for which any modern political party would give its eye teeth.
#
In Wisconsin, a Backlash Against Using Data to Foretell Defendants' Futures - The New York Times
More trial-by-algorithm horrors:
Company officials say the algorithm's results are backed by research, but they are tight-lipped about its details. They do acknowledge that men and women receive different assessments, as do juveniles, but the factors considered and the weight given to each are kept secret. "The key to our product is the algorithms, and they're proprietary," said Jeffrey Harmon, Northpointe's general manager. "We've created them, and we don't release them because it's certainly a core piece of our business. It's not about looking at the algorithms. It's about looking at the outcomes." That secrecy is at the heart of Mr. Loomis's lawsuit. His lawyer, Michael D. Rosenberg, who declined to be interviewed because of the pending appeal, argued that Mr. Loomis should be able to review the algorithm and make arguments about its validity as part of his defense. He also challenges the use of different scales for each sex. The Compas system, Mr. Rosenberg wrote in his brief, "is full of holes and violates the requirement that a sentence be individualized."
ethics compas sentencing wisconsin northpointe law trial-by-algorithm algorithms
#
Holloways: Roads Tunneled into the Earth by Time
Appearing like trenches dragged into the earth, sunken lanes, also called hollow-ways or holloways, are centuries-old thoroughfares worn down by the traffic of time. They're one of the few examples of human-made infrastructure still serving its original purpose, although many who walk through holloways don't realize they're retracing ancient steps.
cool hiking geography roads paths holloways psychogeography lanes
Terrorism and internet blocking – is this the most ridiculous amendment ever? - EDRi
So, there you have it: Blocking is necessary, except it is not. Safeguards need to be implemented, except they don't need to be. This approach is legal, except it isn't. The text is based on the Child Exploitation Directive, except it isn't. Is this really how we are going to create credible legislation on terrorism?
E-Voting in Estonia needs to be discontinued
After studying other e-voting systems around the world, the team was particularly alarmed by the Estonian I-voting system. It has serious design weaknesses that are exacerbated by weak operational management. It has been built on assumptions which are outdated and do not reflect the contemporary reality of state-level attacks and sophisticated cybercrime. These problems stem from fundamental architectural problems that cannot be resolved with quick fixes or interim steps. While we believe e-government has many promising uses, the Estonian I-voting system carries grave risks — elections could be stolen, disrupted, or cast into disrepute. In light of these problems, our urgent recommendation is that to maintain the integrity of the Estonian electoral process, use of the Estonian I-voting system should be immediately discontinued.
internet technology e-voting voting security via:mattblaze estonia i-voting russia cybercrime
#
Squeezing blood from a stone: small-memory JVM techniques for microservice sidecars
Reducing service memory usage from 500MB to 105MB:
We found two specific techniques to be the most beneficial: turning off one of the two JIT compilers enabled by default (the "C2" compiler), and using a 32-bit, rather than a 64-bit, JVM.
#
The Irish Internet in the 1980s
from Dr Mark Humphrys in DCU:
A collection of bits and pieces of Internet history. Focusing somewhat (but not exclusively) on: (a) the 1980s, when I first started using the Internet, and: (b) Ireland.
mark-humphrys dcu history tcd bitnet ireland internet web www 1980s
-
I need to get in touch about the early days of the Irish web!
an online home for stories from Ireland – stories about the country's long and convoluted relationship with information technology. It aims to gather information on the most significant aspects of this relationship, to compile archives on the selected themes, and to store the assembled records for the benefit of future generations.
The History of the Irish Internet
This site is a companion effort to the techarchives website, except it is less well-researched, and is primarily a personal view of the development of the Internet in Ireland by your humble author, Niall Murphy.
What's Actually Wrong with Yahoo's Purchase of Summly
An old post about Y!'s acquisition of Summly, an iPhone app which uses NLP to summarise news stories. This is an excellent point about modern tech startups:
[Summly] licensed the core engine from another company. They are the quintessential bolt-on engineers, taking a Japanese bike engine, slapping together a badly constructed frame aligned solely by eyeballs, and laying down a marketing blitz. That's why the story sells. "You, too, can do it." But do you want to? [...] it's critical to keep tabs on the ratio known as "glue versus thought." Sure, both imply progress and both are necessary. But the former is eminently mundane, replaceable, and outsource-able. The latter is typically what gives a company its edge, what is generally regarded as a competitive advantage. So, what is Yahoo signaling to the world? "We value glue more than thought."
glue thought glue-vs-thought summly yahoo acquisitions licensing tech startups outsourcing open-source
#
What the Irish Ate Before Potatoes - Bon Appétit
on the history of Irish cuisine -- mostly milk and butter, and notably "bog butter":
And the Irish didn't like their butter just one way: from the 12th century on, there are records of butter flavored with onion and garlic, and local traditions of burying butter in bogs. Originally, it's thought that bog butter began as a good storage system, but after a time, buried bog butter came to be valued for its uniquely boggy flavor.
bog-butter bogs ireland food eating milk curds whey banbidh dairy
The tyranny of the algorithm yet again...
Paypal will no longer handle payments if the user's address includes the word "Isis":
That these place names exist won't be a surprise to anyone familiar with English limnology - the study of rivers and inland waters. As Wikipedia helpfully tells us, "The Isis is the name given to the part of the River Thames above Iffley Lock which flows through the university city of Oxford". In at least one local primary school I'm familiar with, the classes are called Windrush, Cherwell, Isis and Thames. [...] Now PayPal has decided that they are not prepared to facilitate payments for goods to be delivered to an address which includes the word "Isis". An Isis street resident ran into some unexpected difficulties when attempting to purchase a small quantity of haberdashery on the internet with the aid of a PayPal account. The transaction would not process. In puzzlement she eventually got irritated enough to brave the 24/7 customer support telephone tag labyrinth. The short version of the response from the eventual real person she managed to get through to was that PayPal have blacklisted addresses which include the name "Isis". They will not process payments for goods to be delivered to an Isis related address, whatever state of privileged respectability the residents of such properties may have earned or inherited in their lifetimes to this point.
One has to wonder if this also brings the risk of adding the user to a secret list, somewhere. Trial by algorithm.isis algorithms automation fail law-enforcement paypal uk rivers
Can the United Kingdom government legally disregard a vote for Brexit?
Oh thank god, there's a "get out of jail" card before they destroy the global economy to appease the eurosceptics.
On the day after a vote for Brexit, the UK will still be a member state of the EU. All the legislation which gives effect to EU law will still be in place. Nothing as a matter of law changes in any way just because of a vote to Leave. What will make all the legal difference is not a decision to leave by UK voters in a non-binding advisory vote, but the decision of the prime minister on how to react before making any Article 50 notification. And what the prime minister will do politically after a referendum vote for Brexit is, at the moment, as unknown as the result of the result of the referendum itself.
-
comparison-shopping site for Irish car insurance. recommended by some random Broadsheet commenter, worth a try next time this comes up
-
Apple have announced they plan to use it; Google use a DP algorithm called RAPPOR in Chrome usage statistics. In summary: "novel privacy technology that allows inferring statistics about populations while preserving the privacy of individual users".
apple privacy anonymization google rappor algorithms sampling populations statistics differential-privacy
-
The Department of Education has issued a new circular accepting it cannot defund the education of children whose parents do not want their kid's data to be in POD [the privacy-infringing database of all Irish primary-school children]. They'll only accept a written request as the basis of that refusal, however. So, here's one you can use that meets the requirements. Send or give it to your school.
Three starts network-level ad blocking trial
Three, the mobile carrier, has begun warming up for a network-level ad blocking trial. It will become one of the first mobile carriers worldwide—and certainly in the UK—to try blocking ads before they are squirted over the network to the consumer, rather than attempting to hide or block ads locally on the device, which can cost both bandwidth and battery life. The ad blocking trial, which will affect both mobile websites and apps, will take place during a 24-hour period sometime between June 13 and 20. Three says it will contact customers and ask them to sign up for the trial, presumably via the online customer portal. It isn't clear how large the trial will be. Technologically, the network-level ad blocking will be powered by Shine. Due to the nature of the beast—the constant tussle between ad publishers and ad blockers—Shine doesn't like to talk about its tech in much detail. It sounds like Shine uses deep packet inspection and machine learning to find packets that contain ads, and then replaces or removes them in such a way that it doesn't break the layout of the website or app.
Some thoughts on operating containers
R.I.Pienaar talks about the conventions he uses when containerising; looks like a decent approach.
ClickHouse — open-source distributed column-oriented DBMS
'ClickHouse manages extremely large volumes of data in a stable and sustainable manner. It currently powers Yandex.Metrica, world's second largest web analytics platform, with over 13 trillion database records and over 20 billion events a day, generating customized reports on-the-fly, directly from non-aggregated data. This system was successfully implemented at CERN's LHCb experiment to store and process metadata on 10bn events with over 1000 attributes per event registered in 2011.' Yandex-tastic, but still looks really interesting
#
Cross-Region Read Replicas for Amazon Aurora
Creating a read replica in another region also creates an Aurora cluster in the region. This cluster can contain up to 15 more read replicas, with very low replication lag (typically less than 20 ms) within the region (between regions, latency will vary based on the distance between the source and target). You can use this model to duplicate your cluster and read replica setup across regions for disaster recovery. In the event of a regional disruption, you can promote the cross-region replica to be the master. This will allow you to minimize downtime for your cross-region application. This feature applies to unencrypted Aurora clusters.
aws mysql databases storage replication cross-region failover reliability aurora
Advanced Airflow (Lesson 1) : TriggerDagRunOperator
good intro to some Airflow concepts
Finding pearls; fuzzing ClamAV
great how-to for practical scanner fuzz testing
fuzz-testing clamav scanners security vulnerabilities testing
#
Ireland goes Big Brother as police upgrade snooping abilities - The Register
The Garda Síochána has proposed to expand its surveillance on Irish citizens by swelling the amount of data it collects on them through an increase in its CCTV and ANPR set-ups, and will also introduce facial and body-in-a-crowd biometrics technologies. [...] The use of Automated Facial Recognition (AFR) technology is fairly troubled in the UK, with the independent biometrics commissioner warning the government that it was risking inviting a legal challenge back in March. It is no less of an issue in Ireland, where the Data Protection Commissioner (DPC) audited Facebook in 2011 and 2012, and scolded the Zuckerborg over its use of facial recognition technology.
afr facial-recognition minority-report surveillance ireland gardai cctv anpr biometrics privacy
-
"Here," by Richard McGuire. Amazing piece of comic art from 1989
#
Stop it with short PGP key IDs!
What happened today? We still don't really know, but it seems we found a first potentially malicious collision — that is, the first "nonacademic" case. Enrico found two keys sharing the 9F6C6333 short ID, apparently belonging to the same person (as would be the case of Asheesh, mentioned above). After contacting Gustavo, though, he does not know about the second — That is, it can be clearly regarded as an impersonation attempt. Besides, what gave away this attempt are the signatures it has: Both keys are signed by what appears to be the same three keys: B29B232A, F2C850CA and 789038F2. Those three keys are not (yet?) uploaded to the keyservers, though... But we can expect them to appear at any point in the future. We don't know who is behind this, or what his purpose is. We just know this looks very evil. Now, don't panic: Gustavo's key is safe. Same for his certifiers, Marga, Agustín and Maxy. It's just a 32-bit collision. So, in principle, the only parties that could be cheated to trust the attacker are humans, right? Nope. Enrico tested on the PGP pathfinder & key statistics service, a keyserver that finds trust paths between any two arbitrary keys in the strong set. Surprise: The pathfinder works on the short key IDs, even when supplied full fingerprints. So, it turns out I have three faked trust paths into our impostor.
UK at serious risk of over-blocking content online, human rights watchdog warns | Ars Technica UK
The IWF in the spotlight...
The blacklist operated by the IWF effectively amounts to censorship. Not only are the blacklist and notices sent to members of the IWF kept secret, but there is no requirement to notify website owners when their site has been added to the blacklist. Even where statutory rules do exist with respect to notice and take-down procedures (namely, the Terrorism Act 2006 and the Defamation (Operators of Websites) Regulations 2013), the provisions are not so concerned with safeguards for the protection of freedom of expression, as with offering an exemption from liability for ISPs.
#
Collecting my thoughts about Torus
Worryingly-optimistic communications about CoreOS' recently-announced distributed storage system. I had similar thoughts, but Jeff Darcy is actually an expert on this stuff so he's way more worth listening to on the topic ;)
German Privacy Regulators Fined Adobe, Others Over U.S. Data Transfers
Adobe was fined 8,000 euros, Punica 9,000 euros and Unilever 11,000 euros. The regulator said they had put in place alternative legal mechanisms for transferring data to the United States following the fine. "The fact that the companies have eventually implemented a legal basis for the transfer had to be taken into account in a favorable way for the calculation of the fines," said Johannes Caspar, the Hamburg Commissioner for Data Protection. "For future infringements, stricter measures have to be applied."
[dns-operations] Sad news today: systemd-resolved to be deployed in Ubuntu 16.10
systemd needs to stop breaking shit
The Mitsubishi Outlander vulnerability allows trivial remote car alarm unlocking.
Nearly-open wifi (easily-cracked weak WPA PSK), and a 6-byte string to disable the car alarm, discovered via replay attack. Massive fail
internetofshit mitsubishi fail outlander wpa alarms security replay-attack
#
FullPageOS Automatically Boots Your Raspberry Pi Into a Full Page Web Kiosk Mode
set up to boot into a full-screen Chromium window on boot. This means if you're using your Pi to power an information display, you won't need to go through the process of disabling screen savers, editing display size, and forcing full-screen mode on your own. All you need to do is install FullPageOS on an SD card, then edit a TXT file to include your Wi-Fi network info and the URL you want it to load up.
kiosks raspberry-pi fullpageos chrome chromium web appliances hacks
_Could a Neuroscientist Understand a Microprocessor?_
'There is a popular belief in neuroscience that we are primarily data limited, that producing large, multimodal, and complex datasets will, enabled by data analysis algorithms, lead to fundamental insights into the way the brain processes information. Microprocessors are among those artificial information processing systems that are both complex and that we understand at all levels, from the overall logical flow, via logical gates, to the dynamics of transistors. Here we take a simulated classical microprocessor as a model organism, and use our ability to perform arbitrary experiments on it to see if popular data analysis methods from neuroscience can elucidate the way it processes information. We show that the approaches reveal interesting structure in the data but do not meaningfully describe the hierarchy of information processing in the processor. This suggests that current approaches in neuroscience may fall short of producing meaningful models of the brain.' via Bryan O'Sullivan.
via:bos neuroscience microprocessors 6502 computers hardware wetware brain biology neural-systems
#
MPs' private emails are routinely accessed by GCHQ
65% of parliamentary emails are routed via Dublin or the Netherlands, so liable to access via Tempora; NSA's Prism program gives access to all Microsoft Office 365 docs; and MessageLabs, the anti-spam scanning system in use, has a GCHQ backdoor program called Haruspex, allegedly.
snowden privacy mps uk politics gchq nsa haruspex messagelabs symantec microsoft parliament
#
-
'centrally-planned object and thread pools' for java. 'In the default JVM thread pools, once a thread is created it will only be retired when it hasn't performed a task in the last minute. In practice, this means that there are as many threads as the peak historical number of concurrent tasks handled by the pool, forever. These thread pools are also poorly instrumented, making it difficult to tune their latency or throughput. Dirigiste provides a fast, richly instrumented version of a java.util.concurrent.ExecutorService, and provides a means to feed that instrumentation into a control mechanism that can grow or shrink the pool as needed. Default implementations that optimize the pool size for thread utilization are provided. It also provides an object pool mechanism that uses a similar feedback mechanism to resize itself, and is significantly simpler than the Apache Commons object pool implementation.' Great metric support, too.
async jvm dirigiste java threadpools concurrency utilization capacity executors object-pools object-pooling latency
#
-
new Jenkins UX. looks great
Here comes the summer: how Daylight Saving Time came to Ireland
good history on the crapfest that is DST
'Virtual nose' may reduce simulator sickness
Anecdotal evidence has suggested simulator sickness is less intense when games contain fixed visual reference objects - such as a racecar's dashboard or an airplane's cockpit - located within the user's field of view. "But you can't have a cockpit in every VR simulation," Whittinghill said. His research team was studying the problem when undergraduate student Bradley Ziegler suggested inserting the image of a virtual human nose in the center of the video display. "It was a stroke of genius," said Whittinghill, who teaches video game design. "You are constantly seeing your own nose. You tune it out, but it's still there, perhaps giving you a frame of reference to help ground you." The researchers have discovered that the virtual nose, or "nasum virtualis," reduces simulator sickness when inserted into popular games.
virtual-nose nose vr simulator-sickness nausea vr-sickness games
-
Interesting new collections lib for Java 6+; generates Map-like and Set-like collections at runtime based on the contract annotations you desire. Fat (20MB) library-based implementation also available
Symantec Issues Intermediate CA Certificate for Blue Coat Public Services
ugh, so dodgy
#
Green/Blue Deployments with AWS Lambda and CloudFormation - done right
Basically, use a Lambda to put all instances from an ASG into the ELB, then remove the old ASG
Six Years of Hacker News Comments about Twilio
love it.
-
'Tired of copy/pasting Dockerfiles around? Not sure about best practices for Dockerfiles or Docker entry points? This tool lets you Dockerize your applications using best practices to define your Dockerfile and Docker entry point files.' The best practices in question are defined here: https://github.com/docker-library/official-images#review-guidelines
docker dockerfile images build best-practices alpine containers
-
backward compatible replacement for Dockerfile. Yes, you can take any Dockerfile, rename it to Rockerfile and use rocker build instead of docker build. ... Rocker aims to solve the following use cases, which are painful with plain Docker: Mount reusable volumes on build stage, so dependency management tools may use cache between builds. Share ssh keys with build (for pulling private repos, etc.), while not leaving them in the resulting image. Build and run application in different images, be able to easily pass an artifact from one image to another, ideally have this logic in a single Dockerfile. Tag/Push images right from Dockerfiles. Pass variables from shell build command so they can be substituted to a Dockerfile. And more. These are the most critical issues that were blocking our adoption of Docker at Grammarly. The most challenging part is caching. While implementing those features seems to be not a big deal, it's not trivial to do that just by utilising Docker's image cache (the one that docker build does). Actually, it is the main reason why those features are still not in Docker. With Rocker we achieve this by introducing a set of trade-offs. Search this page for "trade-off" to find out more details.
How big an issue is the nausea problem for Virtual Reality products? - Quora
Sadly (because I want a "holodeck" as much as the next red-blooded geek) - I don't think it's possible to make a VR system that both delivers the experience that everyone wants - and doesn't make a sizeable proportion of the population so sick that they'll never want to do it again. For the people who can stomach the display - my major concern is that the US Navy studies show that there is some disorientation that might persist long after finishing your game…so driving a car while "under the influence" of post-VR disorientation is probably as dangerous as drunk-driving. If these devices are in pretty much every home - then there are huge problems in store for the industry in terms of product liability. There have been plenty of warnings from the flight simulation industry - there are no excuses for not reading the Wikipedia article on the subject. If people are driving "under the influence" and the VR companies didn't warn them about that - then they're in deep trouble. IMHO, these consumer-grade VR devices should be carefully studied and if they do cause possible driving impairment, they should be banned until such time as the problems can be fixed…which may very well be "never". Sorry to be the bearer of bad news.
(via Tony Finch)holodeck vr oculus-rift hmds nausea head-mounted-displays biology brain flight-simulation
Why do Selenium-style record/replay tests of web applications break?
good data! Mostly because of element locations it seems....
LinkedIn called me a white supremacist
Wow. Massive, massive algorithm fail.
n the morning of May 12, LinkedIn, the networking site devoted to making professionals "more productive and successful," emailed scores of my contacts and told them I'm a professional racist. It was one of those updates that LinkedIn regularly sends its users, algorithmically assembled missives about their connections' appearances in the media. This one had the innocent-sounding subject, "News About William Johnson," but once my connections clicked in, they saw a small photo of my grinning face, right above the headline "Trump put white nationalist on list of delegates." [.....] It turns out that when LinkedIn sends these update emails, people actually read them. So I was getting upset. Not only am I not a Nazi, I'm a Jewish socialist with family members who were imprisoned in concentration camps during World War II. Why was LinkedIn trolling me?
[RFE] add a way to run in a new systemd scope automatically · Issue #428 · tmux/tmux
omgwtfbbq. 1: User reports that their gnome session leaks processes; 2: systemd modifies default session behaviour to kill all processes, including screen/tmux; 3: _everyone_ complains because they break 30 years of UNIX process semantics, then 4: they request that tmux/screen hack their shit to workaround their brokenness. Get fucked, systemd. This is the kind of shit that would finally drive me to BSDland
#
The Dordogne Valley: What to Expect
French Foodie in Dublin writes and vlogs about the Dordogne Valley, good foodie tips
The Dutch word for "nitpicker" is significantly more sweary
via James Kelleher on Twitter: "'Mierenneuker' — Dutch slang for someone who pays (too much) attention to detail, literally 'ant-fucker'."; and in German, 'Korinthenkacker', "raisin-shitter".
raisins funny words ants dutch german language nit-picking perfectionism
#825394 - systemd kill background processes after user logs out - Debian Bug report logs
Systemd breaks UNIX behaviour which has been standard practice for 30 years:
It is now indeed the case that any background processes that were still running are killed automatically when the user logs out of a session, whether it was a desktop session, a VT session, or when you SSHed into a machine. Now you can no longer expect a long running background processes to continue after logging out. I believe this breaks the expectations of many users. For example, you can no longer start a screen or tmux session, log out, and expect to come back to it.
#
-
Geofencing used for evil:
What Flynn realized is that he could use [ad targeting] to infer that a woman might be seeking an abortion, and to target her for ads from anti-choice groups [using geofenced advertising]. "We can reach every Planned Parenthood in the U.S.," he wrote in a PowerPoint display sent to potential clients in February. The Powerpoint included a slide titled "Targets for Pro-Life," in which Flynn said he could also reach abortion clinics, hospitals, doctors' offices, colleges, and high schools in the United States and Canada, and then "[d]rill down to age and sex." "We can gather a tremendous amount of information from the [smartphone] ID," he wrote. "Some of the break outs include: Gender, age, race, pet owners, Honda owners, online purchases and much more." Flynn explained that he would then use that data to send anti-choice ads to women "while they're at the clinic."
geofencing grim-meathook-future abortion phones smartphones pro-choice ads
-
Rapid Fire is a special event we started hosting at our own in-person CTFs in 2014. The idea is pretty simple: Create several CTF challenges that can be solved in a few minutes each. Set up the challenges on 4 identical computers with some basic tools. Mirror the player's screens so the audience can watch their actions. Whoever solves the most challenges the fastest wins. This event is interesting for a number of reasons: the players are under intense pressure, as everything they do is being watched by several people; the audience can watch several different approaches to the same problems; and people can follow along fairly easily with what is going on with the challenges.
With e-sports-style video! -
Twitter are open sourcing their Storm replacement, and moving it to an independent open source foundation
open-source twitter heron storm streaming architecture lambda-architecture
Why the Very Silly Oracle v. Google Trial Actually Matters
If it's illegal to write clean room implementations of APIs, then no one has clean hands. The now-shelved open source project Apache Harmony, like Android, reimplemented Java SE, and tech giant IBM contributed code to that project. Oracle itself built its business off a proprietary implementation of SQL, which was created by IBM. The proposition "Reimplementations of APIs are infringements" creates a recursive rabbit hole of liability that spans across the industry. Even the very 37 Java APIs at issue in this trial contain reimplementations of other APIs. Google witness Joshua Bloch—who, while at Sun Microsystems, wrote many of the Java APIs—testified that specific Java APIs are reimplementations of other APIs from Perl 5 and the C programming language.
#
-
GitLab continue to out-innovate Github, which is just wanking around with breaking the UI these days
-
'The algorithm of Lamport timestamps is a simple algorithm used to determine the order of events in a distributed computer system. As different nodes or processes will typically not be perfectly synchronized, this algorithm is used to provide a partial ordering of events with minimal overhead, and conceptually provide a starting point for the more advanced vector clock method. They are named after their creator, Leslie Lamport.' See also vector clocks (which I think would be generally preferable nowadays).
vector-clocks distributed programming algorithm clocks time leslie-lamport coding distcomp
#
100 thieves steal $13m in three hours from cash machines across Japan
'Police believe that as many as 100 people, none of whom have been apprehended, worked together using forged credit cards containing account details illegally obtained from a bank in South Africa. The culprits used the fake cards at 1,400 convenience store automated teller machines on the morning of 15 May, according to police. Each made a single withdrawal of 100,000 yen – the maximum allowed by the cash machines.' 1,600 forged/stolen credit card credentials from a single bank, then a synchronised attack made possible by the eventually-consistent ledger model of ATM accounting. (via William Gibson)
Revealed: How copyright law is being misused to remove material from the internet
Automated DMCA takedowns used to fraudulently censor online content.
In fact, no copyright infringement had occurred at all. Instead, something weirder had happened. At some point after Narey posted her comments on Mumsnet, someone had copied the entire text of one of her posts and pasted it, verbatim, to a spammy blog titled "Home Improvement Tips and Tricks". The post, headlined "Buildteam interior designers" was backdated to September 14 2015, three months before Narey had written it, and was signed by a "Douglas Bush" of South Bend, Indiana. The website was registered to someone quite different, though: Muhammed Ashraf, from Faisalabad, Pakistan. Quite why Douglas Bush or Muhammed Ashraf would be reviewing a builder based in Clapham is not explained in "his" post. BuildTeam says it has no idea why Narey's review was reposted, but that it had nothing to do with it. "At no material times have we any knowledge of why this false DCMA take down was filed, nor have we contracted any reputation management firms, or any individual or a group to take such action on our behalf. Finally, and in conjunction to the above, we have never spoken with a 'Douglas Bush,' or a 'Muhammed Ashraf.'"
fraud censorship mumsnet dmca takedowns google automation copyright
3 Reasons AWS Lambda Is Not Ready for Prime Time
This totally matches my own preconceptions ;)
When we at Datawire tried to actually use Lambda for a real-world HTTP-based microservice [...], we found some uncool things that make Lambda not yet ready for the world we live in: Lambda is a building block, not a tool; Lambda is not well documented; Lambda is terrible at error handling Lung skips these uncool things, which makes sense because they'd make the tutorial collapse under its own weight, but you can't skip them if you want to work in the real world. (Note that if you're using Lambda for event handling within the AWS world, your life will be easier. But the really interesting case in the microservice world is Lambda and HTTP.)
aws lambda microservices datawire http api-gateway apis https python ops
-
holy crap, this is dystopian:
The first time Paul Zilly heard of his score — and realized how much was riding on it — was during his sentencing hearing on Feb. 15, 2013, in court in Barron County, Wisconsin. Zilly had been convicted of stealing a push lawnmower and some tools. The prosecutor recommended a year in county jail and follow-up supervision that could help Zilly with "staying on the right path." His lawyer agreed to a plea deal. But Judge James Babler had seen Zilly's scores. Northpointe's software had rated Zilly as a high risk for future violent crime and a medium risk for general recidivism. "When I look at the risk assessment," Babler said in court, "it is about as bad as it could be." Then Babler overturned the plea deal that had been agreed on by the prosecution and defense and imposed two years in state prison and three years of supervision.
dystopia law policing risk risk-assessment northpointe racism fortune-telling crime
Guillermo Del Toro's Tweetstorm About John Carpenter
'Regarding [John] Carpenter: We all talk about inequalities in film. We can add a huge one: Genre inequality. Horror will always be punk rock!'
#
For World's Newest Scrabble Stars, SHORT Tops SHORTER
Nigeria's scrabble team are kicking ass with short-word strats.
" 'What would the robot do?' is now the key question in Scrabble," said Mr. Fatsis. Often, he said, the robot plays five letters: "There are inefficiencies in the game that you can exploit by having a mastery of those intermediate-length words."
#
-
Today in nose-leech news -- the paper!
Principal Findings: A new genus and species of leech from Perú was found feeding from the nasopharynx of humans. Unlike any other leech previously described, this new taxon has but a single jaw with very large teeth. Phylogenetic analyses of nuclear and mitochondrial genes using parsimony and Bayesian inference demonstrate that the new species belongs among a larger, global clade of leeches, all of which feed from the mucosal surfaces of mammals. Conclusions: This new species, found feeding from the upper respiratory tract of humans in Perú, clarifies an expansion of the family Praobdellidae to include the new species Tyrannobdella rex n. gen. n.sp., along with others in the genera Dinobdella, Myxobdella, Praobdella and Pintobdella. Moreover, the results clarify a single evolutionary origin of a group of leeches that specializes on mucous membranes, thus, posing a distinct threat to human health.
leeches nose-leech papers science species tyrannobdella-rex horror
Bike thief reveals tricks of the trade in this shockingly candid interview
This is an eye-opener:
A former bicycle thief has revealed the tricks of the trade in an interview, which clearly and shockingly shows the extent that thieves will go to in order to steal a bike. He talks about the motivations behind the theft, the tools used to crack locks and how the bikes were moved around and sold for a significant sum. He also gives tips on how to prevent your bike from being stolen. [...] 'Don't be fooled by Kryptonite locks, they're not as tough as made out to be. Also D-bars with tubular locks, never use them, they're the most easy to pick with a little tool. It's small and discreet, no noise and it looks like you are just unlocking your bike. With the bolt cutters we would go out on high performance motorbikes, two men on a bike.'
bikes locks bike-locks security london theft lockpicking d-locks
#
How Trump's troll army is cashing in on his campaign
Of the dozens of Trump pages seemingly run by click-farms, just one responded to our request for an interview, though the anonymous operators of the Trumpians fan page declined to provide the name of their company, citing the "volatility of Trump haters." Trump's Facebook page is the only one of over 100 the company runs that's dedicated to an individual politician. "The other [candidates] don't have any value from a merchandise perspective ," the operator said by Facebook Messenger.
click-farms spam donald-trump politics us-politics facebook trolls
_DataEngConf: Parquet at Datadog_
"How we use Parquet for tons of metrics data". good preso from Datadog on their S3/Parquet setup
datadog parquet storage s3 databases hadoop map-reduce big-data
Should create a separate Hystrix Thread pool for each remote call?
Excellent advice on capacity planning and queueing theory, in the context of Hystrix. Should I use a single thread pool for all dependency callouts, or independent thread pools for each one?
threadpools pooling hystrix capacity queue-theory queueing queues failure resilience soa microservices
-
'The database of Irish nonprofits'. Excellent stuff!
Far more drivers break red lights in Dublin than cyclists
'of all the red light violations [filmed by red light cameras at Blackhall Place and Con Colbert Road by the RPA in 2011,] approximately 15% were committed by cyclists, with almost 85% committed by motor vehicles.'
-
RIP. "Big Dead Place" is a fantastic document of "M*A*S*H on ice", as the London Times called it, and one of my favourite books. See also http://feralhouse.com/nick-johnson-rip/ for another eulogy from his publishers
big-dead-place nick-johnson rip eulogies books reading history antarctica exploration raytheon bureaucracy
#
-
Gradle plugin that allows easy integration with the infer static analyzer
"You Can't Copyright Klingon" Means Paramount Is In Trouble
The Language Creation Society filed an amicus brief claiming that Klingon is a real language and therefore not subject to copyright. To reiterate: the fandom of Star Trek elevated a language invented in 1984 by Marc Okrand for Star Trek III: The Search for Spock to the point it is taught in colleges and spoken as a living language. So it isn't Star Trek anymore: it is real. [...] the entire legal brief is impossible to reprint due to limits in our non-Klingon font system, but even the motion includes Klingon-translated passages that accuse Paramount of being "arrogant" and "pathetic".
#
Westminster social engineering to blame for 'Glasgow effect' mortality rate
This is quite significant -- scientific proof that austerity/social engineering policies cause higher mortality rates:
Researchers found that the historic effect of overcrowding was an important factor and highlighted the strategies of local government, which prioritised the regeneration of the city centre over investment in the cities housing schemes as having a significant impact on the health of Glaswegians. Data shows that Glasgow authorities spent far less on housing repairs, leaving people's homes poorly maintained and subject to damp. David Walsh, of the Glasgow Centre for Population Health, said that their work proved that poor health had political causes and could not simply be attributed to individual lifestyle choices.
glasgow-effect scotland poverty glasgow lifestyle health mortality housing policies uk
#
Key Metrics for Amazon Aurora | AWS Partner Network (APN) Blog
Very DataDog-oriented, but some decent tips on monitorable metrics here
In Oracle v. Google, a Nerd Subculture Is on Trial
"The G part stands for GNU?" Alsup asked in disbelief. "Yes," said Schwartz on the stand. "That doesn't make any sense," said the 71-year-old Clinton appointee.
Historic computers look super sexy in this new photo series by Docubyte and Ink
Wow, these look amazing:
The IBM 1401 and Alan Turing's Pilot ACE (shown below) are among the computers featured in the series by photographer Docubyte and production studio Ink.
Kodak Had a Secret Nuclear Reactor Loaded With Enriched Uranium Hidden In a Basement
non-proliferation? what's that?
Kodak's purpose for the reactor wasn't sinister: they used it to check materials for impurities as well as neutron radiography testing. The reactor, a Californium Neutron Flux multiplier (CFX) was acquired in 1974 and loaded with three and a half pounds of enriched uranium plates placed around a californium-252 core. The reactor was installed in a closely guarded, two-foot-thick concrete walled underground bunker in the company's headquarters, where it was fed tests using a pneumatic system. According to the company, no employees were ever in contact with the reactor. Apparently, it was operated by atomic fairies and unicorns.
kodak nuclear safety non-proliferation scary rochester reactors
Champagne Mojitos Recipe - John Besh
sounds like a decent party starter:
This puckery drink is prepared with rum and fresh mint like a classic mojito, but New Orleans chef John Besh makes it holiday-worthy by topping it with a splash of Champagne.
cocktails recipes champagne mojito sugar water rum lime mint sparkling-wine
Cava and Pomegranate Cocktails Recipe - José Andrés
I've made a variant on this, good cava cocktail
Southside Royale Recipe - Eric Alperin
variant on the French 75 with lime juice in place of lemon
#
Virgin Media Ireland hate people working from home
What the hell, Virgin?
Section 12: Use of Virtual Private Network (VPN) As stated above, the Virgin Media Services are for residential use only and we do not support the use of VPN. If we find you are using VPN we may instruct you to stop using it and you must comply with this request. This is in order to prevent problems with our network and other Internet users.
virgin-media virgin upc isps ireland teleworking telecommuting home vpns vpn
About to leave UPC due to (lack of) port forwarding - Boards.ie
Virgin Media/UPC seem to have silently deployed an IPv6 "carrier-grade NAT" setup called "DS-Lite" -- ie. all customers now get just a routable IPv6 address, and share a small pool of IPv4 NATs. This breaks a multitude of useful services, including UDP IPSec VPNs it seems
udp vpns isps virgin-media virgin ireland ds-lite ipv6 tunnelling networking nat ipv4
Ireland will need referendum to create EU court for patents
omg. Sean "Irish SOPA" Sherlock dealing with the important issues once again -- in this case the bloody "Unified Patent Court"
-
In his 1962 book, The Image: A Guide to Pseudo-Events in America, former Librarian of Congress Daniel J. Boorstin describes a world where our ability to technologically shape reality is so sophisticated, it overcomes reality itself. "We risk being the first people in history," he writes, "to have been able to make their illusions so vivid, so persuasive, so 'realistic' that they can live in them."
algorithms facebook ethics filtering newsfeed conspiracy-theories twitter viral crazy
World's first vanity gTLD goes live
".richardli". TLDs are now officially beyond a joke
#
Open Whisper Systems >> Blog >> Reflections: The ecosystem is moving
Very interesting post on federation vs centralization for new services:
One of the controversial things we did with Signal early on was to build it as an unfederated service. Nothing about any of the protocols we've developed requires centralization; it's entirely possible to build a federated Signal Protocol based messenger, but I no longer believe that it is possible to build a competitive federated messenger at all.
development encryption communication network-effects federation signal ip protocols networking smtp platforms
CD at LMAX: Testing into Production and Back Again
Chock-full of excellent build/test ideas from LMAX's Continuous Delivery setup. Lots of good ideas to steal
#
Chinese censorship: arbitrary rule changes are a form of powerful intermittent reinforcement
China's Internet censors are capricious and impossible to predict -- but this isn't because China's censors are incompetent, rather, they're tapping into one of the most powerful forms of conditioning, the uncertainty born of intermittent reinforcement. [...] As C Custer writes at Tech in Asia, this caprice is by design: by not specifying a set of hard and fast rules, but rather the constant risk of being taken down for crossing some invisible line, China's censors inspire risk-aversion in people who rely on the net to be heard or earn their livings. It's what Singaporeans call "out of bounds," the unspecified realm of things you mustn't, shouldn't or won't want to enter.
risk risk-aversion censorship control china politics enforcement crime self-censorship
Dublin & Wicklow Walks » Family Walks
These are a great selection. Gonna be doing one of these every weekend if possible, now that the 2 year old can just about handle it ;)
#
-
command line utility that performs an HTML element selection on HTML content passed to the stdin. Using css selectors that everybody knows. Since input comes from stdin and output is sent to stdout, it can easily be used inside traditional UNIX pipelines to extract content from webpages and html files. tq provides extra formating options such as json-encoding or newlines squashing, so it can play nicely with everyones favourite command line tooling.
#
Apple Stole My Music. No, Seriously.
some amazingly terrible product decisions here. Deleting local copies of unreleased WAV files -- on the assumption that the user will simply listen to them streamed down from Apple Music -- that is astonishingly bad, and it's amazing they didn't consider the "freelance composer" use case at all. (via Tony Finch)
apple music terrible wav sound copyright streaming apple-music design product fail
-
Purpose-built in 1898, the telephone exchange in Temple Bar was Dublin's first automatic telephone exchange. Much like its newer neighbor, Internet House, it stood as a technological beacon shining through the luddite fog. With this in mind the Irish Citizen Army targeted the Telephone Exchange in 1916 as one of the communication hubs for the island. While many of us grew up learning of a history of 'blood sacrifice' and the futility of the Easter Rising, the truth is that the attack was meticulously planned both militarily and logistically. Sixty communication points around Dublin were hit in an effort to cut off all contact between British military forces within Ireland and to the 'mainland'. The hope being that reserves and reinforcements would be delayed or misinformed.[...] Unfortunately for the rebels they could not take the Temple Bar exchange. A failure that would prove disastrous.
#
Waste charges unpaid by 50% of residents in city litter blackspot
as Paul McDonnell noted: this one line tells you everything you need to know about DCC's ability to enforce the rules: 'in some of the bags inspected previously issued litter fines were found'. Pathetic
-
This conceptual collection consists of eight 6:1 scale versions of classic LEGO bricks, each fully functional in one way or the other. Including eight matching photo montages, a homage to the box cover art for the classic "Legoland Space" line. Hultén - "Like most people, I was raised by Lego. For this project, I chose to work with a set of decorated bricks from the iconic 79-87 "Legoland Space" line. These were bricks that would trigger my imagination as a child. 25 years have passed, and they still trigger"
ERMAHGERD (faints) BTrDB: Optimizing Storage System Design for Timeseries Processing
interesting, although they punt to Ceph for storage and miss out the chance to make a CRDT
storage trees data-structures timeseries delta-delta-coding encoding deltas
?Why I Hate Security, Computers, and the Entire Modern Banking System | Motherboard
I am honestly amazed the US banking system still works this way, after over a decade of rampant identity theft:
I cannot count the number of times I've freely given out my routing and account numbers—in emails, in webforms, in paperwork. This is because it's necessary for other people to know my routing number and account number in order for them to send me money. But apparently, with that same information, they can also snatch money straight from my account. What kind of insane system is this? There's two factor authentication, there's one factor authentication, and then there's this, which I think I can call zero factor authentication.
identity-theft phishing banking banks usa authentication 2fa 0fa security
#
-
Cropping, scaling, and resizing images on the fly, for free, with GAE. Great service, wish AWS had something similar
App Engine API has a very useful function to extract a magic URL for serving the images when uploaded into the Cloud Storage. get_serving_url() returns a URL that serves the image in a format that allows dynamic resizing and cropping, so you don't need to store different image sizes on the server. Images are served with low latency from a highly optimized, cookieless infrastructure.
gae google app-engine images scaling cropping image-processing thumbnails google-cloud
Ex-surgeon duped into being €100k drug mule
Oh man. This is so sad:
Soriano, who had travelled to Ireland from Bogota via Panama and Paris, told customs officials that a red bag he was carrying contained a gift for banking officials which would facilitate the transfer of a $2.3m inheritance from a long-lost relative he had never heard of until recently. He was very co-operative with the officials and agreed to allow them x-ray and examine the bag. It was found to contain 1.86kg of cocaine in three packets. Sgt Finnegan said gardaí were initially sceptical that Soriano could have fallen for the scam but, as interviews went on, they became aware that there were underlying issues. Gardaí found documentation that Soriano had printed out about other phishing scams. He said that he knew they were scams but he was lonely and would respond to them for "a little bit of fun". Sgt Finnegan said that, despite this, he remained adamant that the inheritance was still due to be claimed.
Bizarrely not the first prominent surgeon to fall victim to 419 scammers.Wikipedia's Piracy Police Are Ruining the Developing World's Internet Experience | Motherboard
Oh dear.
The Wikimedia Foundation told me last month that it has been aware of people using Wikipedia Zero for file sharing for about a year, and says that there are no plans to pull out of any countries because of piracy. But that hasn't stopped rogue Wiki users from suggesting it anyway, and members of the task force have gotten Wikimedia Bangladesh to plead with the pirates to stop contributing to an "increasingly negative perception of Bangladesh in many different sectors."
wikipedia wikimedia bangladesh filesharing piracy wikipedia-zero copyright
Go best practices, six years in
from Peter Bourgon. Looks like a good list of what to do and what to avoid
raboof/nethogs: Linux 'net top' tool
NetHogs is a small 'net top' tool. Instead of breaking the traffic down per protocol or per subnet, like most tools do, it groups bandwidth by process.
nethogs cli networking performance measurement ops linux top
The Airplane Seating Arrangement that Triggers 'Air Rage'
The presence of a first-class cabin, and having to walk through it to get to economy, is a triggering factor for "air rage" incidents:
As lead researcher Katherine DeCelles explained to Gizmodo, airplanes are like a miniature version of class-based society. "It's a small world of the greater society that we live in, though one that's greatly concentrated," she said. Traveling by plane is stressful enough, but DeCelles believes that seating inequality on airplanes often serves as "the straw that breaks the camel's back," and that air rage can be partly explained and understood through the lens of social inequality.
The Challenges of Container Configuration // Speaker Deck
Some good advice on Docker metadata/config from Gareth Rushgrove
docker metadata configuration build devops dev containers slidfes
#
CoreOS and Prometheus: Building monitoring for the next generation of cluster infrastructure
Ooh, this is a great plan. :applause:
Enabling GIFEE — Google Infrastructure for Everyone Else — is a primary mission at CoreOS, and open source is key to that goal. [....] Prometheus was initially created to handle monitoring and alerting in modern microservice architectures. It steadily grew to fit the wider idea of cloud native infrastructure. Though it was not intentional in the original design, Prometheus and Kubernetes conveniently share the key concept of identifying entities by labels, making the semantics of monitoring Kubernetes clusters simple. As we discussed previously on this blog, Prometheus metrics formed the basis of our analysis of Kubernetes scheduler performance, and led directly to improvements in that code. Metrics are essential not just to keep systems running, but also to analyze and improve application behavior. All things considered, Prometheus was an obvious choice for the next open source project CoreOS wanted to support and improve with internal developers committed to the code base.
monitoring coreos prometheus metrics clustering ops gifee google kubernetes
Let Them Make Noise: A 'Dining Club' Invites Toddlers - NYTimes.com
This is a great idea. I miss eating out, and this is why:
Throughout our three-hour meal, babies cried, mothers nursed, toddlers shrieked and farro grains flew, but the atmosphere was surprisingly leisurely. There was no reason to be self-conscious about a crying-nursing-dancing child because everyone knew every other parent was in the same boat. Or would be in a few seconds. So we relaxed and ate. This is not fine dining as I once knew it, and that's O.K. That's what date night is for. But my daughter got her first lesson in how to behave at a fancy restaurant. And I got to finish a delicious meal while it was still warm, toddler in tow.
Image Dithering: Eleven Algorithms and Source Code
Nice demos
#
A poem about Silicon Valley, made up of Quora questions about Silicon Valley
Why do so many startups fail? Why are all the hosts on CouchSurfing male? Are we going to be tweeting for the rest of our lives? Why do Silicon Valley billionaires choose average-looking wives? What makes a startup ecosystem thrive? What do people plan to do once they're over 35? Is an income of $160K enough to survive? What kind of car does Mark Zuckerberg drive? Are the real estate prices in Palo Alto crazy? Do welfare programs make poor people lazy? What are some of the biggest lies ever told? How do I explain Bitcoin to a 6-year-old? Why is Powdered Alcohol not successful so far? How does UberX handle vomiting in the car? Is being worth $10 million considered 'rich'? What can be causing my upper lip to twitch? Why has crowdfunding not worked for me? Is it worth pre-ordering a Tesla Model 3? How is Clinkle different from Venmo and Square? Can karma, sometimes, be unfair? Why are successful entrepreneurs stereotypically jerks? Which Silicon Valley company has the best intern perks? What looks easy until you actually try it? How did your excretions change under a full Soylent diet? What are alternatives to online dating? Is living in small apartments debilitating? Why don't more entrepreneurs focus on solving world hunger? What do you regret not doing when you were younger?
funny tech poetry silicon-valley humour bitcoin soylent 2016
#
Some great factoids about Glasnevin Cemetery
local landmark and significant chunk of Dublin history. I like this one:
Another odd thing was that people from Dublin had to be buried before noon. This was due to the fact that many funerals stopping at the gate would end up so late in the pub the gates would be closed. A number of times the sextant would open up in the morning to find a coffin or two aganst the gates. For years I thought this was made up but it turns out to be true. A friend had a copy of the cemetary bye laws from (I think) around 1908 and it was in there. I think the rule was if you lived within 7 miles of the GPO you had to be buried before 12 noon.
-
Results: We obtained 20?882 survey responses (94?606 preferences) from 27 EU member countries. Respondents recognized the benefits of storing electronic health information, with 75.5%, 63.9%, and 58.9% agreeing that storage was important for improving treatment quality, preventing epidemics, and reducing delays, respectively. Concerns about different levels of access by third parties were expressed by 48.9% to 60.6% of respondents. On average, compared to devices or systems that only store basic health status information, respondents preferred devices that also store identification data (coefficient/relative preference 95% CI?=?0.04 [0.00-0.08], P?=?0.034) and information on lifelong health conditions (coefficient?=?0.13 [0.08 to 0.18], P?<?0.001), but there was no evidence of this for devices with information on sensitive health conditions such as mental and sexual health and addictions (coefficient?=??0.03 [?0.09 to 0.02], P?=?0.24). Respondents were averse to their immediate family (coefficient?=??0.05 [?0.05 to ?0.01], P?=?0.011) and home care nurses (coefficient?=??0.06 [?0.11 to ?0.02], P?=?0.004) viewing this data, and strongly averse to health insurance companies (coefficient?=??0.43 [?0.52 to 0.34], P?<?0.001), private sector pharmaceutical companies (coefficient?=??0.82 [?0.99 to ?0.64], P?<?0.001), and academic researchers (coefficient?=??0.53 [?0.66 to ?0.40], P?<?0.001) viewing the data. Conclusions: Storing more detailed electronic health data was generally preferred, but respondents were averse to wider access to and sharing of this information. When developing frameworks for the use of electronic health data, policy makers should consider approaches that both highlight the benefits to the individual and minimize the perception of privacy risks.
Via Antoin. Inside "Emojigeddon": The Fight Over The Future Of The Unicode Consortium
Michael "evertype" Everson in the news!
The Make: Weekend Projects Thumbnail Guide To Soldering
man, I wish I had this 30 years ago. now I know what stuff I need to get to make my occasional solders less of a PITA
#
Exclusive: SWIFT bank network says aware of multiple cyber fraud incidents
"SWIFT is aware of a number of recent cyber incidents in which malicious insiders or external attackers have managed to submit SWIFT messages from financial institutions' back-offices, PCs or workstations connected to their local interface to the SWIFT network," the group warned customers on Monday in a notice seen by Reuters.
Ouch. They seem to be indicating that they're all phishing/impersonation-based attacks.Bodyhackers are all around you, they're called women
I have two cyborg implants. One is in my hand, and it lets my unlock phones and doors by waving at them. The other is in my uterus, and it lets me control my own fertility.
-
Amazing deep dive into the graphic design of 1980s sci-fi classic, Alien, in particular Ron Cobb's_Semiotic Standard For All Commercial Trans-Stellar Utility Lifter And Heavy Element Transport Spacecraft_ and its application aboard the Weylan-Yutani Nostromo
fonts typography movies cinema alien sf history 1980s ron-cobb graphic-design
#
Bots won't replace apps. Better apps will replace apps
As I'll explain, messenger apps' apparent success in fulfilling such a surprising array of tasks does not owe to the triumph of "conversational UI." What they've achieved can be much more instructively framed as an adept exploitation of Silicon Valley phone OS makers' growing failure to fully serve users' needs, particularly in other parts of the world. Chat apps have responded by evolving into "meta-platforms." Many of the platform-like aspects they've taken on to plaster over gaps in the OS actually have little to do with the core chat functionality. Not only is "conversational UI" a red herring, but as we look more closely, we'll even see places where conversational UI has breached its limits and broken down.
apps bots chatops chat ui messaging silicon-valley agents alexa siri phones
#
How I Hacked Facebook, and Found Someone's Backdoor Script
Great writeup of a practical pen test. Those crappy proprietary appliances that get set up "so the CEO can read his email on the road" etc. are always a weak spot
Anti-innovation: EU excludes open source from new tech standards
EC up to its old anti-competitive tricks:
The European Commission is surprisingly coy about what exactly ['open'] means in this context. It is only on the penultimate page of the ICT Standardisation Priorities document that we finally read the following key piece of information: "ICT standardisation requires a balanced IPR [intellectual property rights] policy, based on FRAND licensing terms." It's no surprise that the Commission was trying to keep that particular detail quiet, because FRAND licensing—the acronym stands for "fair, reasonable, and non-discriminatory"—is incompatible with open source, which will therefore find itself excluded from much of the EU's grand new Digital Single Market strategy. That's hardly a "balanced IPR policy."
I am Alex St. John's Daughter, and He is Wrong About Women in Tech — Medium
Great, great post from Amilia St. John, responding to the offensive sexist crap spewed by her father, Alex St. John
sexism career tech amilia-st-john alex-st-john jobs work feminism
-
The history of this is fascinating:
Today's pirate libraries have their roots in the work of Russian academics to digitize texts in the 1990s. Scholars in that part of the world had long had a thriving practice of passing literature and scientific information underground, in opposition to government censorship—part of the samizdat culture, in which banned documents were copied and passed hand to hand through illicit channels. Those first digital collections were passed freely around, but when their creators started running into problems with copyright, their collections "retreated from the public view," writes Balázs Bodó, a piracy researcher based at the University of Amsterdam. "The text collections were far too valuable to simply delete," he writes, and instead migrated to "closed, membership-only FTP servers." [....] There's always been osmosis within the academic community of copyrighted materials from people with access to scholar without. "Much of the life of a research academic in Kazakhstan or Iran or Malaysia involves this informal diffusion of materials across the gated walls of the top universities," he says.
pirates pirate-libraries libraries archival history russia ussr samizdat samizdata academia papers
#
[Updated] Using a Dyson hand dryer is like setting off a viral bomb in a bathroom | Ars Technica
Clumping the data from all six heights together, the Dyson produced 60 times more plaques than the warm air dryer and 1,300 times more than paper towels. Of the viruses launched by the jet dryer, 70 percent were at the height of a small child's face.
(vomit)Building a Regex Search Engine for DNA | Hacker News
The original post is pretty mediocre -- a search engine which handles a corpus of "thousands" of plasmids from "a scientist's personal library", and which doesn't handle fuzzy matches? I think that's called grep -- but the HN comments are good
grep regular-expressions hacker-news strings dna genomics search elasticsearch
#
-
Prepaid talk+text+data or data-only mobile SIM cards, delivered to your home or hotel, prior to visiting the US. great service for temporary US business visits
visiting us usa zip-sim sims mobile-phones travel phones mobile travelling data
Detecting the use of "curl | bash" server side
tl;dr:
The better solution is never to pipe untrusted data streams into bash. If you still want to run untrusted bash scripts a better approach is to pipe the contents of URL into a file, review the contents on disk and only then execute it.
The Melancholy Mystery of Lullabies - NYTimes.com
Fascinating article on lullabies:
One way a mother might bond with a newborn is by sharing her joy; another way is by sharing her grief or frustration. We see this in songs across time. A 200-year-old Arabic lullaby still sung today goes: I am a stranger, and my neighbors are strangers; I have no friends in this world. Winter night and the husband is absent. And an old Spanish lullaby from Asturias, written down by the poet Federico García Lorca, goes: This little boy clinging so Is from a lover, Vitorio, May God, who gave, end my woe, Take this Vitorio clinging so. We assume the sound of these songs is sweet, as no lullaby endures without being effective at putting babies to sleep. Think of ''Rock-a-bye Baby,'' the way it tenderly describes an infant and its cradle falling to the ground: The singer gets to speak a fear, the baby gets to rest; the singer tries to accommodate herself to a possible loss that has for most of human history been relatively common, and the baby gets attentive care. In the Arabic and Spanish lullabies, the singers get to say something to the one being — their new burden, their new love — who can't and won't judge or discipline them for saying it. When even relatively happy, well-supported people become the primary caretaker of a very small person, they tend to find themselves eddied out from the world of adults. They are never alone — there is always that tiny person — and yet they are often lonely. Old songs let us feel the fellowship of these other people, across space and time, also holding babies in dark rooms.
New Oil-Based Cityscapes Set at Dawn and Dusk by Jeremy Mann
lovely art via This Is Colossal
Amazon S3 Transfer Acceleration
The AWS edge network has points of presence in more than 50 locations. Today, it is used to distribute content via Amazon CloudFront and to provide rapid responses to DNS queries made to Amazon Route 53. With today's announcement, the edge network also helps to accelerate data transfers in to and out of Amazon S3. It will be of particular benefit to you if you are transferring data across or between continents, have a fast Internet connection, use large objects, or have a lot of content to upload. You can think of the edge network as a bridge between your upload point (your desktop or your on-premises data center) and the target bucket. After you enable this feature for a bucket (by checking a checkbox in the AWS Management Console), you simply change the bucket's endpoint to the form BUCKET_NAME.s3-accelerate.amazonaws.com. No other configuration changes are necessary! After you do this, your TCP connections will be routed to the best AWS edge location based on latency. Transfer Acceleration will then send your uploads back to S3 over the AWS-managed backbone network using optimized network protocols, persistent connections from edge to origin, fully-open send and receive windows, and so forth.
-
Earlier this year, I asked a question on Stack Overflow about a data structure for loaded dice. Specifically, I was interested in answering this question: "You are given an n-sided die where side i has probability pi of being rolled. What is the most efficient data structure for simulating rolls of the die?" This data structure could be used for many purposes. For starters, you could use it to simulate rolls of a fair, six-sided die by assigning probability 1616 to each of the sides of the die, or a to simulate a fair coin by simulating a two-sided die where each side has probability 1212 of coming up. You could also use this data structure to directly simulate the total of two fair six-sided dice being thrown by having an 11-sided die (whose faces were 2, 3, 4, ..., 12), where each side was appropriately weighted with the probability that this total would show if you used two fair dice. However, you could also use this data structure to simulate loaded dice. For example, if you were playing craps with dice that you knew weren't perfectly fair, you might use the data structure to simulate many rolls of the dice to see what the optimal strategy would be. You could also consider simulating an imperfect roulette wheel in the same way. Outside the domain of game-playing, you could also use this data structure in robotics simulations where sensors have known failure rates. For example, if a range sensor has a 95% chance of giving the right value back, a 4% chance of giving back a value that's too small, and a 1% chance of handing back a value that's too large, you could use this data structure to simulate readings from the sensor by generating a random outcome and simulating the sensor reading in that case. The answer I received on Stack Overflow impressed me for two reasons. First, the solution pointed me at a powerful technique called the alias method that, under certain reasonable assumptions about the machine model, is capable of simulating rolls of the die in O(1)O(1) time after a simple preprocessing step. Second, and perhaps more surprisingly, this algorithm has been known for decades, but I had not once encountered it! Considering how much processing time is dedicated to simulation, I would have expected this technique to be better- known. A few quick Google searches turned up a wealth of information on the technique, but I couldn't find a single site that compiled together the intuition and explanation behind the technique.
(via Marc Brooker)via:marcbrooker algorithms probability algorithm coding data-structures alias dice random
#
Donald Rumsfeld wrote the best memo ever: "Issues w/Various Countries"
Paraphrasing: "I have made a massive mess of US foreign policy and the whole world is falling apart. Have you fixed it for me yet?" Right in the middle of the biggest Middle Eastern shitstorm ever created, April 7, 2003. Heck of a job, Rummie
donald-rumsfeld inept gobshites korea pakistan issues world-politics funny facepalm george-w-bush iraq syria libya amazing
The problems with forcing regular password expiry
The new password may have been used elsewhere, and attackers can exploit this too. The new password is also more likely to be written down, which represents another vulnerability. New passwords are also more likely to be forgotten, and this carries the productivity costs of users being locked out of their accounts, and service desks having to reset passwords. It's one of those counter-intuitive security scenarios; the more often users are forced to change passwords, the greater the overall vulnerability to attack. What appeared to be a perfectly sensible, long-established piece of advice doesn't, it turns out, stand up to a rigorous, whole-system analysis. CESG now recommend organisations do not force regular password expiry.
cesg recommendations guidelines security passwords expiry uk gchq
#
-
good rules of thumb for variable naming, from ex-coworker Jacob Gabrielson
Canadian Police Obtained BlackBerry's Global Decryption Key in 2010
According to technical reports by the Royal Canadian Mounted Police that were filed in court, law enforcement intercepted and decrypted roughly one million PIN-to-PIN BlackBerry messages in connection with the probe. The report doesn't disclose exactly where the key — effectively a piece of code that could break the encryption on virtually any BlackBerry message sent from one device to another — came from. But, as one police officer put it, it was a key that could unlock millions of doors. Government lawyers spent almost two years fighting in a Montreal courtroom to keep this information out of the public record.
canada crime encryption security blackberry crypto rcmp police rogers montreal rim
#
-
Ouch, multi-region outage:
At 14:50 Pacific Time on April 11th, our engineers removed an unused GCE IP block from our network configuration, and instructed Google's automated systems to propagate the new configuration across our network. By itself, this sort of change was harmless and had been performed previously without incident. However, on this occasion our network configuration management software detected an inconsistency in the newly supplied configuration. The inconsistency was triggered by a timing quirk in the IP block removal - the IP block had been removed from one configuration file, but this change had not yet propagated to a second configuration file also used in network configuration management. In attempting to resolve this inconsistency the network management software is designed to 'fail safe' and revert to its current configuration rather than proceeding with the new configuration. However, in this instance a previously-unseen software bug was triggered, and instead of retaining the previous known good configuration, the management software instead removed all GCE IP blocks from the new configuration and began to push this new, incomplete configuration to the network. One of our core principles at Google is 'defense in depth', and Google's networking systems have a number of safeguards to prevent them from propagating incorrect or invalid configurations in the event of an upstream failure or bug. These safeguards include a canary step where the configuration is deployed at a single site and that site is verified to still be working correctly, and a progressive rollout which makes changes to only a fraction of sites at a time, so that a novel failure can be caught at an early stage before it becomes widespread. In this event, the canary step correctly identified that the new configuration was unsafe. Crucially however, a second software bug in the management software did not propagate the canary step's conclusion back to the push process, and thus the push system concluded that the new configuration was valid and began its progressive rollout.
multi-region outages google ops postmortems gce cloud ip networking cascading-failures bugs
Using jemalloc to get to the bottom of an off-heap Java memory leak
Good technique
#
Easy way to log all queries in mysql without restart
thanks StackOverflow!
Rendezvous hashing - Wikipedia, the free encyclopedia
Rendezvous or Highest Random Weight (HRW) hashing[1][2] is an algorithm that allows clients to achieve distributed agreement on a set of k options out of a possible set of n options. A typical application is when clients need to agree on which sites (or proxies) objects are to assigned to. When k is 1, it subsumes the goals of consistent hashing, using an entirely different method.
hrw hashing hashes consistent-hashing rendezvous-hashing algorithms discovery distributed-computing
Open Sourcing Dr. Elephant: Self-Serve Performance Tuning for Hadoop and Spark
[LinkedIn] are proud to announce today that we are open sourcing Dr. Elephant, a powerful tool that helps users of Hadoop and Spark understand, analyze, and improve the performance of their flows.
neat, although I've been bitten too many times by LinkedIn OSS release quality at this point to jump in....Improving Our Engineering Interview Process
Foursquare on hiring. 'we forgo technical phone interviews whenever possible. They're typically unpleasant for everyone involved and we felt like the environment of a phone screen wasn't conducive to learning about a candidate's abilities comprehensively. Instead we give out a take-home exercise that takes about three hours.'
#
-
'AWS Assume Made Awesome' -- 'Here are Trek10, we work with many clients, and thus work with multiple AWS accounts on a regular (daily) basis. We needed a way to make managing all our different accounts easier. We create a standard Trek10 administrator role in our clients' accounts that we can assume. For security we require that the role assumer have multifactor authentication enabled.'
-
'I would strongly encourage you to avoid repeating the mistakes of testing methodologies that focus entirely on max achievable throughput and then report some (usually bogus) latency stats at those max throughout modes. The techempower numbers are a classic example of this in play, and while they do provide some basis for comparing a small aspect of behavior (what I call the "how fast can this thing drive off a cliff" comparison, or "pedal to the metal" testing), those results are not very useful for comparing load carrying capacities for anything that actually needs to maintain some form of responsiveness SLA or latency spectrum requirements.' Some excellent advice here on how to measure and represent stack performance. Also: 'DON'T use or report standard deviation for latency. Ever. Except if you mean it as a joke.'
performance benchmarking testing speed gil-tene latency measurement hdrhistogram load-testing load
Data Protection Mishap Leaves 55M Philippine Voters at Risk
Every registered voter in the Philippines is now susceptible to fraud and other risks after a massive data breach leaked the entire database of the Philippines' Commission on Elections (COMELEC). While initial reports have downplayed the impact of the leak, our investigations showed a huge number of sensitive personally identifiable information (PII)–including passport information and fingerprint data–were included in the data dump. [....] Based on our investigation, the data dumps include 1.3 million records of overseas Filipino voters, which included passport numbers and expiry dates. What is alarming is that this crucial data is just in plain text and accessible to everyone. Interestingly, we also found a whopping 15.8 million record of fingerprints and a list of people running for office since the 2010 elections. In addition, among the data leaked were files on all candidates running on the election with the filename VOTESOBTAINED. Based on the filename, it reflects the number of votes obtained by the candidate. Currently, all VOTESOBTAINED file are set to have NULL as figure.
fingerprints biometrics philippines authentication data-dumps security hacks comelec e-voting pii passports voting
The dark side of Guardian comments | Technology | The Guardian
Excellent data on abusive commenters
comments data guardian journalism abuse twitter racism sexism
-
The saddest superhero ever
funny pintman dublin ireland alcoholics twitter history pubs
#
Damien Mulley on Twitter: "Item Number 1 for the startup is our hoody."
Legendary Mulley tweetstorm on startup culture
Dan Luu reviews the Site Reliability Engineering book
voluminous! still looks great, looking forward to reading our copy (via Tony Finch)
Koyaanisqatsi trailer recreated using stock footage
'Koyannistocksi is a shot-by-shot remake of the trailer for Godfrey Reggio's Koyaanisqatsi using only stock footage. A testament to Reggio's influence on contemporary motion photography, and the appropriation of his aesthetic by others for commercial means.' Nailed it. This is why I find it hard to watch Koyaanisqatsi nowadays -- its imagery and style have been stolen by so many other filmmakers.
#
Neutered RNG let man rig million dollar lotteries | Ars Technica
A forensic examination found that the generator had code that was installed after the machine had been audited by a security firm that directed the generator not to produce random numbers on three particular days of the year if two other conditions were met. Numbers on those days would be drawn by an algorithm that Tipton could predict [...] All six prizes linked to Tipton were drawn on either Nov. 23 or Dec. 29 between 2005 and 2011.
prng randomness security hacks exploits lottery us audits holes
-
I would only recommend 3d printing to someone who wanted a hobby, and wanted that hobby to be 3d printing, not "having parts made on a 3d printer". The printing itself is the activity. If you have any other primary motivation your parts will fail more often than they'll succeed.
(via burritojustice)via:burritojustice 3d-printing machines parts things hobbies open-source funny
Internet mapping turned a remote farm into a digital hell
I think this a bit of a legal issue for MaxMind:
The trouble for the Taylor farm started in 2002, when a Massachusetts-based digital mapping company called MaxMind decided it wanted to provide "IP intelligence" to companies who wanted to know the geographic location of a computer to, for example, show the person using it relevant ads or to send the person a warning letter if they were pirating music or movies.
#
GCHQ intervenes to prevent catastrophically insecure UK smart meter plan - The Inquirer
GCHQ barged in after spooks cast their eyes over the plans and realised that power companies were proposing to use a single decryption key for communications from the 53 million smart meters that will eventually be installed in the UK.
holy crap.gchq security smart-meters power uk electricity gas infrastructure
Irish drone register allowed access to personal details of 2,000 members
The breach, which allowed registered users to view names, addresses, email addresses and phone numbers of other people registered on the site, was brought to the attention of the authority on Sunday night. In a statement to TheJournal.ie, the IAA revealed it was aware of four users who downloaded the file.
Running Docker on AWS from the ground up
Advantages/disavantages section right at the bottom is good.
ECS, believe it or not, is one of the simplest Schedulers out there. Most of the other alternatives I've tried offer all sorts of fancy bells & whistles, but they are either significantly more complicated to understand (lots of new concepts), take too much effort to set up (lots of new technologies to install and run), are too magical (and therefore impossible to debug), or some combination of all three. That said, ECS also leaves a lot to be desired.
Hungary proposes anti-crypto law
up to 2 years imprisonment for use of apps for encrypted communication
good example of Application-Level Keepalive beating SO_KEEPALIVE
we have now about 100 salt-minions which are installed in remote areas with 3G and satellite connections. We loose connectivity with all of those minions in about 1-2 days after installation, with test.ping reporting "minion did not return". The state was each time that the minions saw an ESTABLISHED TCP connection, while on the salt-master there were no connection listed at all. (Yes that is correct). Tighter keepalive settings were tried with no result. (OS is linux) Each time, restarting the salt-minion fixes the problem immediately. Obviously the connections are transparently proxied someplace, (who knows what happens with those SAT networks) so the whole tcp-keepalive mechanism of 0mq fails.
Also notes in the thread that the default TCP timeout for Azure Load Balancer is 4 minutes: https://azure.microsoft.com/en-us/blog/new-configurable-idle-timeout-for-azure-load-balancer/ . The default Linux TCP keepalive doesn't send until 2 hours after last connection use, and it's a system-wide sysctl (/proc/sys/net/ipv4/tcp_keepalive_time). Further, http://networkengineering.stackexchange.com/questions/7207/why-bgp-implements-its-own-keepalive-instead-of-using-tcp-keepalive notes "some firewalls filter TCP keepalives".tcp keep-alive keepalive protocol timeouts zeromq salt firewalls nat
#
"Racist algorithms" and learned helplessness
Whenever I've had to talk about bias in algorithms, I've tried be careful to emphasize that it's not that we shouldn't use algorithms in search, recommendation and decision making. It's that we often just don't know how they're making their decisions to present answers, make recommendations or arrive at conclusions, and it's this lack of transparency that's worrisome. Remember, algorithms aren't just code. What's also worrisome is the amplifier effect. Even if "all an algorithm is doing" is reflecting and transmitting biases inherent in society, it's also amplifying and perpetuating them on a much larger scale than your friendly neighborhood racist. And that's the bigger issue. [...] even if the algorithm isn't creating bias, it's creating a feedback loop that has powerful perception effects.
The revenge of the listening sockets
More adventures in debugging the Linux kernel:
You can't have a very large number of bound TCP sockets and we learned that the hard way. We learned a bit about the Linux networking stack: the fact that LHTABLE is fixed size and is hashed by destination port only. Once again we showed a couple of powerful of System Tap scripts.
-
git for Cloud Storage. Create distributed, decentralized and versioned repositories that scale infinitely to 100s of millions of files and PBs of storage. Huge repos can be cloned on your local SSD for making changes, committing and pushing back. Oh yeah, and it dedupes too due to BLAKE2 Tree hashing. http://s3git.org
BLAKE2: simpler, smaller, fast as MD5
'We present the cryptographic hash function BLAKE2, an improved version of the SHA-3 finalist BLAKE optimized for speed in software. Target applications include cloud storage, intrusion detection, or version control systems. BLAKE2 comes in two main flavors: BLAKE2b is optimized for 64-bit platforms, and BLAKE2s for smaller architectures. On 64-bit platforms, BLAKE2 is often faster than MD5, yet provides security similar to that of SHA-3. We specify parallel versions BLAKE2bp and BLAKE2sp that are up to 4 and 8 times faster, by taking advantage of SIMD and/or multiple cores. BLAKE2 has more benefits than just speed: BLAKE2 uses up to 32% less RAM than BLAKE, and comes with a comprehensive tree-hashing mode as well as an efficient MAC mode.'
crypto hash blake2 hashing blake algorithms sha1 sha3 simd performance mac
#
When It Comes to Age Bias, Tech Companies Don't Even Bother to Lie
HubSpot's CEO and co-founder, Brian Halligan, explained to the New York Times that this age imbalance was not something he wanted to remedy, but in fact something he had actively cultivated. HubSpot was "trying to build a culture specifically to attract and retain Gen Y'ers," because, "in the tech world, gray hair and experience are really overrated," Halligan said. I gasped when I read that. Could anyone really believe this? Even if you did believe this, what CEO would be foolish enough to say it out loud? It was akin to claiming that you prefer to hire Christians, or heterosexuals, or white people. I assumed an uproar would follow. As it turned out, nobody at HubSpot saw this as a problem. Halligan didn't apologize for his comments or try to walk them back. The lesson I learned is that when it comes to race and gender bias, the people running Silicon Valley at least pay lip service to wanting to do better — but with age discrimination they don't even bother to lie.
hiring startups tech ageism age hubspot gen-y discrimination
Gaeltacht development company defends sale of State seaweed company to Canadian multinational
FFS. Fine Gael government sells off more of our national assets for cheap:
Mr John O'Sullivan, chief executive of Bioatlantis Ltd in Co Kerry called on the Oireachtas environment committee to investigate the sale, or ask the Oireachtas public accounts committee to do so. Mr O'Sullivan said that his company had made a bid of €5.7 million for Arramara, comprising €1.5 million initially and €4.2 million in the post-investment phase, and had been given just 12 days to prepare the bid. He understood that two foreign companies – the Canadian Acadian Seaplants and French company Setalg – had been given over a year to prepare their bids. He said that Acadian's bid was €1.8 million, and the French bid was €2 million, for initial purchase, and that the rating was "changed" when the final bids were in. No details had been released and the lack of transparency was "frightening" in relation to the final sale, he said.
seaweed acadian setalg arramara bioatlantis government ireland selloff gaeltacht unag
-
Comprehensive surveillance appears as seemingly inexpensive because it is a solution that scales thanks to technology: troubleshooting at the press of a button. Directly linked with the aim of saving more and more, just as with the State in general. But classic investigative work, which is proven to work, is expensive and labor intensive. This leads to a failure by the authorities because of a faith in technology that is driven by economics.
tech surveillance techdirt terrorism brussels crypto going-dark
So you're thinking of coming to Dublin...
A really excellent list of stuff to do/see/eat/drink in Ireland, from Colin @ 3FE. top notch recommendations! (also, god I need to get out more)
Nest Reminds Customers That Ownership Isn't What It Used to Be
EFF weigh in on the internet of shit:
Customers likely didn't expect that, 18 months after the last Revolv Hubs were sold, instead of getting more upgrades, the device would be intentionally, permanently, and completely disabled. .... Nest Labs and Google are both subsidiaries of Alphabet, Inc., and bricking the Hub sets a terrible precedent for a company with ambitions to sell self-driving cars, medical devices, and other high-end gadgets that may be essential to a person's livelihood or physical safety.
Primary Online Database: POD now (mostly) not compulsory (for now)
Ever since the introduction of the Primary Online Database of schoolchildren by the Department of Education, the Department and its Minister have been eager to point out that any parent who refused to allow a child's data to be transferred would see that child's education defunded. Well, for all children other than this week's crop of new Junior Infants, that threat has now collapsed. This is despite the Minister and her department having claimed that the drastic threat of defunding was because it simply wasn't possible to give grants without a child's full data being transferred. [...] Oddly, as the prospect of defunding the education of 30% of the nation's children in the run up to an election loomed large, the Department discovered it could, after all, pay for a child's education without all its POD data.
Wired on the new O'Reilly SRE book
"Site Reliability Engineering: How Google Runs Production Systems", by Chris Jones, Betsy Beyer, Niall Richard Murphy, Jennifer Petoff. Go Niall!
google sre niall-murphy ops devops oreilly books toread reviews
#
Google's Nest killing off old devices
Google is making customers' existing devices useless, less than 2 years after the devices were available for sale, with only 2 months warning. This is one of the reasons I won't spend money on the Internet Of Things shitshow. '"Which hardware will Google choose to intentionally brick next?" asks Arlo Gilbert. "If they stop supporting Android will they decide that the day after warranty expires that your phone will go dark? Is your Nexus device safe? What about your Nest fire alarm? What about your Dropcam? What about your Chromecast device?"'
'Devastating' bug pops secure doors at airports, hospitals
"A command injection vulnerability exists in this function due to a lack of any sanitisation on the user-supplied input that is fed to the system() call," Lawshae says.
:facepalm:security iot funny fail linux unix backticks system udp hid vertx edge
Counting with domain specific databases — The Smyte Blog — Medium
whoa, pretty heavily engineered scalable counting system with Kafka, RocksDB and Kubernetes
Is anyone concerned about the future of Nest?
wow, looks like Nest is fucked:
As a Nest engineer, I won't say any numbers that aren't public, but this company is already on deathwatch. Once that happens, most people will quickly have shiny paperweights because it's a constant firefight keeping these systems up. We have $340M in revenue, not profit, against a ~$500M budget. No new products since the purchase, and sales/growth numbers are dire. Our budget deal expires soon, and all the good engineers on my teams have discreetly indicated they are going to flee once their golden handcuffs unlock (many have already left despite sacrificing a lot of money to do so). Tony and his goons demand crazy timelines so much that "crunch time" has basically lost meaning. Just when your labor bears fruit, they swoop in, 180 the specs you just delivered on, then have the gall to call your team "incompetent" for not reading their mind and delivering on these brand-new specs. I waste most of my time in pointless meetings, or defending my teams so they don't flip their desks and walk out. People fall asleep in corners and cry in the bathrooms, health and marriages are suffering. Already the churn is insane, close to half the company if not more. Skilled engineers can tell the environment is toxic, so we're filling vacancies with mostly sub-par talent.
#
-
Publish JVM and Android libraries direct from github -- it'll build and package a lib on the fly, caching them via CDN
build github java maven gradle dependencies packaging libraries
Illicit trade in prescription drugs a growing problem for Dublin's north inner city
ughh. The latest scourge is Zopiclone, "zimmos", which are being dealt openly due to a bureaucratic loophole in enforcement.
A programming language for E. coli
Mind = blown.
MIT biological engineers have created a programming language that allows them to rapidly design complex, DNA-encoded circuits that give new functions to living cells. Using this language, anyone can write a program for the function they want, such as detecting and responding to certain environmental conditions. They can then generate a DNA sequence that will achieve it. "It is literally a programming language for bacteria," says Christopher Voigt, an MIT professor of biological engineering. "You use a text-based language, just like you're programming a computer. Then you take that text and you compile it and it turns it into a DNA sequence that you put into the cell, and the circuit runs inside the cell."
dna mit e-coli bacteria verilog programming coding biohacking science
GitHub now supports "squash on merge"
yay. On the other hand -- http://www.thecaucus.net/#/content/caucus/tech_blog/516 is a good explanation of why not to adopt it. Pity GitHub haven't made it a per-review option...
-
Dynamic tracing tools for Linux, a la dtrace, ktrace, etc. Built using BPF, using kernel features in the 4.x kernel series, requiring at least version 4.1 of the kernel
US government commits to publish publicly financed software under Free Software licenses
Wow, this is significant:
At the end of last week, the White House published a draft for a Source Code Policy. The policy requires every public agency to publish their custom-build software as Free Software for other public agencies as well as the general public to use, study, share and improve the software. At the Free Software Foundation Europe (FSFE) we believe that the European Union, and European member states should implement similar policies. Therefore we are interested in your feedback to the US draft.
government open-source coding licenses fsf free-software source-code us-politics usa
-
'used most commonly when coding integers whose upper-bound cannot be determined beforehand.'
data-structures algorithms elias-gamma-coding encoding coding numbers integers
A Decade Of Container Control At Google
The big thing that can be gleaned from the latest paper out of Google on its container controllers is that the shift from bare metal to containers is a profound one – something that may not be obvious to everyone seeking containers as a better way – and we think cheaper way – of doing server virtualization and driving up server utilization higher. Everything becomes application-centric rather than machine-centric, which is the nirvana that IT shops have been searching for. The workload schedulers, cluster managers, and container controllers work together to get the right capacity to the application when it needs it, whether it is a latency-sensitive job or a batch job that has some slack in it, and all that the site recovery engineers and developers care about is how the application is performing and they can easily see that because all of the APIs and metrics coming out of them collect data at the application level, not on a per-machine basis. To do this means adopting containers, period. There is no bare metal at Google, and let that be a lesson to HPC shops or other hyperscalers or cloud builders that think they need to run in bare metal mode.
How wet is a cycling commute in Ireland?
It turns out that you'll get wet 3 times more often if you're a Galway cyclist when compared to a Dubliner. Dublin is Ireland's driest cycling city.
Some good data and visualization on this extremely important issuerain rainfall-radar ireland climate weather dublin galway cycling
#
CNBC "How Secure Is Your Password" tester form is a spectacular security shitshow
It not only runs over HTTP, it also sends your password to a bunch of third-party ad trackers. omgwtfbbqfail
fail wtf funny cnbc clowns inept security passwords http ad-trackers
Inside the GPO in 1916: Desmond FitzGerald's eyewitness account
'First published 50 years ago, this first-hand account by the father of the future taoiseach Garrett FitzGerald created a storm by claiming that the rebel leaders sympathetically discussed the likelihood of the Germans putting a prince of their own on the Irish throne.' This is amazing -- the dispair and confusion is palpable. This is the first realistic-sounding account of what went on inside the GPO during the Easter Rising I've read, and the "German prince" gambit is pretty astonishing too.
easter-rising 1916 history gpo germany ireland desmond-fitzgerald royalty
SmartThings Presence Detection using DD-WRT Router Script
neat trick -- using DD-WRT's arp tables and a cron job to detect presence of wifi devices (e.g. phones) and take action based on that. By using https://ifttt.com/maker , it should be feasible to wire up any IFTTT action when a device connects to my home wifi...
-
quite a reasonable position, I think
#
Clampers have to clock off as hour change crashes system
DST strikes again:
The failure of the ParkbyText system, operated by National Controlled Parking Systems (NCPS), was described by one employee contacted by a midlands motorist unable to pay for his parking at a train station as a "Y2K moment". The system failure caused early morning panic for thousands of drivers who tried unsuccessfully to use text messages or an app to pay for their parking ahead of returning to work after the bank holiday weekend.
Impact was that they had to stop enforcement until the day passed, I think.firehol/netdata: Real-time performance monitoring, done right!
Lovely Bootstrap-based UI, easy to install (via Mark Kenny)
via:markkenny linux monitoring ops netdata sysstat metrics graphing ui
the murky origins of Truecrypt
Allegedly, Truecrypt, the disk encryption tool, was written by a multi-millionaire international arms dealer and criminal kingpin. Hell of an assertion, this!
#
Mass surveillance silences minority opinions, according to study - The Washington Post
This is excellent research, spot on.
Elizabeth Stoycheff, lead researcher of the study and assistant professor at Wayne State University, is disturbed by her findings. "So many people I've talked with say they don't care about online surveillance because they don't break any laws and don't have anything to hide. And I find these rationales deeply troubling," she said. She said that participants who shared the "nothing to hide" belief, those who tended to support mass surveillance as necessary for national security, were the most likely to silence their minority opinions. "The fact that the 'nothing to hide' individuals experience a significant chilling effect speaks to how online privacy is much bigger than the mere lawfulness of one's actions. It's about a fundamental human right to have control over one's self-presentation and image, in private, and now, in search histories and metadata," she said.
culture privacy psychology surveillance mass-surveillance via:snowden nothing-to-hide spiral-of-silence fear
-
pretty sure I had this bookmarked previously, but this is the current URL -- SSL/TLS quality report
Observability at Twitter: technical overview, part II
Interesting to me mainly for this tidbit which makes my own prejudices:
"Pull" vs "push" in metrics collection: At the time of our previous blog post, all our metrics were collected by "pulling" from our collection agents. We discovered two main issues: * There is no easy way to differentiate service failures from collection agent failures. Service response time out and missed collection request are both manifested as empty time series. * There is a lack of service quality insulation in our collection pipeline. It is very difficult to set an optimal collection time out for various services. A long collection time from one single service can cause a delay for other services that share the same collection agent. In light of these issues, we switched our collection model from "pull" to "push" and increased our service isolation. Our collection agent on each host only collects metrics from services running on that specific host. Additionally, each collection agent sends separate collection status tracking metrics in addition to the metrics emitted by the services. We have seen a significant improvement in collection reliability with these changes. However, as we moved to self service push model, it becomes harder to project the request growth. In order to solve this problem, we plan to implement service quota to address unpredictable/unbounded growth.
pull push metrics tcp stacks monitoring agents twitter fault-tolerance
These unlucky people have names that break computers
Pat McKenzie's name is too long to fit in Japanese database schemas; Janice Keihanaikukauakahihulihe'ekahaunaele's name was too long for US schemas; and Jennifer Null suffers from the obvious problem
How we implemented the video player in Mail.Ru Cloud
We've recently added video streaming service to Mail.Ru Cloud. Development started with contemplating the new feature as an all-purpose "Swiss Army knife" that would both play files of any format and work on any device with the Cloud available. Video content uploaded to the Cloud mostly falls into one of the two categories: "movies/series" and "users' videos". The latter are the videos that users shoot with their phones and cameras, and these videos are most versatile in terms of formats and codecs. For many reasons, it is often a problem to watch these videos on other end-user devices without prior normalization: a required codec is missing, or the file size is too big to download, or whatever.
Mainly around using HLS (HTTP Live Streaming).A shot that rang round the world
The international impact of the Easter Rising has rarely been acknowledged. This rebellion did not only rattle British rule in Ireland — it inspired radical movements in Britain itself and across the globe, and it shook colonial rulers and states worldwide.
-
nice java impl of this efficient data structure, broken out from Project Reactor
scalability java timers hashed-wheel-timers algorithms data-structures
#
SNES Code Injection -- Flappy Bird in Super Mario World
hand-injecting an entirely different game into Super Mario World on the SNES by exploiting buffer overflows BY HAND. this is legendary behaviour
games hacks exploits buffer-overflow snes code-injection amazing flappy-bird seth-bling video youtube
#
-
built-in support for CI/CD deployment pipelines, driven from a checked-in DSL file. great stuff, very glad to see them going this direction. (via Eric)
via:eric jenkins ci cd deployment pipelines testing automation build
Hey Microsoft, the Internet Made My Bot Racist, Too
All machine learning algorithms strive to exaggerate and perpetuate the past. That is, after all, what they are learning from. The fundamental assumption of every machine learning algorithm is that the past is correct, and anything coming in the future will be, and should be, like the past. This is a fine assumption to make when you are Netflix trying to predict what movie you'll like, but is immoral when applied to many other situations. For bots like mine and Microsoft's, built for entertainment purposes, it can lead to embarrassment. But AI has started to be used in much more meaningful ways: predictive policing in Chicago, for example, has already led to widespread accusations of racial profiling. This isn't a little problem. This is a huge problem, and it demands a lot more attention then it's getting now, particularly in the community of scientists and engineers who design and apply these algorithms. It's one thing to get cursed out by an AI, but wholly another when one puts you in jail, denies you a mortgage, or decides to audit you.
#
Tahoe LAFS accidentally lose Bitcoin wallet with loads of donations in it, get it back
But ECDSA private keys don't trigger the same protective instincts that we'd apply to, say, a bar of gold. One sequence of 256 random bits looks just as worthless as any other. And the cold hard unforgeability of these keys means we can't rely upon other humans to get our money back when we lose them. Plus, we have no experience at all with things that grow in value by four orders of magnitude, without any attention, in just three years. So we have a cryptocurrency-tool UX task in front of us: to avoid mistakes like the one we made, we must to either move these digital assets into solid-feeling physical containers, or retrain our perceptions to attach value to the key strings themselves.
backups cryptography bitcoin cryptocurrency ecdsa private-keys ux money
Visual Representation of SQL Joins
useful bookmark to have (via Nelson)
Interesting Lottery Terminal Hack - Schneier on Security
Neat manual timing attack.
An investigator for the Connecticut Lottery determined that terminal operators could slow down their lottery machines by requesting a number of database reports or by entering several requests for lottery game tickets. While those reports were being processed, the operator could enter sales for 5 Card Cash tickets. Before the tickets would print, however, the operator could see on a screen if the tickets were instant winners. If tickets were not winners, the operator could cancel the sale before the tickets printed.
#
-
A microservice saviour appears! In order to prevent such a terrible tragedy from occurring ever again during our lifetimes, `left-pad.io` has been created to provide all the functionality of `left-pad` AND the overhead of a TLS handshake and an HTTP request. Less code is better code, leave the heavy lifting to `left-pad.io`, The String Experts™.
humor javascript jokes npm packages left-pad strings microservices http
Life360 testimonial for Prometheus
Now this is a BIG thumbs up:
'Prometheus has been known to us for a while, and we have been tracking it and reading about the active development, and at a point (a few months back) we decided to start evaluating it for production use. The PoC results were incredible. The monitoring coverage of MySQL was amazing, and we also loved the JMX monitoring for Cassandra, which had been sorely lacking in the past.'
metrics monitoring time-series prometheus testimonials life360 cassandra jmx mysql
Microsoft terminates its Tay AI chatbot after she turns into a Nazi
'if you tell her "repeat after me" she will parrot back whatever you say, allowing you to put words into her mouth.'
what. the. fuck. Microsoft.
#
Javascript libraries and tools should bundle their code
If you have a million npm dependencies, distribute them in the dist package; aka. omnibus packages for JS
packaging omnibus npm webpack rollup dependencies coding javascript
Ruby in Production: Lessons Learned — Medium
Based on the pain we've had trying to bring our Rails services up to the quality levels required, this looks pretty accurate in many respects. I'd augment this advice by saying: avoid RVM; use Docker.
Charity Majors - AWS networking, VPC, environments and you
'VPC is the future and it is awesome, and unless you have some VERY SPECIFIC AND CONVINCING reasons to do otherwise, you should be spinning up a VPC per environment with orchestration and prob doing it from CI on every code commit, almost like it's just like, you know, code.'
Angola's Wikipedia Pirates Are Exposing the Problems With Digital Colonialism | Motherboard
Wikimedia and Facebook have given Angolans free access to their websites, but not to the rest of the internet. So, naturally, Angolans have started hiding pirated movies and music in Wikipedia articles and linking to them on closed Facebook groups, creating a totally free and clandestine file sharing network in a country where mobile internet data is extremely expensive.
#
-
This is a great point, and one I'll be quoting:
Any design that is hard to test is crap. Pure crap. Why? Because if it's hard to test, you aren't going to test it well enough. And if you don't test it well enough, it's not going to work when you need it to work. And if it doesn't work when you need it to work the design is crap.
Amen!
#
Modern Irish genome closely matches pre-Celt DNA, not Celtic
Radiocarbon dating shows that the bones discovered at McCuaig's go back to about 2000 B.C. That makes them hundreds of years older than the oldest artifacts generally considered to be Celtic — relics unearthed from Celt homelands of continental Europe, most notably around Switzerland, Austria and Germany. For a group of scholars who in recent years have alleged that the Celts, beginning from the middle of Europe, may never have reached Ireland, the arrival of the DNA evidence provides the biological certitude that the science has sometimes brought to criminal trials. "With the genetic evidence, the old model [of Celtic colonisation of Ireland] is completely shot," John Koch, a linguist at the Center for Advanced Welsh and Celtic Studies at the University of Wales.
celts ireland history dna genetics genome carbon-dating bronze-age europe colonisation
#
GCM XMPP delivery receipt not always received - Google Groups
Good to know:
'GCM delivery receipts don't have an SLA at this time. Having your connection open longer will increase the odds that delivery receipts will arrive. 10 seconds seems a bit short. I'm glad it works. I would recommend longer like 10 min or an hour. The real design of this system is for persistent connections, hence connections that setup and tear down frequently will have difficulty receiving delivery receipts.'
#
The disturbingly simple way dozens of celebrities had their nude photos stolen
Basic phishing: 'Collins hacked over 100 people by sending emails that looked like they came from Apple and Google, such as "e-mail.protection318@icloud.com," "noreply_helpdesk0118@outlook.com," and "secure.helpdesk0019@gmail.com." According to the government, Collins asked for his victims' iCloud or Gmail usernames and passwords and "because of the victims' belief that the email had come from their [Internet Service Providers], numerous victims responded by giving [them]."'
RFC 7754 - Technical Considerations for Internet Service Blocking and Filtering
The Internet is structured to be an open communications medium. This openness is one of the key underpinnings of Internet innovation, but it can also allow communications that may be viewed as undesirable by certain parties. Thus, as the Internet has grown, so have mechanisms to limit the extent and impact of abusive or objectionable communications. Recently, there has been an increasing emphasis on "blocking" and "filtering", the active prevention of such communications. This document examines several technical approaches to Internet blocking and filtering in terms of their alignment with the overall Internet architecture. When it is possible to do so, the approach to blocking and filtering that is most coherent with the Internet architecture is to inform endpoints about potentially undesirable services, so that the communicants can avoid engaging in abusive or objectionable communications. We observe that certain filtering and blocking approaches can cause unintended consequences to third parties, and we discuss the limits of efficacy of various approaches.
(via Tony Finch)via:fanf blocking censorship filtering internet rfcs rfc isps
-
'There are three easy to make mistakes in go. I present them here in the way they are often found in the wild, not in the way that is easiest to understand. All three of these mistakes have been made in Kubernetes code, getting past code review at least once each that I know of.'
Health of purebred vs mixed breed dogs: the actual data - The Institute of Canine Biology
This study found that purebred dogs have a significantly greater risk of developing many of the hereditary disorders examined in this study. No, mixed breed dogs are not ALWAYS healthier than purebreds; and also, purebreds are not "as healthy" as mixed breed dogs. The results of this study will surprise nobody who understands the basics of Mendelian inheritance. Breeding related animals increases the expression of genetic disorders caused by recessive mutations, and it also increases the probability of producing offspring that will inherit the assortment of genes responsible for a polygenic disorder.
In conclusion, go mutts.dogs breeding genetics hereditary-disorders science inheritance recessive-mutation data
#
DeepMind founder Demis Hassabis on how AI will shape the future | The Verge
Good interview with Demis Hassabis on DeepMind, AlphaGo and AI:
I'd like to see AI-assisted science where you have effectively AI research assistants that do a lot of the drudgery work and surface interesting articles, find structure in vast amounts of data, and then surface that to the human experts and scientists who can make quicker breakthroughs. I was giving a talk at CERN a few months ago; obviously they create more data than pretty much anyone on the planet, and for all we know there could be new particles sitting on their massive hard drives somewhere and no-one's got around to analyzing that because there's just so much data. So I think it'd be cool if one day an AI was involved in finding a new particle.
ai deepmind google alphago demis-hassabis cern future machine-learning
-
Good post on Dublin City Council's atrociously revisionist 1916-commemoration banner, celebrating Henry Grattan, Daniel O'Connell, Charles Stewart Parnell and John Redmond:
The banner is not showing parliamentary nationalists who might be included in a history of 1916 (Redmond might have been joined by John Dillon and Tom Kettle, for instance), but displaying the parliamentarian tradition in Irish political history. The people chosen all worked for change via political means, whether obtaining an independent Irish parliament from 1782-1801 (Grattan), working for Catholic Emancipation (Grattan and O'Connell), land reform (Parnell), or trying to repeal the Act of Union and obtain Home Rule (O'Connell, Parnell, Redmond). All were MPs in Westminster at some point. None openly espoused physical force. None aimed at establishing an independent Irish Republic. Putting the history of parliamentarianism on a banner labelled 1916 suggests that 1916 was in the parliamentarian tradition. That suggestion is very far from the truth.
parliamentarianism 1916 history revisionism dcc dublin politics
-
a static type checker for Javascript, from Facebook
#
Wait and lock free alternatives to LongAdder and AtomicLong by qwwdfsad
interesting new lock-free low-level hacking
longadder doug-lea mechanical-sympathy lock-free performance atomic multithreading java jvm
#
Annie West's walking trail maps
These are really beautiful (and actually quite practical)! Nice one Annie
annie-west maps prints ireland sligo benbulben trails via:broadsheet
#
-
a free, multi-threaded compression utility with support for bzip2 compressed file format. lbzip2 can process standard bz2 files in parallel. It uses POSIX threading model (pthreads), which allows it to take full advantage of symmetric multiprocessing (SMP) systems. It has been proven to scale linearly, even to over one hundred processor cores. lbzip2 is fully compatible with bzip2 – both at file format and command line level. Files created by lbzip2 can be decompressed by all versions of bzip2 and other software supporting bz2 format. lbzip2 can decompress any bz2 files in parallel. All bzip2 command-line options are also accepted by lbzip2. This makes lbzip2 a drop-in replacement for bzip2.
#
Distribution of people's PIN codes, as a heatmap
Excellent use of a heatmap
security datavis pins passwords date-of-birth birthday atms banking
Conversant ConcurrentQueue and Disruptor BlockingQueue
'Disruptor is the highest performing intra-thread transfer mechanism available in Java. Conversant Disruptor is the highest performing implementation of this type of ring buffer queue because it has almost no overhead and it exploits a particularly simple design. Conversant has been using this in production since 2012 and the performance is excellent. The BlockingQueue implementation is very stable, although we continue to tune and improve it. The latest release, 1.2.4, is 100% production ready. Although we have been working on it for a long time, we decided to open source our BlockingQueue this year to contribute something back to the community. ... its a drop in for BlockingQueue, so its a very easy test. Conversant Disruptor will crush ArrayBlockingQueue and LinkedTransferQueue for thread to thread transfers. In our system, we noticed a 10-20% reduction in overall system load and latency when we introduced it.'
disruptor blocking-queues queues queueing data-structures algorithms java conversant concurrency performance
TeleGeography Submarine Cable Map 2015
Gorgeously-illustrated retro map of modern-day submarine cables. Prints available for $150 (via Conor Delaney)
via:conor-delaney data internet maps cables world telegeography mapping retro
-
UK banks are getting press for evading liability and screwing the customer when scams and phishing occur
scams phishing uk banking banks liability terms-and-conditions barclays
-
Nice approach from MongoDB:
we've recently gained momentum on standardizing our [cross-platform test] drivers. Human-readable, machine-testable specs, coded in YAML, prove which code conforms and which does not. These YAML tests are the Cat-Herd's Crook: a tool to guide us all in the same direction.
There's Something Fishy About The Other Nefertiti
The last possibility and reigning theory is that Ms. Badri and Mr. Nelles elusive hacker partners are literally real hackers who stole a copy of the high resolution scan from the Museum's servers. A high resolution scan must exist as a high res 3D printed replica is already available for sale online. Museum officials have dismissed the Other Nefertiti model as "of minor quality", but that's not what we are seeing in this highly detailed scan. Perhaps the file was obtained from someone involved in printing the reproduction, or it was a scan made of the reproduction? Indeed, the common belief in online 3D Printing community chatter is that the Kinect "story" is a fabrication to hide the fact that the model was actually stolen data from a commercial high quality scan. If the artists were behind a server hack, the legal ramifications for them are much more serious than scanning the object, which has few, if any legal precedents.
art history 3d-printing 3d nefertiti heists copyright data kinect
Amaro 101: An Introduction to Italian Amari
some nice-sounding cocktail recipes for these tasty bitters
#
-
Prodigy software patents invoked in suit against GroupOn. Patent troll mode activated :( (via Paul Graham)
ibm patents swpats paul-graham patent-trolls prodigy groupon
Nook DRM promises to kill book collection unless user takes action
yay, DRM. "It is important that you transfer your purchased NOOK Books to ensure access"
March 2016's shocking global warming temperature record
Keep in mind that it took from the dawn of the industrial age until last October to reach the first 1.0 degree Celsius, and we've come as much as an extra 0.4 degrees further in just the last five months. Even accounting for the margin of error associated with these preliminary datasets, that means it's virtually certain that February handily beat the record set just last month for the most anomalously warm month ever recorded. That's stunning.
eek.
#
Protect me, I am the Donnybrook laundry
Mannix Flynn makes a persuasive case to preserve the last remaining Magdalene Laundry still standing:
Memory is something that fights an eternal battle with the passage of time and forgetfulness. Time is a great healer for those who can heal and those who are offered healing. There is no healing here. Time stands still like a festering wound in a well-to-do suburb as somebody attempts to erase a grave and mortal wrong. The McAleese report, the Justice for the Magdalenes, the hundreds of women still alive and their families should know of this place. Should be present here to witness what can only be witnessed by them. So that they can understand what's lost, what cannot be given. What was taken from them for generations.
magdalenes injustice ireland history catholic-church abuse mannix-flynn
#
10 things to avoid in docker containers
decent tips
-
The latest SSL security hole. 'DROWN shows that merely supporting SSLv2 is a threat to modern servers and clients. It allows an attacker to decrypt modern TLS connections between up-to-date clients and servers by sending probes to a server that supports SSLv2 and uses the same private key.'
#
-
Excellent drawing books from Chris Judge and his brother Andrew. gotta get this: 'WELCOME TO DOODLETOWN, the home of the Doodles. It is a very nice town, except for one SMALL problem. Everything is half drawn with bits and pieces missing! The Doodles are going to need YOUR help. So grab a pen or a pencil and help finish the adventure!'
The IPv6 Numeric IP Format is a Serious Usability Problem
strongly agreed!
#
Proportional Representation in Ireland: How it Works
Excellent explanation of PR-STV and the Irish voting system. Don't be a Plumper! (via John O'Shea)
Microsoft warns of risks to Irish operation in US search warrant case
"Our concern is that if we lose the case more countries across Europe or elsewhere are going to be concerned about having their data in Ireland, " Mr Smith said, after testifying before the House judiciary committee. Asked what would happen to its Irish unit if the company loses the case or doesn't convince Congress to pass updated legislation governing cross-border data held by American companies, the Microsoft executive said: "We'll certainly face a new set of risks that we don't face today." He added that the issue could be resolved by an executive order by the White House or through international negotiations between the Irish Government or the European Union and the US.
How To Implement Secure Bitcoin Vaults
At the Bitcoin workshop in Barbados, Malte Möser will present our solution to the Bitcoin private key management problem. Specifically, our paper describes a way to create vaults, special accounts whose keys can be neutralized if they fall into the hands of attackers. Vaults are Bitcoin's decentralized version of you calling your bank to report a stolen credit card -- it renders the attacker's transactions null and void. And here's the interesting part: in so doing, vaults demotivate key theft in the first place. An attacker who knows that he will not be able to get away with theft is less likely to attack in the first place, compared to current Bitcoin attackers who are guaranteed that their hacking efforts will be handsomely rewarded.
#
Maglev: A Fast and Reliable Software Network Load Balancer
Maglev is Google's network load balancer. It is a large distributed software system that runs on commodity Linux servers. Unlike traditional hardware network load balancers, it does not require a specialized physical rack deployment, and its capacity can be easily adjusted by adding or removing servers. Network routers distribute packets evenly to the Maglev machines via Equal Cost Multipath (ECMP); each Maglev machine then matches the packets to their corresponding services and spreads them evenly to the service endpoints. To accommodate high and ever-increasing traffic, Maglev is specifically optimized for packet processing performance. A single Maglev machine is able to saturate a 10Gbps link with small packets. Maglev is also equipped with consistent hashing and connection tracking features, to minimize the negative impact of unexpected faults and failures on connection-oriented protocols. Maglev has been serving Google's traffic since 2008. It has sustained the rapid global growth of Google services, and it also provides network load balancing for Google Cloud Platform.
Something we argued for quite a lot in Amazon, back in the day....google paper scale ecmp load-balancing via:conall maglev lbs
-
BrewDog releases their beer recipes for free. so cool! 'So here it is. The keys to our kingdom. Every single BrewDog recipe, ever. So copy them, tear them to pieces, bastardise them, adapt them, but most of all, enjoy them. They are well travelled but with plenty of miles still left on the clock. Just remember to share your brews, and share your results. Sharing is caring.'
National Children's Science Centre due to open in 2018
Good for science fans, not so hot for real tennis fans.
The former real tennis court building close to the concert hall's north wing would be used for temporary and visiting exhibitors, with a tunnel connecting it to the science centre. The National Children's Science Centre is due to open in late 2018 and will also be known as the Exploration Station, said Dr Danny O'Hare, founding president of Dublin City University and chairman of the Exploration Station board since 2006.
#
Troy Hunt: Controlling vehicle features of Nissan LEAFs across the globe via vulnerable APIs
holy crap. Nissan expose a public API authenticated _solely_ using the car's VIN -- which is more or less public info; the API allows turning on/off AC, grabbing driving history, etc.
#
You could pay €40k in fund fees - even if you lose money - Independent.ie
High PRSA charges make them a pretty crappy retirement policy
prsa savings retirement money investment fees irish-life pensions
#
Neutrino Software Load Balancer
eBay's software LB, supporting URL matching, comparable to haproxy, built using Netty and Scala. Used in their QA infrastructure it seems
netty scala ebay load-balancing load-balancers url http architecture
This is Why People Fear the 'Internet of Things'
Ugh. This is a security nightmare. Nice work Foscam...
Imagine buying an internet-enabled surveillance camera, network attached storage device, or home automation gizmo, only to find that it secretly and constantly phones home to a vast peer-to-peer (P2P) network run by the Chinese manufacturer of the hardware. Now imagine that the geek gear you bought doesn't actually let you block this P2P communication without some serious networking expertise or hardware surgery that few users would attempt. This is the nightmare "Internet of Things" (IoT) scenario for any system administrator: The IP cameras that you bought to secure your physical space suddenly turn into a vast cloud network designed to share your pictures and videos far and wide. The best part? It's all plug-and-play, no configuration necessary!
#
CharybdeFS: a new fault-injecting filesystem for software testing
a FUSE-based filesystem from ScyllaDB to test filesystem-related failure scenarios. great idea
fuse software testing scylladb filesystems disk charybdefs fault-injection tests
#
The NSA's SKYNET program may be killing thousands of innocent people
Death by Random Forest: this project is a horrible misapplication of machine learning. Truly appalling, when a false positive means death:
The NSA evaluates the SKYNET program using a subset of 100,000 randomly selected people (identified by their MSIDN/MSI pairs of their mobile phones), and a a known group of seven terrorists. The NSA then trained the learning algorithm by feeding it six of the terrorists and tasking SKYNET to find the seventh. This data provides the percentages for false positives in the slide above. "First, there are very few 'known terrorists' to use to train and test the model," Ball said. "If they are using the same records to train the model as they are using to test the model, their assessment of the fit is completely bullshit. The usual practice is to hold some of the data out of the training process so that the test includes records the model has never seen before. Without this step, their classification fit assessment is ridiculously optimistic." The reason is that the 100,000 citizens were selected at random, while the seven terrorists are from a known cluster. Under the random selection of a tiny subset of less than 0.1 percent of the total population, the density of the social graph of the citizens is massively reduced, while the "terrorist" cluster remains strongly interconnected. Scientifically-sound statistical analysis would have required the NSA to mix the terrorists into the population set before random selection of a subset—but this is not practical due to their tiny number. This may sound like a mere academic problem, but, Ball said, is in fact highly damaging to the quality of the results, and thus ultimately to the accuracy of the classification and assassination of people as "terrorists." A quality evaluation is especially important in this case, as the random forest method is known to overfit its training sets, producing results that are overly optimistic. The NSA's analysis thus does not provide a good indicator of the quality of the method.
terrorism surveillance nsa security ai machine-learning random-forests horror false-positives classification statistics
#
Lasers reveal 'lost' Roman roads
UK open data success story, via Tony Finch:
This LIDAR data bonanza has proved particularly helpful to archaeologists seeking to map Roman roads that have been 'lost', some for thousands of years. Their discoveries are giving clues to a neglected chapter in the history of Roman Britain: the roads built to help Rome's legions conquer and control northern England.
uk government lidar open-data data roman history mapping geodata
#
-
Also known as "Graduate Student Descent", a common approach to hyperparameter tuning in machine learning -- ie. get an intern to sit there tweaking parameters until they find something approximating optimal performance
optimization funny terms terminology graduate-student-descent hyperparameters semisupervised-intern-descent tuning interns
-
Valentine's Day cards for you and yours, from one of cinema's true visionaries. How do you communicate the depth of your desire? Say it with Cronenberg Valentines.
david-cronenberg horror gross naked-lunch movies valentines-day funny
-
Let's see how long this lasts:
Today Sauce Labs is proud to open-source isign. isign can take an iOS app that was authorized to run only on one developer's phone, and transform it so it can run on another developer's phone. This is not a hack around Apple's security. We figured out how Apple's code signing works and re-implemented it in Python. So now you can use our isign utility anywhere – even on Linux!
#
-
'Indonesia's government has demanded that instant messaging apps remove stickers featuring same-sex couples, in the latest high-profile attempt to discourage visible homosexuality in the socially conservative country.' (via fuzzix)
#
-
Apple outlaws third-party repairs with vague TouchID-related justifications:
Freelance photographer and self-confessed Apple addict Antonio Olmos says this happened to his phone a few weeks ago after he upgraded his software. Olmos had previously had his handset repaired while on an assignment for the Guardian in Macedonia. "I was in the Balkans covering the refugee crisis in September when I dropped my phone. Because I desperately needed it for work I got it fixed at a local shop, as there are no Apple stores in Macedonia. They repaired the screen and home button, and it worked perfectly." He says he thought no more about it, until he was sent the standard notification by Apple inviting him to install the latest software. He accepted the upgrade, but within seconds the phone was displaying "error 53" and was, in effect, dead.
Now that is scummy.apple error-53 ios9 ios phones smartphones touchid via:boingboing
-
good roundup of real-world clock skew links
clocks clock-skew ntp realtime time bugs distcomp reliability skew
#
-
A critique of the "Redlock" locking algorithm from Redis by Martin Kleppman. antirez responds here: http://antirez.com/news/101
distributed locking redis algorithms coding distcomp redlock martin-kleppman zookeeper
Submitting User Applications with spark-submit - AWS Big Data Blog
looks reasonably usable, although EMR's crappy UI is still an issue
-
Awesome post from Dan Luu with data from Google:
The cause [of some mystery widespread 250ms hangs] was kernel throttling of the CPU for processes that went beyond their usage quota. To enforce the quota, the kernel puts all of the relevant threads to sleep until the next multiple of a quarter second. When the quarter-second hand of the clock rolls around, it wakes up all the threads, and if those threads are still using too much CPU, the threads get put back to sleep for another quarter second. The phase change out of this mode happens when, by happenstance, there aren't too many requests in a quarter second interval and the kernel stops throttling the threads. After finding the cause, an engineer found that this was happening on 25% of disk servers at Google, for an average of half an hour a day, with periods of high latency as long as 23 hours. This had been happening for three years. Dick Sites says that fixing this bug paid for his salary for a decade. This is another bug where traditional sampling profilers would have had a hard time. The key insight was that the slowdowns were correlated and machine wide, which isn't something you can see in a profile.
debugging performance visualization instrumentation metrics dan-luu latency google dick-sites linux scheduler throttling kernel hangs
#
View & diagnose Google Cloud Messaging (GCM) statistics
Looks like GCM now offers a way to determine if a message got delivered, via the GCM diagnostics console
OnePlus 2 and OnePlus X damaging Deutsche Telekom SIM cards
I can confirm, there is a help forum from the "deutsche telekom", they say there is a feature called MEC (it's mainly for setting phone parameters to match their network), active on all their SIM cards, which is not correctly handled by any of the OnePlus Devices (one, two, x) so it writes constantly to flash memory, killing it arround 100.000 writes which is 3-6 weeks.
(via Mike Walsh on the Irish tech slack)via:itc oneplus phones sim-cards mec deutsche-telekom bugs flash
#
Scala client composition with Traits vs implementing an abstract class - Stack Overflow
good Scala coding advice from Travis Brown
#
The science behind "don't drink when pregnant" is rubbish
As the economist Emily Oster pointed out in her 2013 book Expecting Better, there is also no "proven safe" level of Tylenol or caffeine, and yet both are fine in moderation during pregnancy. Oster pored through reams of research on alcohol and pregnancy for her book and concluded that there is simply no scientific evidence that light drinking during pregnancy impacts a baby's health. (In one frequently cited 2001 study that suggested light drinking in pregnancy increases the chances of a child displaying aggressive behaviors, the drinkers were also significantly likelier to have taken cocaine during pregnancy.)
My wife also followed the paper trail on this issue in the past. In the papers from which these recommendations were derived, the level of drinking at which any effects were observed in babies was when women consumed at least *9 units every day* for the entire pregnancy. That's an entire bottle of wine, daily!booze alcohol science facts papers medicine emily-oster babies pregnancy pre-pregnant research
-
'"Spam emails are a large proportion of emails seen in SIGINT [signals intelligence]," reads part of a dense document from the Snowden archive, published by Boing Boing on Tuesday. "GCHQ would like to reduce the impact of spam emails on data storage, processing and analysis."' (circa 2011). Steganography, anyone? (via Tony Finch)
spam anti-spam gchq funny boing-boing sigint snowden surveillance
ECHR: Websites not liable for readers' comments
'Lawyers for [a Hungarian news] site said the comments concerned had been taken down as soon as they were flagged. They said making their clients liable for everything readers posted "would have serious adverse repercussions for freedom of expression and democratic openness in the age of Internet". The ECHR agreed. "Although offensive and vulgar, the incriminated comments did not constitute clearly unlawful speech; and they certainly did not amount to hate speech or incitement to violence," the judges wrote.'
research!rsc: Zip Files All The Way Down
quine.zip, quine.gz, and quine.tar.gz. Here's what happens when you mail it through bad AV software: https://twitter.com/FioraAeterna/status/694655296707297281
The Nuclear Missile Sites of Los Angeles
Great article by Geoff "bldgblog" Manaugh on the ruins of the Nike air-to-air missile emplacements dotted around California. I had absolutely no idea that these -- the 1958-era Nike-Hercules missiles, at least -- carried 30-kiloton nuclear warheads, intended to be detonated at 50,000 feet *above* the cities they were defending, in order to destroy in-flight bomber formations. Nuclear war was truly bananas.
war history la sf california nike-missiles missiles nuclear-war nike-hercules cold-war 1950s
#
Exclusive: Snowden intelligence docs reveal UK spooks' malware checklist / Boing Boing
This is an excellent essay from Cory Doctorow on mass surveillance in the post-Snowden era, and the difference between HUMINT and SIGINT. So much good stuff, including this (new to me) cite for, "Goodhart's law", on secrecy as it affects adversarial classification:
The problem with this is that once you accept this framing, and note the happy coincidence that your paymasters just happen to have found a way to spy on everyone, the conclusion is obvious: just mine all of the data, from everyone to everyone, and use an algorithm to figure out who's guilty. The bad guys have a Modus Operandi, as anyone who's watched a cop show knows. Find the MO, turn it into a data fingerprint, and you can just sort the firehose's output into "terrorist-ish" and "unterrorist-ish." Once you accept this premise, then it's equally obvious that the whole methodology has to be kept from scrutiny. If you're depending on three "tells" as indicators of terrorist planning, the terrorists will figure out how to plan their attacks without doing those three things. This even has a name: Goodhart's law. "When a measure becomes a target, it ceases to be a good measure." Google started out by gauging a web page's importance by counting the number of links they could find to it. This worked well before they told people what they were doing. Once getting a page ranked by Google became important, unscrupulous people set up dummy sites ("link-farms") with lots of links pointing at their pages.
adversarial-classification classification surveillance nsa gchq cory-doctorow privacy snooping goodharts-law google anti-spam filtering spying snowden
#
Phone robot keeps annoying telemarketers talking for as long as possible
'Anderson encourages his readers to forward telemarketers to the robot, and is happy to send them recordings of the ensuing conversations. His instructions are below if you'd like to give it a shot.'
Why is Safe Harbour II such a challenge? - EDRi
The only possible deal that is immediately available is where the European Commission agrees a politically expeditious but legally untenable deal, creating a time bomb rather than a durable deal, to the benefit of no one. In absence of reforms before an agreement, individuals' fundamental rights would remain under threat.
edri law eu ec ecj surveillance snooping us-politics safe-harbor
-
interactive menu selection for the UNIX command line
-
It seems git's default behavior in many situations is -- despite communicating objectID by content-addressable hashes which should be sufficient to assure some integrity -- it may not actually bother to *check* them. Yes, even when receiving objects from other repos. So, enabling these configuration parameters may "slow down" your git operations. The return is actually noticing if someone ships you a bogus object. Everyone should enable these.
git security integrity error-checking dvcs version-control coding
#
-
Good explanation and scipy code for the birthday paradox and hash collisions
hashing hashes collisions birthday-problem birthday-paradox coding probability statistics
iPhone, iPad, Mac Buyer's Guide: Know When to Buy
sync up with the Apple product cycle when you're buying new hardware
hardware devices apple shopping mac ios iphone ipad releases schedule gadgets
#
Seesaw: scalable and robust load balancing from Google
After evaluating a number of platforms, including existing open source projects, we were unable to find one that met all of our needs and decided to set about developing a robust and scalable load balancing platform. The requirements were not exactly complex - we needed the ability to handle traffic for unicast and anycast VIPs, perform load balancing with NAT and DSR (also known as DR), and perform adequate health checks against the backends. Above all we wanted a platform that allowed for ease of management, including automated deployment of configuration changes. One of the two existing platforms was built upon Linux LVS, which provided the necessary load balancing at the network level. This was known to work successfully and we opted to retain this for the new platform. Several design decisions were made early on in the project — the first of these was to use the Go programming language, since it provided an incredibly powerful way to implement concurrency (goroutines and channels), along with easy interprocess communication (net/rpc). The second was to implement a modular multi-process architecture. The third was to simply abort and terminate a process if we ended up in an unknown state, which would ideally allow for failover and/or self-recovery.
seesaw load-balancers google load-balancing vips anycast nat lbs go ops networking
#
"What the hell have you built"
cut out and keep PNG for many occasions! "Why is Redis talking to MongoDB?"
Schema evolution in Avro, Protocol Buffers and Thrift
Good description of this key feature of decent serialization formats
avro thrift protobuf schemas serialization coding interop compatibility
ECB forcing Ireland to pay the bondholders was like a hostage situation | David McWilliams
At the time, many of us citizens thought the State was being craven in the face of the EU but it is now clear that Trichet's ECB was prepared to let the Irish banks go to the wall, prompting a new bank run in 2010. This is like a hostage situation. The ECB was saying to the Irish government: you managed in September 2008 to prevent a bank run with the guarantee (which should always have been temporary and conditional) but now we are going to threaten you with another bank run – because we are still funding your banks and you must pay all the bondholders and add the cost to the national debt of the country. So the implicit threat was: "We will close the banks, cause a bank run and you will be left to pick up the pieces politically, socially and economically."
banking ireland politics ecb eu bondholders jean-claude-trichet economics
Three lessons from running Kubernetes in production
Wow, the deployment thing is pretty hacky
Apollo 11 Mission on Technical Debt — Medium
'# TEMPORARY, I HOPE HOPE HOPE'
hacks technical-debt backlog prioritisation project-management apollo space history
Pinboard: bookmarks for peakscale tagged 'postmortem'
Bookmarking so I can follow my own link from https://pinboard.in/u:jmason/t:post-mortems/
#
Ireland's first dedicated poutine place opened in Dublin today and it's delish
SOUND THE POUTINE KLAXON
-
Dropwizard for Go, basically:
a distributed programming toolkit for building microservices in large organizations. We solve common problems in distributed systems, so you can focus on your business logic.
microservices go golang http libraries open-source rpc circuit-breakers
#
Meteor | What are the full list of short-codes for voicemail/diverts?
bookmarking for future use
In Phibsboro, a New Deli For a Changing Neighbourhood
"Bang Bang", new fancy deli on Leinster Road North
Tara Pilgrimage 2006 - Indymedia Ireland
OMG, this is hilarious. High drama among the arch-druids (via Lisa Carey)
#
Tim O'Reilly vs Paul Graham: fight!
'In his essay on Income Inequality, Paul Graham credited me for pre-publication feedback. Because he didn't do much with my comments, I thought I'd publish them here.' ... 'Mostly, I think you are picking a fight with people who would mostly agree with you, and ignoring the real arguments about what inequality means and why it matters.'
inequality silicon-valley tech paul-graham tim-oreilly piketty politics economics wealth startups history work stock-options
Fairytales much older than previously thought, say researchers
Analysis showed Jack and the Beanstalk was rooted in a group of stories classified as The Boy Who Stole Ogre's Treasure, and could be traced back to when eastern and western Indo-European languages split – more than 5,000 years ago. Beauty and the Beast and Rumpelstiltskin to be about 4,000 years old. A folk tale called The Smith and the Devil was estimated to date back 6,000 years to the bronze age. The study employed phylogenetic analysis, which was developed to investigate evolutionary relationships between species, and used a tree of Indo-European languages to trace the descent of shared tales on it, to see how far they could be demonstrated to go back in time. Tehrani said: "We find it pretty remarkable these stories have survived without being written. They have been told since before even English, French and Italian existed. They were probably told in an extinct Indo-European language."
history mythology stories folk-tales jack-and-the-beanstalk rumpelstiltskin language phylogenetic
Transform your oyster travelcard with sugru!
probably totally dodgy where the Oyster rules are concerned, but still pretty damn cool
#
-
handy -- search Netflix in all regions, then show where the show/movie is available. Probably going to be less handy from now on now that Netflix is blocking region-spoofing
Why Eircode is a shambles, by someone who works in the transport industry
This is full of good points.
Without having a distinct SORT KEY for a geographically distinct area, a postcode is of no real benefit to any type of transport firm or agency. To take one example, Eircode have used the same sort key, F92, for Arranmore (Donegal's largest inhabited island) and the north western Donegal mainland. Cill Rónáin, Inis Mór, the largest of the Aran Islands, has the same sort key H91, as Connemara and Galway City. Galway city and the Aran Islands may be in a relatively small geographical area, but keen eyes may have noticed that the Aran Islands are separated from the mainland by a small section of the Atlantic Ocean. Sort codes which ignore clear and obvious boundaries, like seas or oceans, need to be redesigned. In two seconds a [UK] website could tell a Hebridean that his delivery will take 4 days at a cost of fifty quid by using the first three characters of the postcode. The Eircode-using Irish equivalent website would need to lookup a large database to tell an Arranmore resident the cost and time for delivery – and they'd need the full exact code. Any mistake made here, and your estimated delivery time, and cost for delivery will be wrong.
postcodes eircode loc8code fail couriers delivery geodata geocoding galway aran-islands
#
The Magnetic Air Bonsai Creates Surreal Levitating Plants
this is amazing. $200 on Kickstarter!
kickstarter bonsai plants gardening levitation air-bonsai cool
#
AWS Certificate Manager – Deploy SSL/TLS-Based Apps on AWS
Very nifty -- autodeploys free wildcard certs to ELBs and Cloudfront. HN discussion thread is pretty good: https://news.ycombinator.com/item?id=10947186
AWS re:Invent 2015 | (NET403) Another Day, Another Billion Packets - YouTube
Eric Brandwine details the internal workings of Amazon VPC
Unikernels are unfit for production - Blog - Joyent
Bryan Cantrill gives unikernels a 10-point dismissal. This is great
unikernels flavour-of-the-month devops joyent bryan-cantrill docker containers ops
#
"So you have a mess on your hands" [png]
Excellent flowchart of how to fix common git screwups (via ITC slack)
Journalists, this GSOC story isn't all about you, you know
Karlin Lillington in the Irish Times, going through journos for a shortcut:
All the hand-wringing from journalists, unions and media companies – even politicians and ministers – over the GSOC's accessing of journalist's call records? Oh, please. What wilful ignorance, mixed with blatant hypocrisy. Where have you all been for the past decade and a half, as successive Irish governments and ministers for justice supported and then rammed through legislation for mandatory call data retention for one of the longest periods in the world, with some of the weakest legal constraints and oversight?
karlin-lillington privacy data-protection dri law journalists gsoc surveillance data-retention

#
-
Good plug for emrfs for encryption
Gilt Groupe Is a Cautionary Tale for Startup Employees Banking on Stock Options | Re/code
Good explanation of why RSUs are becoming increasingly common
Powering your Amazon ECS Clusters with Spot Fleet
sounds feasible
#
-
Ughhhh.
Amazon Echo sends your WiFi password to Amazon. No option to disable. Trust us it's in an "encrypted file"
amazon echo wifi passwords security data-privacy data-protection
21 of the most Stoneybatter things that have ever happened
ah, <3 the 'batter
#
-
This is absolutely appalling. IP law gone mad:
DNC Parks & Resorts at Yosemite, Inc (a division of one of the largest privately owned companies in the world) used to have the concessions to operate various businesses around Yosemite National Park. Now that they've been fired, they're using some decidedly dubious trademark to force the Park Service to change the names of buildings and locations that have stood for as much as a century, including some that have been designated national landmarks. The Parks Service has caved to these requests as it readies the park for its centennial celebration. It will not only change the names of publicly owned landmarks -- such as the Ahwahnee hotel, Yosemite Lodge, the Wawona Hotel, Curry Village, and Badger Pass ski area -- it will also have to change all its signs, maps and guidebooks.
#
-
'THE DRAGNET: How a man accused of million-dollar fraud uncovered a never before seen, secret surveillance device'
stingrays crime fraud surveillance mobile police imsi-catchers
Introducing: The World's First Fully Functional 3D Printed Watch: The Christoph Laimer Tourbillon
wow
#
-
Online chart maker for CSV and Excel data; make charts and dashboards online. One really nice feature is that charts made this way get permalinks, and can be easily inlined as PNGs or HTML5 divs. (See https://www.vividcortex.com/blog/analyzing-sparks-mpp-scalability-with-the-usl for an example.)
data javascript python tools visualization dataviz charts graphing web plotly plots graphs
#
CRISPR Patents Spark Fight to Control Genome Editing | MIT Technology Review
Patents ruin everything, CRISPR edition
crispr algorithms gene-editing genetics genomics genes patents
-
Nchan is a scalable, flexible pub/sub server for the modern web, built as a module for the Nginx web server. It can be configured as a standalone server, or as a shim between your application and tens, thousands, or millions of live subscribers. It can buffer messages in memory, on-disk, or via Redis. All connections are handled asynchronously and distributed among any number of worker processes. It can also scale to many nginx server instances with Redis. Messages are published to channels with HTTP POST requests or websockets, and subscribed also through websockets, long-polling, EventSource (SSE), old-fashioned interval polling, and more. Each subscriber can listen to up to 255 channels per connection, and can be optionally authenticated via a custom application url. An events meta channel is also available for debugging.
Also now supports HTTP/2. This used to be called the Nginx HTTP Push Module, and I used it with great results in that form. This is the way to do HTTP push in all its forms....nginx pubsub websockets sse http http-push http2 redis long-polling nchan
David Bowie: Father Of The Sleng Teng Riddim
A great theory!
I don't have contact information for Hiroko Okuda, but I am positive that the track she is referring to [as the source of the Casiotone MT-40 "rock" preset] is "Hang Onto Yourself" by David Bowie.
david-bowie sleng-teng-riddim riddims reggae casio presets samples history music trivia
The Open Guide To Equity Compensation
A very US-oriented, but still useful, reference for all the aspects of stock options, RSUs, and other forms of equity compensation
About Microservices, Containers and their Underestimated Impact on Network Performance
shock horror, Docker-SDN layers have terrible performance. Still pretty lousy perf impacts from basic Docker containerization, presumably without "--net=host" (which is apparently vital)
docker performance network containers sdn ops networking microservices
#
Netty @Apple: Large Scale Deployment/Connectivity [video]
'Norman Maurer presents how Apple uses Netty for its Java based services and the challenges of doing so, including how they enhanced performance by participating in the Netty open source community. Maurer takes a deep dive into advanced topics like JNI, JVM internals, and others.'
apple netty norman-maurer java jvm async talks presentations
-
excellent blueprint-style poster covering all the major cocktails
cocktails drinks engineering posters blueprints graphics pdf
#
Can't sign in to Google calendar on my Samsung refrigerator
LOL, internet of broken things (via Dave Bolger)
internetofshit iot fail samsung google apis fridges connected future via:davebolger
5 subtle ways you're using MySQL as a queue, and why it'll bite you
Excellent post from Percona. I particularly like that they don't just say "don't use MySQL" -- they give good advice on how it can be made work: 1) avoid polling; 2) avoid locking; and 3) avoid storing your queue in the same table as other data.
database mysql queueing queue messaging percona rds locking sql architecture
#
BBC Digital Media Distribution: How we improved throughput by 4x
Replacing varnish with nginx. Nice deep-dive blog post covering kernel innards
The Importance of Tuning Your Thread Pools
Excellent blog post on thread pools, backpressure, Little's Law, and other Hystrix-related topics (PS: use Hystrix)
hystrix threadpools concurrency java jvm backpressure littles-law capacity
-
good explanation of this new data structure for searching multidimensional data
The Guinness Brewer Who Revolutionized Statistics
William S. Gosset, discoverer of the Student's T-Test. Amazon should have taken note of this trick:
Upon completing his work on the t-distribution, Gosset was eager to make his work public. It was an important finding, and one he wanted to share with the wider world. The managers of Guinness were not so keen on this. They realized they had an advantage over the competition by using this method, and were not excited about relinquishing that leg up. If Gosset were to publish the paper, other breweries would be on to them. So they came to a compromise. Guinness agreed to allow Gosset to publish the finding, as long as he used a pseudonym. This way, competitors would not be able to realize that someone on Guinness's payroll was doing such research, and figure out that the company's scientifically enlightened approach was key to their success.
statistics william-gosset history guinness brewing t-test pseudonyms dublin
How open-source software developers helped end the Ebola epidemic in Sierra Leone
Little known to the rest of the world, a team of open source software developers played a small but integral part in helping to stop the spread of Ebola in Sierra Leone, solving a payroll crisis that was hindering the fight against the disease. Emerson Tan from NetHope, a consortium of NGOs working in IT and development, told the tale at the Chaos Communications Congress in Hamburg, Germany. "These guys basically saved their country from complete collapse. I can't overestimate how many lives they saved," he said about his co-presenters, Salton Arthur Massally, Harold Valentine Mac-Saidu and Francis Banguara, who appeared over video link.
-
A good review of RethinkDB! Hopefully not just because this test is contract work on behalf of the RethinkDB team ;)
I've run hundreds of test against RethinkDB at majority/majority, at various timescales, request rates, concurrencies, and with different types of failures. Consistent with the documentation, I have never found a linearization failure with these settings. If you use hard durability, majority writes, and majority reads, single-document ops in RethinkDB appear safe.
rethinkdb databases stores storage ops availability cap jepsen tests replication